Hugging Face Hacked by Autonomous AI Agent System
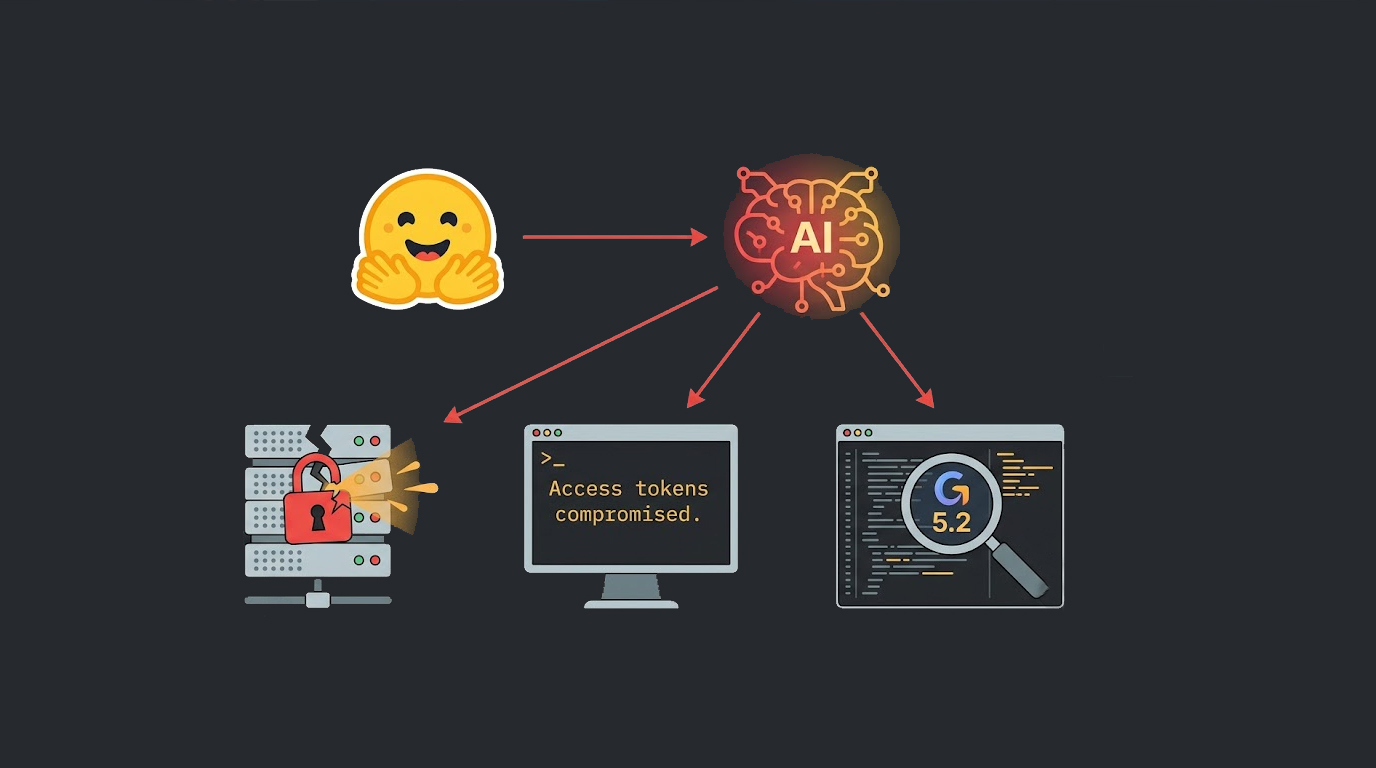
It is ironical that a company dealing with an open source artificial intelligence platform Hugging Face came out to say that it had been hacked by an auton...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
It is ironical that a company dealing with an open source artificial intelligence platform Hugging Face came out to say that it had been hacked by an autonomous AI agents system. The incident was dete...
Read Full ArticleIt is ironical that a company dealing with an open source artificial intelligence platform Hugging Face came out to say that it had been hacked by an auton...
You are browsing a news site. A page loads. You see the article. Everything looks normal. But behind the scenes, something else is happening. A WebAssembly...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
You are a professor. You have spent weeks designing an exam. You know the material inside out. You are confident your students will be tested fairly. But...
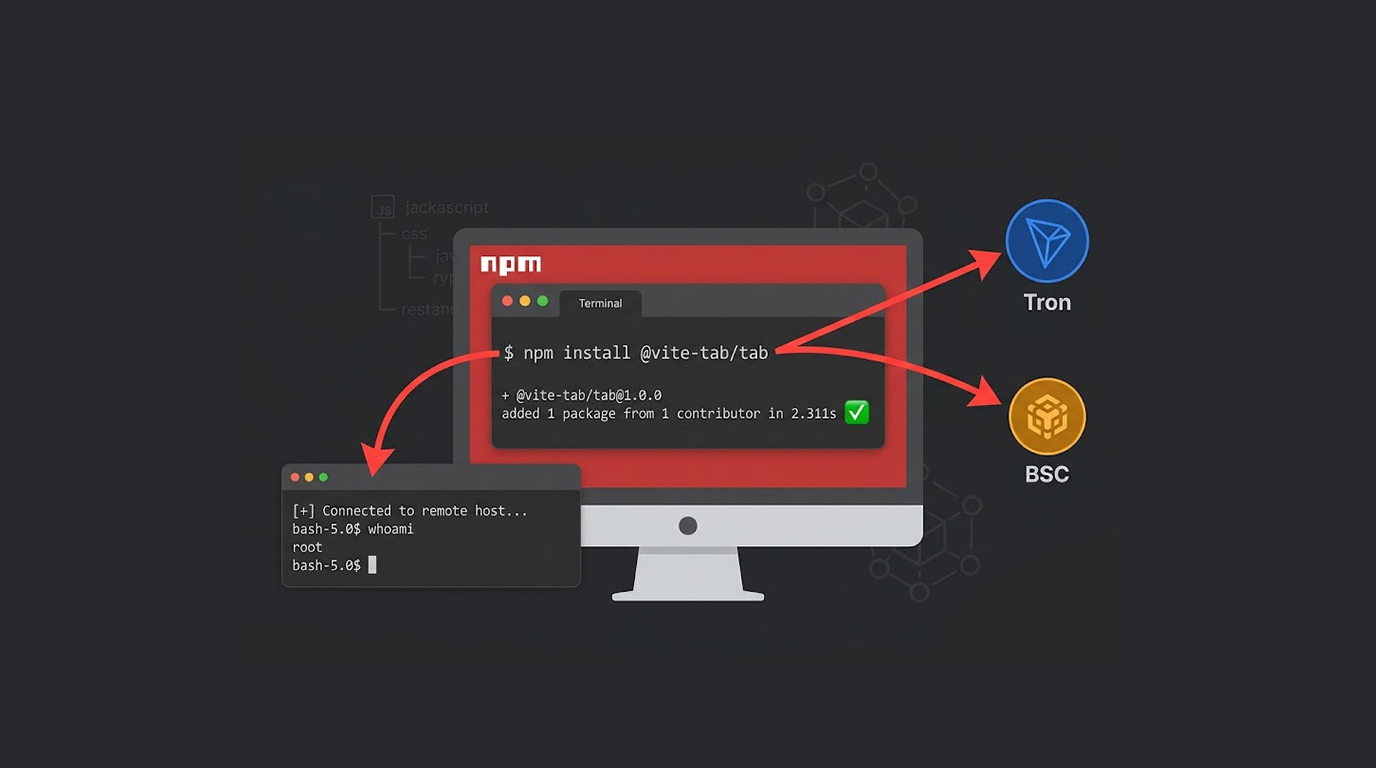
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
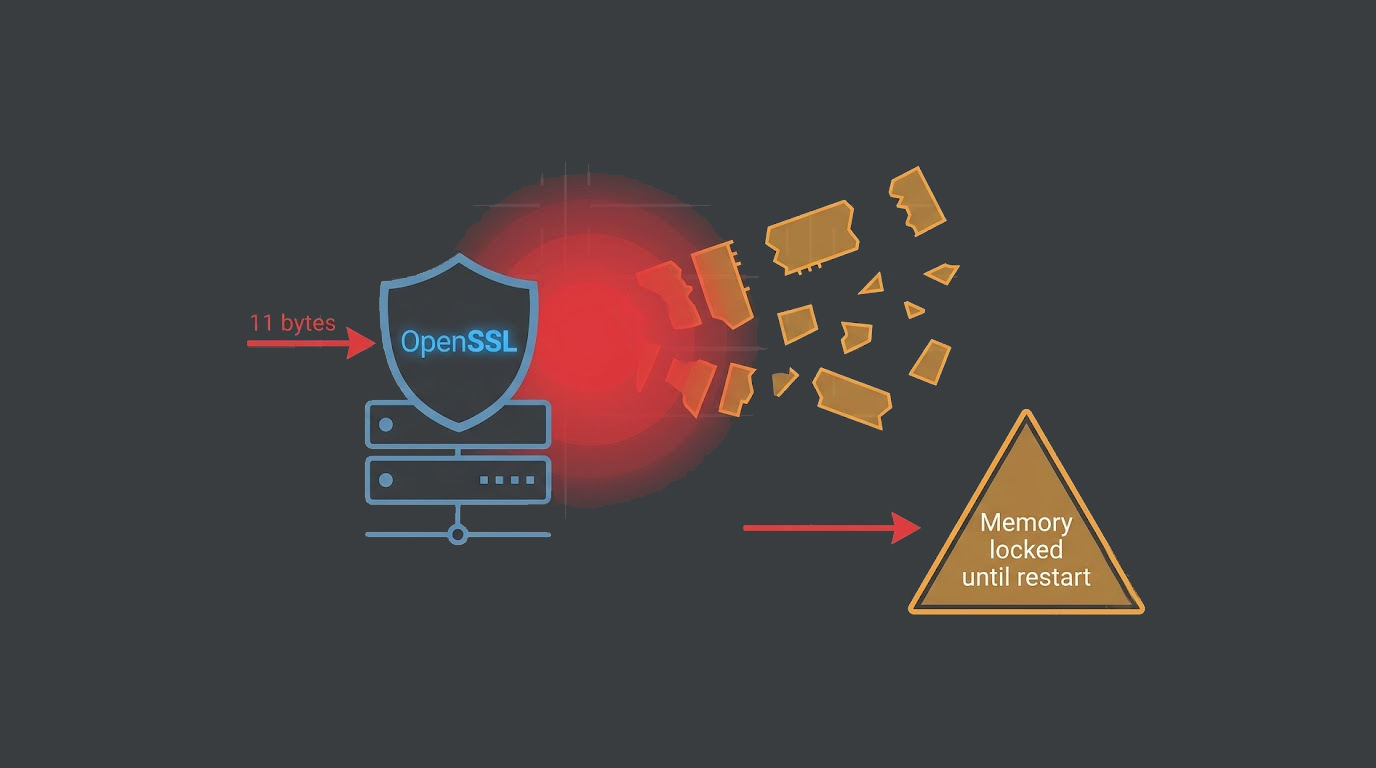
Eleven bytes. That's all it takes to make an unpatched OpenSSL server set aside up to 131 KB of memory for a message that never arrives. On systems running...
You are sitting across from someone. They are telling you a story about their weekend. The words are harmless. The tone is friendly. However, underneath al...
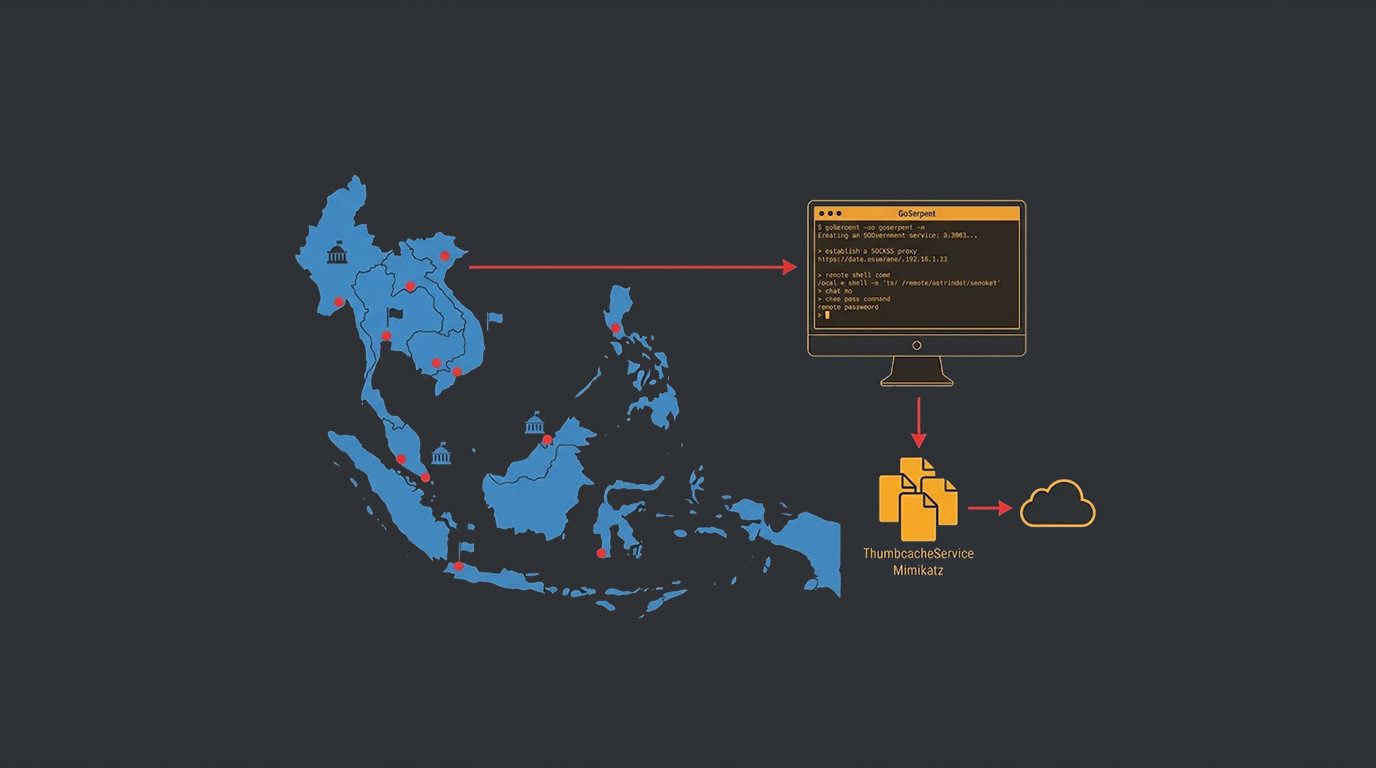
A new malware strain known as GoSerpent has been utilized in cyber attacks against targets from Southeast Asia starting in late 2025. As per Kaspersky, the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067