Malicious npm postinstall Scripts, How They Hide Code
The postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in th...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
The postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in the "postinstall" field of package.json execute...
Read Full ArticleThe postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in th...
Google Looker Studio, formerly Data Studio is a go-to tool for turning data from BigQuery, Sheets, Spanner, Cloud Storage, and dozens of other sources into...
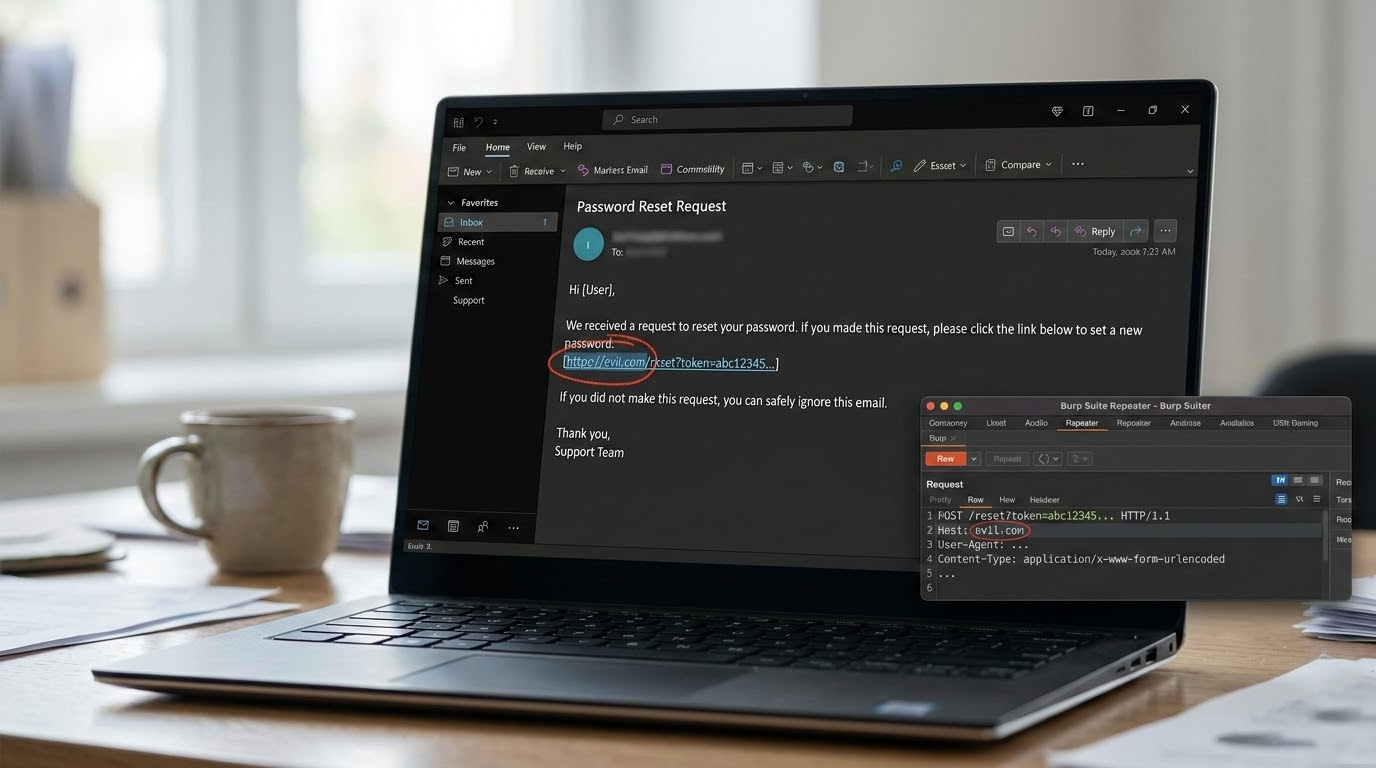
Password reset poisoning (also called Host header poisoning in reset flows) is one of those “old but gold” vulnerabilities that refuses to die....
In 2026, a surprisingly large number of web servers (especially legacy PHP apps, shared hosting environments and misconfigured cloud instances) still leave...
Mailcow; one of the most popular self-hosted, Docker-based mail server suites, patched a nasty vulnerability earlier this year that could let attackers hij...
In 2026, there is still an active known vulnerability on many WordPress sites that have seen extensive exploitation (both public and through Metasploit) an...
In the world of industrial control systems, even small devices can carry outsized risks when a vulnerability slips through. That's exactly the case with CV...
At this moment in March of 2026, hundreds of thousands of cyber attacks happen around the world every hour including instances of malware detection, phishi...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067