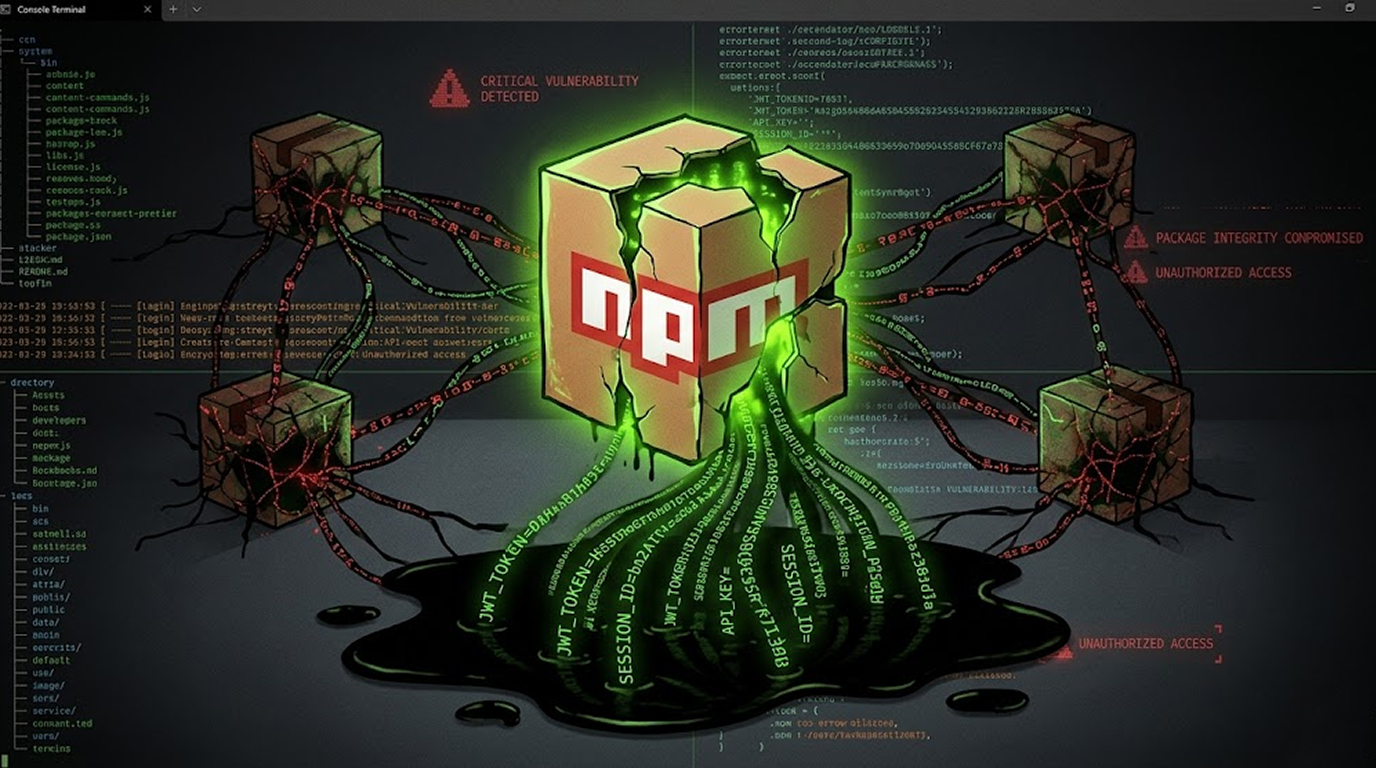
npm Worm Steals Tokens to Poison Open Source Packages
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
Found 389 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
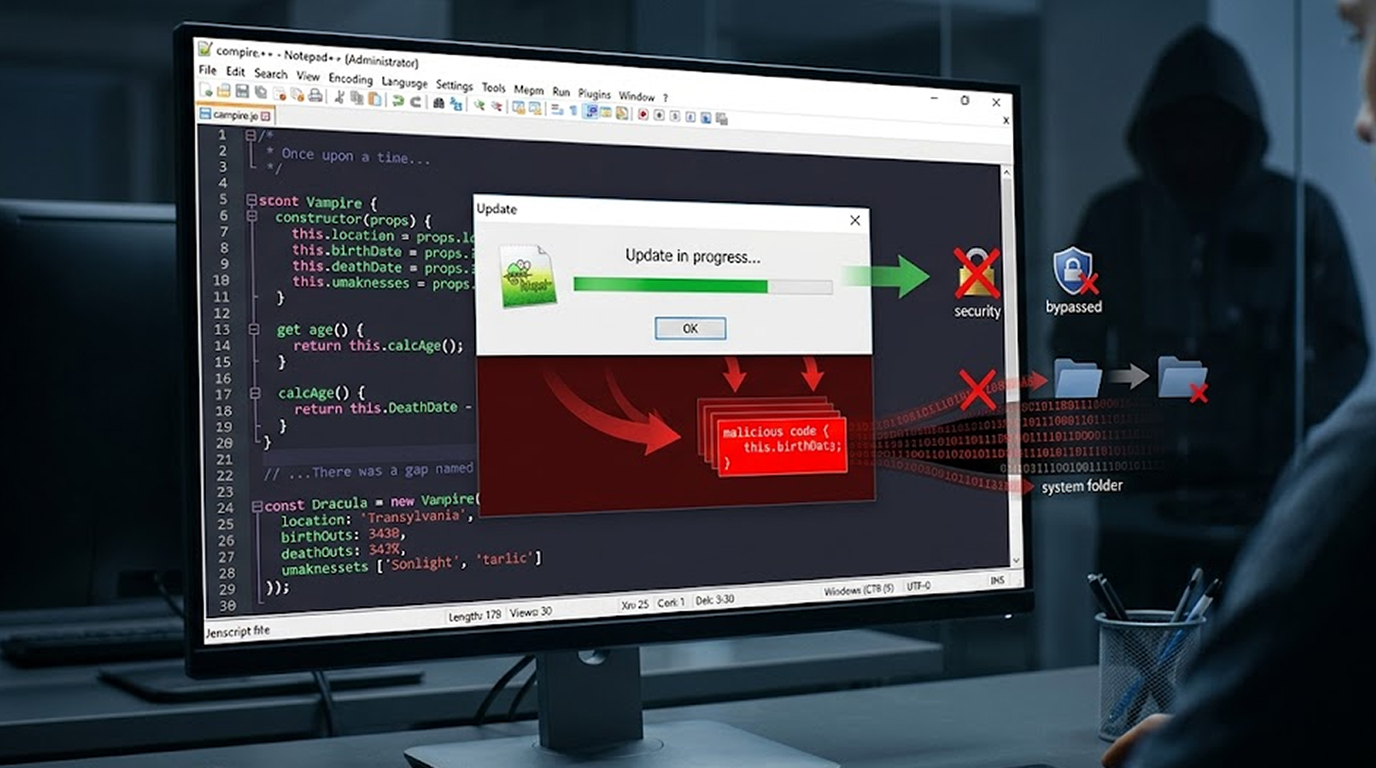
You sit down at your computer. You need to edit a configuration file. You open Notepad++. It has been on your machine for years. Lightweight. Fast. Trustwo...
You have heard of ransomware. Hackers break in, encrypt your files, and demand money. It is bad. But there is a catch: they want you to pay. So they leave...
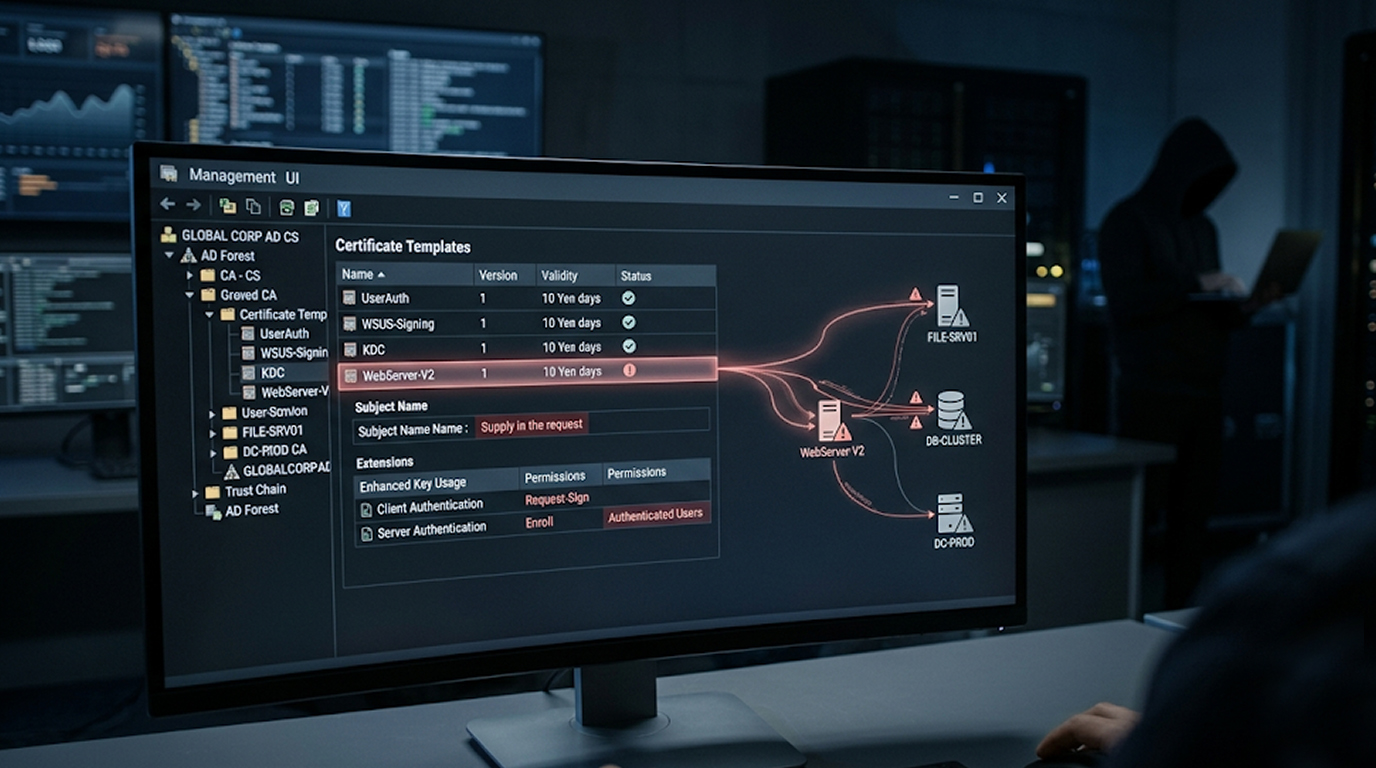
Active Directory Certificate Services (AD CS) is everywhere in enterprise Windows environments. And everywhere means opportunity.If you have done any inter...
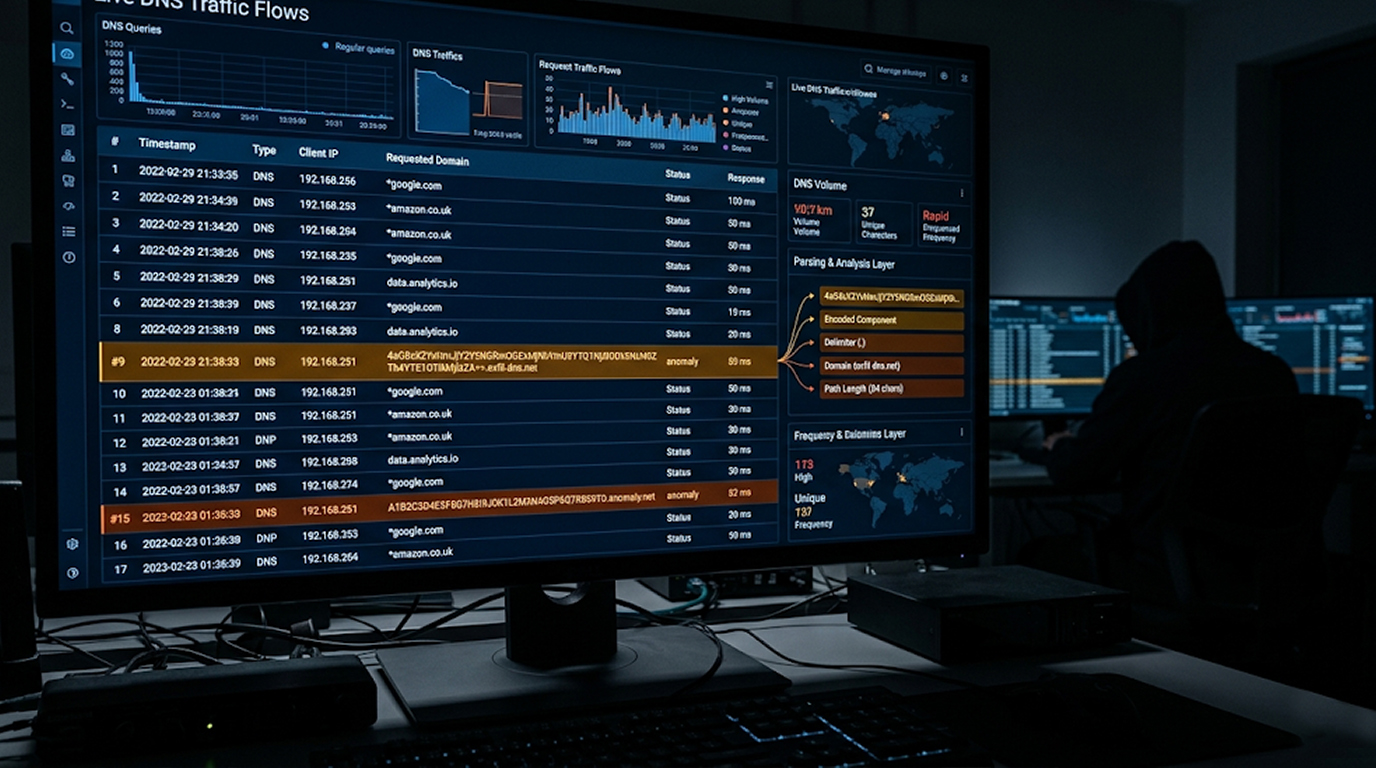
One of the most stealthy ways that attackers have been able to leak sensitive information out of a network is by conducting “DNS exfiltration.”...
PHANTOMPULSE RAT is a newly developed and highly advanced Remote Access Trojan (RAT) that is getting a lot of attention within the cybersecurity community...
Authentication state attacks take advantage of weakness in how applications manage login sequences and states. Rather than using encryption or guessing a p...
As the cybersecurity industry continues to advance at an accelerated pace, new vulnerabilities pose increased potential for both rewards and risk by being...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067