Was the Malware Sample Planted to Mislead You?
There's a question that arrives at some point in almost every serious investigation, usually late at night, and it goes something like this, which is that...
Found 30 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There's a question that arrives at some point in almost every serious investigation, usually late at night, and it goes something like this, which is that...
Scoping sounds like the easy part of incident response, because you already know how to search a filesystem and you already know how to read an audit log,...
There's a moment that separates a stolen credential from a compromised network, and it lasts about five minutes, because that's roughly how long an attacke...
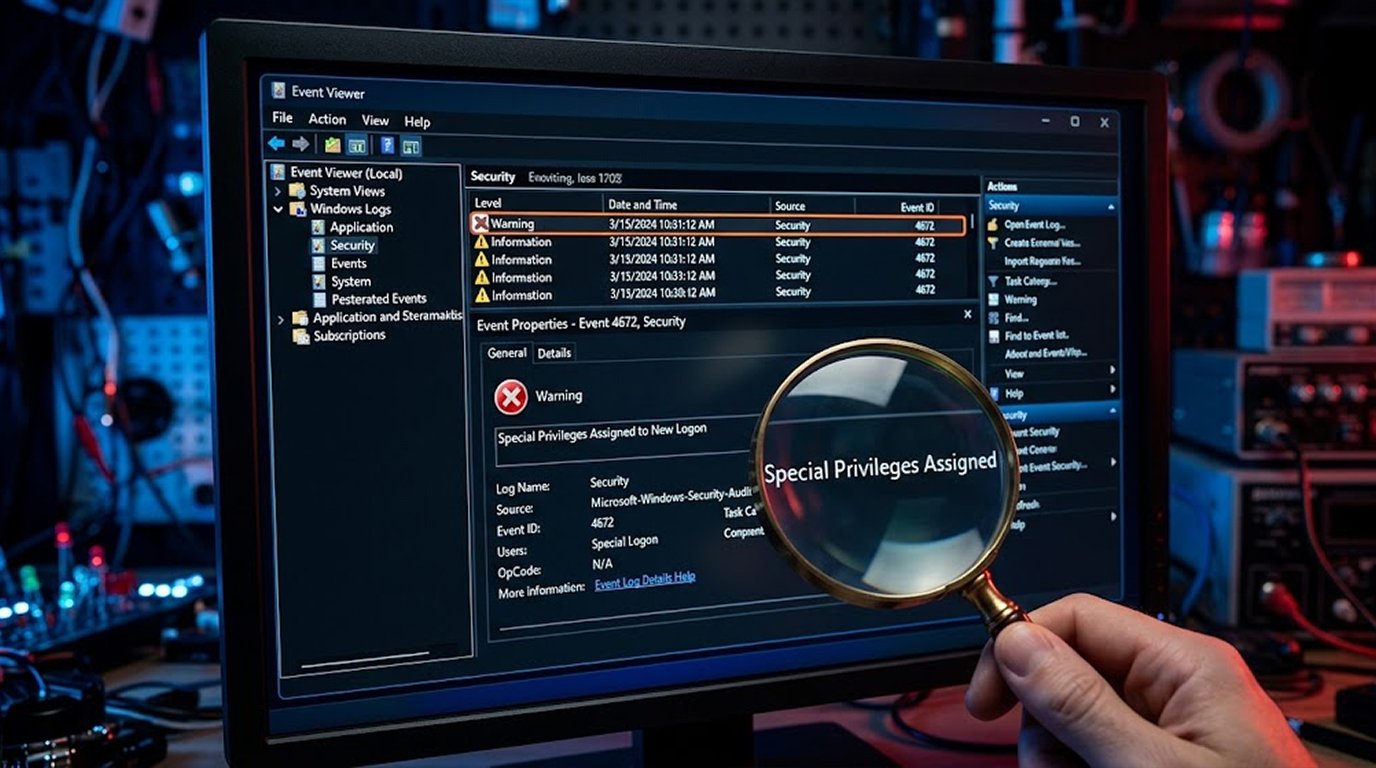
You are sitting there going through your Windows event logs. Everything looks fine. Then you spot it. Event ID 4672. Special privileges assigned to a new l...
Traditional antivirus looks for known signatures. It has a list of bad files and checks every file against that list. If the malware is new, the antivirus...
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
The creation of a hidden local admin account is one of the most effective persistence mechanisms utilized by both malware developers and red team practitio...
Persistence is an essential phase of any kind of red team operation or malware. The payloads will need to survive reboot and user logoffs and other routine...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067