How to Check If Your PHP Version Is Vulnerable
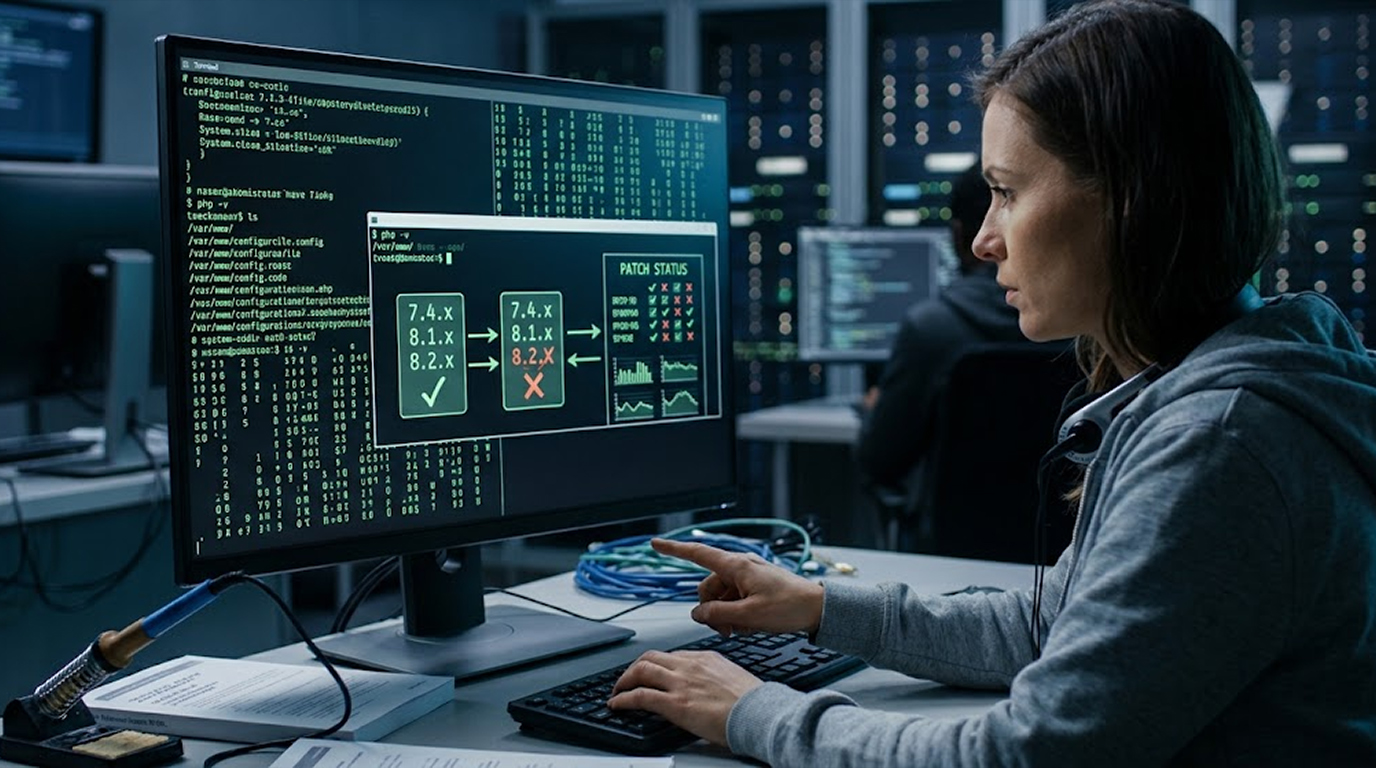
Most site owners think they know their PHP version, because they ran php -v once, saw a number, and assumed that was the answer. It usually is not the ans...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
Most site owners think they know their PHP version, because they ran php -v once, saw a number, and assumed that was the answer. It usually is not the answer, and that gap is where real incidents hap...
Read Full ArticleMost site owners think they know their PHP version, because they ran php -v once, saw a number, and assumed that was the answer. It usually is not the ans...
Your self-managed GitLab server might be accepting remote code execution from anyone who sends the right request, because GitLab just released emergency fi...
Your AI gateway might have handed over cloud keys before you ever imported the package, because the popular LiteLLM Python package was compromised in a sof...
Your server might be running a language runtime that can be exploited by anyone who sends the right request, because PHP just released emergency updates fo...
Your WordPress site might have a new administrator you never created, because unknown attackers breached TeamUpdraft's website and walked away with custome...
You patched the vulnerability, you removed the suspicious file, and you thought the incident was over, then two weeks later the same thing happens again, b...
You ask an AI assistant for a quick PHP snippet, it needs to store some session data, or cache an object, or pass a configuration array between requests, t...
Your website might have been tested by something that never gets tired, never asks for permission, and costs about five dollars a run, because a Chinese-sp...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067