
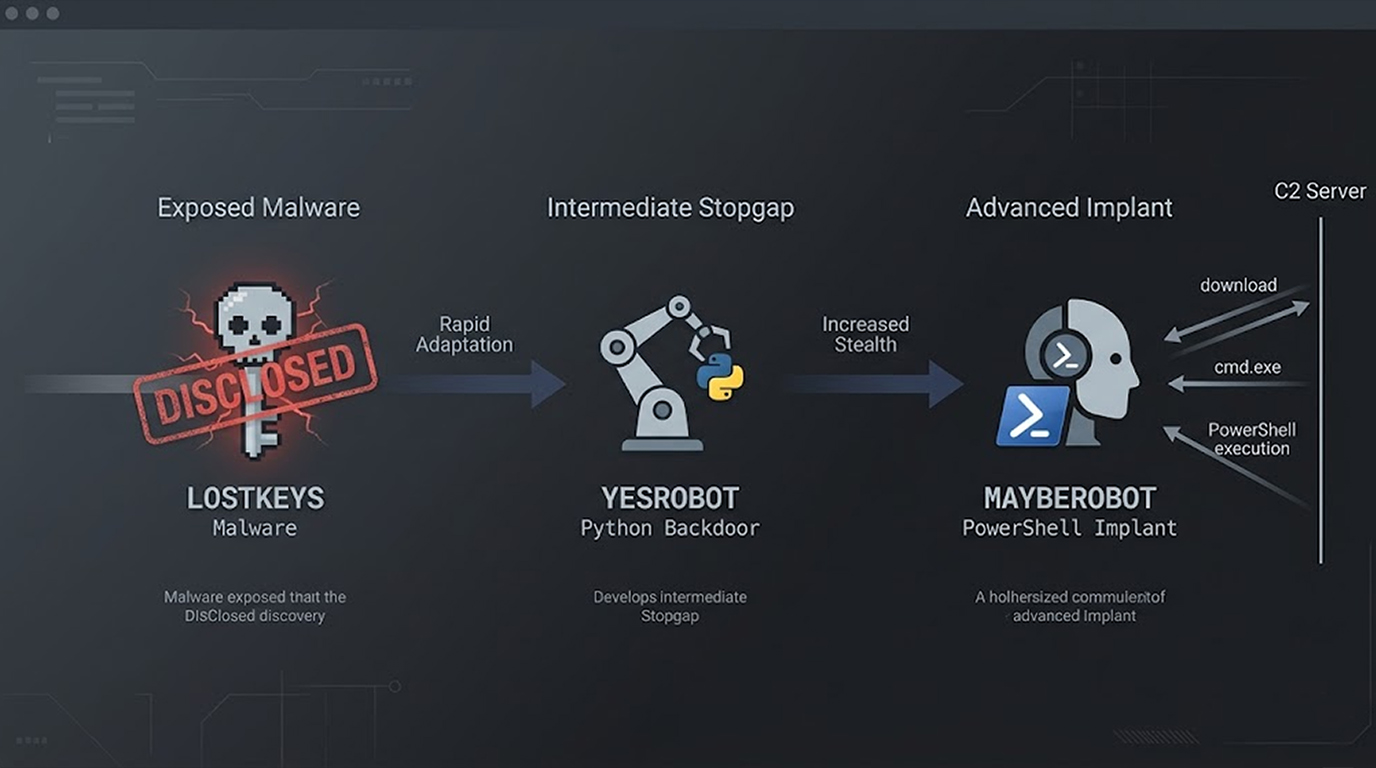
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not the case with COLDRIVER (also known as Star Blizzard, Callisto, or UNC4057), a Russian APT that has been targeting NGOs, governments, and Westerns entities for the purpose of credential theft and espionage.
On May 18, 2025, the Google Threat Intelligence Group (GTIG) published information on LOSTKEYS, which was the main backdoor used by COLDRIVER at that time. In just 5 days afterward, the organization had already transitioned to another tool, first deploying a short-term Python implementation known as YESROBOT, then transitioning to a cleaned up and more versatile PowerShell implementation that they now heavily rely on known as MAYBEROBOT (some vendors refer to it as SIMPLEFIX).
Timeline of rapid evolution of operations
1. Before May 2025: The primary method of using COLDRIVER was via using LOSTKEYS, typically delivered to individuals through ClickFix lures (fake CAPTCHA windows that trick users into running the malware as a result of interacting with it).
2. In May 2025, Google announced the existence of LOSTKEYS, and COLDRIVER ceased using it immediately following that announcement.
3. In Late May 2025, they introduced NOROBOT (a loader sometimes referred to as BAITSWITCH), which drops YESROBOT. YESROBOT is a Python-based backdoor, which required the installation of a complete Python 3.8 runtime on the target system. A complete runtime left behind a "noisy" artifact, which made it easy for the defenders of the system to detect the presence of YESROBOT.
4. Starting in Early June 2025, COLDRIVER abandoned YESROBOT for MAYBEROBOT, a lightweight, extensible PowerShell implant. NOROBOT was also simplified to simply deliver a single logon script that permanently installs MAYBEROBOT.
The rapidity with which COLDRIVER pivots their operations indicates a high level of operational maturity on the part of COLDRIVER as they view any public exposure to their operations as simply a prompt to rapidly iterate on their existing operational capabilities, instead of slowing down due to the public exposure.
What Makes MAYBEROBOT Different (and More Dangerous)
Unlike its Python predecessor, MAYBEROBOT has several advantages:
1. No external dependencies; It runs entirely in PowerShell, which means you don't have to download or install Python (huge issue).
2. Lightweight and extensible; Core is small and allows for a clean, custom C2 protocol.
3. Three primary commands:
a) Download and execute files from a URL.
b) Execute arbitrary commands through cmd.exe.
c) Execute multiple lines of PowerShell code.
4. Two separate channels for command and output; Acknowledgment and result messages flow through separate paths, making it more difficult to associate actions.
5. Persistent through logon script; Simple PowerShell command placed in user's logon script allows MAYBEROBOT to remain after rebooting
In short, MAYBEROBOT is easier to install, harder to identify, and more adaptable for operators that want to issue commands, download other applications, or have long-term access without being detected.
Delivery Chain (Typical Flow)
1. Victim is tricked via a ClickFix-style lure (fake “I am not a robot” CAPTCHA that instructs them to run a command).
2. The lure contains NOROBOT, which is a small DLL (dynamic link library) that runs through the use of rundll32.exe;
3. NOROBOT will find and execute a PowerShell logon script;
4. The PowerShell script will install MAYBEROBOT on the victim's system persistently and will connect to the command and control server (C2).
Also noteworthy is COLDRIVER continues to make adjustments to NOROBOT in order to achieve additional levels of stealth for NOROBOT while keeping MAYBEROBOT stable for use as a legitimate long-term implant.
Why This Is Important
The speed with which COLDRIVER was able to replace the LOSTKEYS- NOROBOT - MAYBEROBOT demonstrates how professional advanced persistent threats (APTs) view public access to the technical descriptions of the code used to facilitate cyber attacks: as a catalyst for rapid evolution and innovation in their tactics, tools and techniques. The change from the original LOSTKEYS noisy Python backdoor to a clean PowerShell backdoor with little or no forensic traces improves operational security for APTs.
For the purpose of establishing operational security, defenders should focus on:
1. Monitoring for unusual PowerShell execution (especially logon scripts and download-execute patterns).
2. Watching for ClickFix-style social engineering lures.
3. Behavioral detection rather than relying solely on known hashes.
MAYBEROBOT is a reminder that when one tool gets burned, sophisticated actors don’t panic, they simply ship the next, leaner version.


