CL-UNK-1211: AI-Powered Linux Espionage Campaign
Unit 42 spent six months watching a cluster they now call CL-UNK-1211 work its way through government Linux servers across multiple regions. The campaign r...
Found 11 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Unit 42 spent six months watching a cluster they now call CL-UNK-1211 work its way through government Linux servers across multiple regions. The campaign r...
Traditional antivirus looks for known signatures. It has a list of bad files and checks every file against that list. If the malware is new, the antivirus...
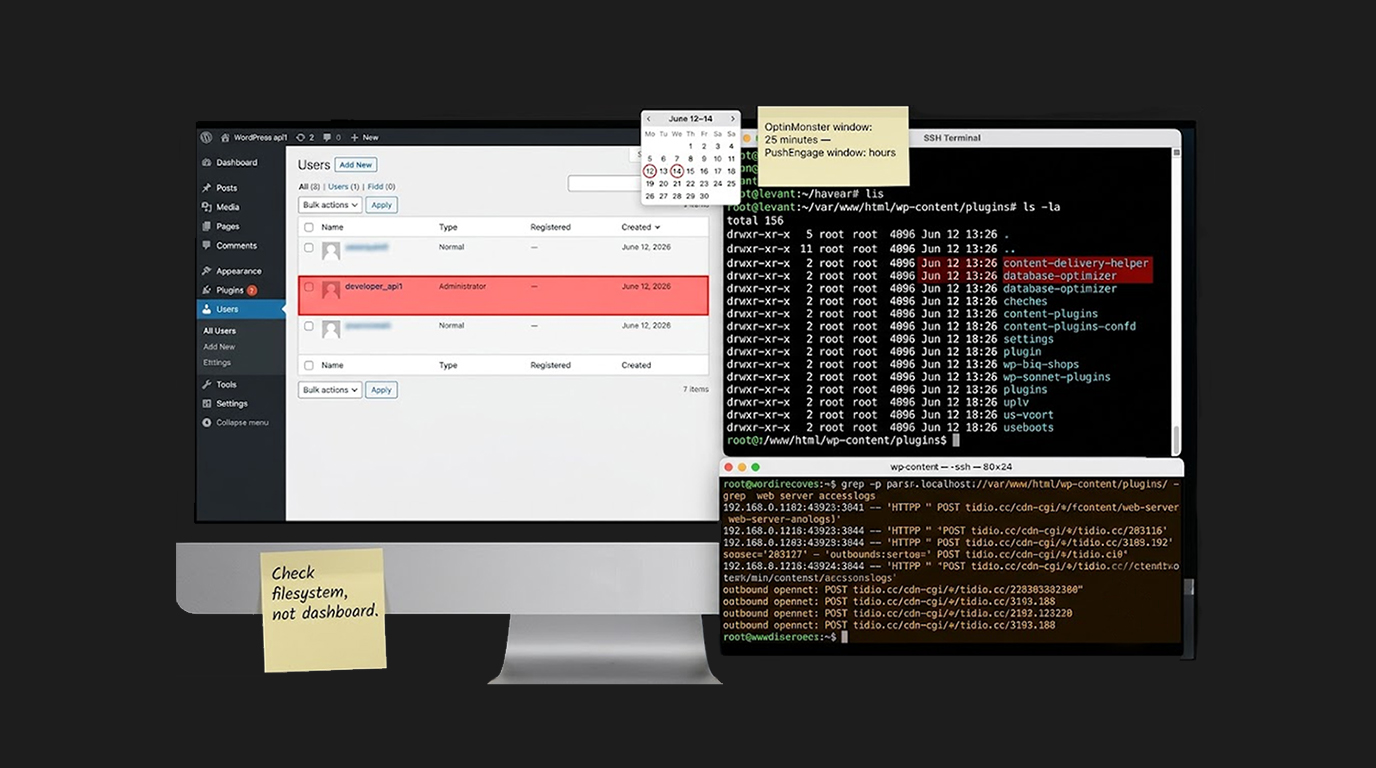
You install PushEngage for push notifications. OptinMonster for popups. TrustPulse for social proof. They are trusted brands. Millions of sites use them.La...
You spend thousands on marketing, you optimize your product pages, you run Facebook ads, you finally see sales rolling in.Then one morning you wake up to a...
You type your SSH password, you press enter, you are logged in, everything seems normal, but someone else just logged in without any password at all, they...
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
In 2026, "Sponge" file manipulation is an evolution of malware that has become increasingly prevalent and dangerous. Unlike traditional ransomware, which l...
When an incident like this happens and your website is down, no way for customers to check out and Google is displaying scary security warnings. In 2025 (a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067