Barracuda ESG Flaw: Root Access With No Login
Barracuda patched two vulnerabilities in its Email Security Gateway on Monday. By Thursday, watchTowr had published a full technical breakdown of how an at...
Found 23 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Barracuda patched two vulnerabilities in its Email Security Gateway on Monday. By Thursday, watchTowr had published a full technical breakdown of how an at...
Unit 42 spent six months watching a cluster they now call CL-UNK-1211 work its way through government Linux servers across multiple regions. The campaign r...
Cybercriminals have found a new way to make money off AI. They're not building their own models or paying for access. They're stealing it. According to re...
Security researchers found a previously undocumented Linux toolkit compiled directly into trojanized HAProxy load balancers. Two South Korean organizations...
When Cisco disclosed CVE-2026-20245 earlier this month, the company acknowledged that it was already aware of exploitation. Now Mandiant has revealed the f...
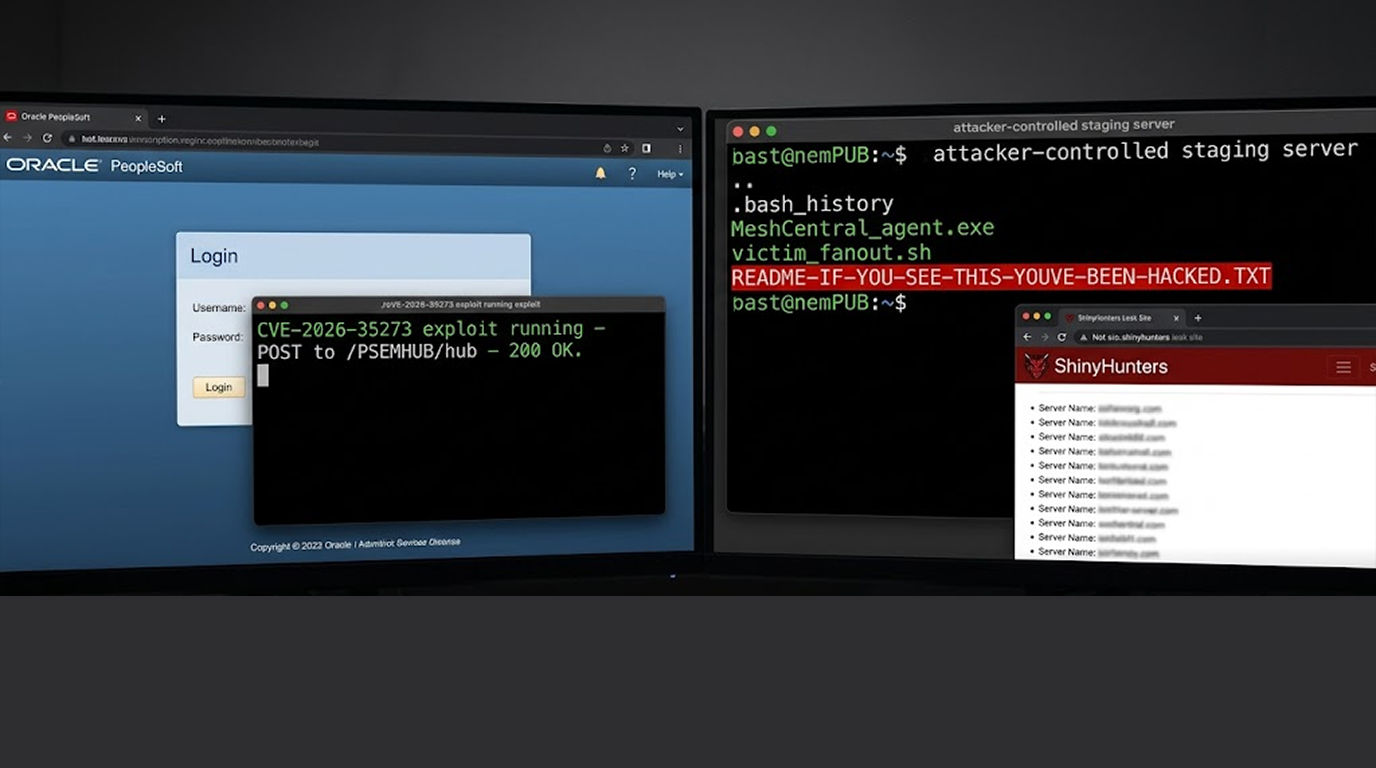
The ShinyHunters extortion crew pulled off something unusual. They exploited an unpatched vulnerability in Oracle PeopleSoft to break into enterprise syste...
You expect phishing emails. You train your team to spot suspicious links. But what happens when the attacker calls you directly and sounds exactly like you...
Vercel has revealed they were exposed to a security breach which enabled unauthorised access to company internal systems because of an employee's Google Wo...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067