Cybercriminals have found a new way to make money off AI. They're not building their own models or paying for access. They're stealing it.
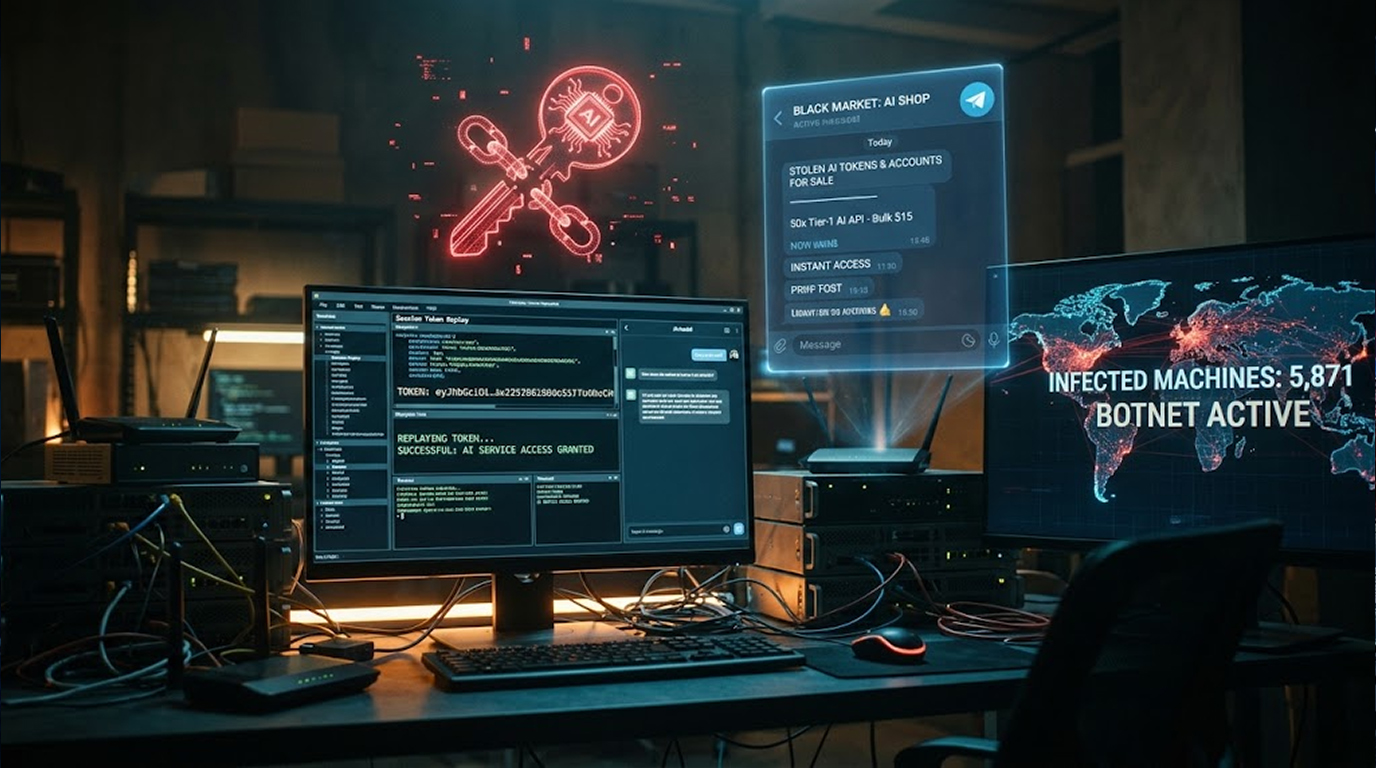
According to reporting from The Hacker News, threat actors are harvesting session tokens and API keys from infected machines and using them to hijack AI accounts from Google, Anthropic, OpenAI, and other providers. The technique is called LLMjacking, and it's growing fast.
The Hacker News covered the findings from Okta's threat intelligence team, which analyzed a massive infostealer dump released on Telegram in August 2026. What they found is concerning.
Let me break down how this works.
Quick Summary
|
What |
Details |
|
Attack Type |
AI account hijacking via stolen tokens |
|
Method |
Infostealer logs, session token replay |
|
Scale |
5,871 infected machines, 162 countries |
|
Targets |
Google, Anthropic, OpenAI, Microsoft, and more |
|
Black Market |
Telegram channels selling AI access |
|
Term |
LLMjacking |
What's Happening?
Infostealers like Lumma Stealer and Vidar are designed to harvest everything from a compromised machine. Credentials. Session tokens. API keys. Anything that looks valuable.
Once that data is stolen, it ends up in stealer logs. Those logs get sold on underground forums and Telegram channels. Buyers use them to launch follow-on attacks.
But here's the twist. Threat actors aren't just after passwords anymore. They're specifically hunting for session tokens and API keys tied to AI services.
"Session tokens and API keys are sought specifically by threat actors because it is often possible to replay those secrets and bypass credential-based authentication," said Jeremy Kirk, director of threat intelligence at Okta, in a report shared with The Hacker News.
"Once successfully replayed, a threat actor is effectively logged in to an LLM service without actually logging in. Use of these skeleton keys makes abuse more challenging but not impossible to detect."
The Scale of the Problem
Okta analyzed a 7 GB infostealer dump released on Telegram on August 2, 2026. What they found:
|
Metric |
Number |
|
Infected machines |
5,871 |
|
Countries affected |
162 |
|
Unique JWTs |
44,791 |
|
AI-related JWTs |
555 |
|
Authentication-related JWEs |
2,937 |
|
Unexpired JWTs and JWEs |
1,843 |
|
JWTs with plaintext PII |
17.7% |
The dump contained tokens for Google, Microsoft, Anthropic, Amazon, Gamma, Notion, Character.ai, Cursor, Poe.com, and Pika AI.
Most of the JWEs were set by OpenAI, which uses NextAuth.js. While these encrypted tokens can only be decrypted by the party holding the key, they can still be replayed if they haven't expired.
"The stolen data is a goldmine for attackers," The Hacker News noted in its coverage.
Why Session Tokens Are So Dangerous
A valid session token is like a skeleton key. It bypasses username and password checks. It bypasses multi-factor authentication. It just works.
What Attackers Can Do:
- Log in as the victim without credentials
- Access AI services without paying
- Use the victim's account for malicious purposes
- Rack up charges on the victim's bill
Why It's Hard to Detect:
- The login looks legitimate
- No password is entered
- No MFA prompt is triggered
- The session appears normal
"This is another problematic aspect since that information does not expire or disappear, and it directly links a user with a specific service, which could be useful for social engineering attempts or phishing," Kirk said.
What Is LLMjacking?
LLMjacking is the term for using stolen API keys or session tokens to access large language models without authorization.
The Concept in Action:
- Attacker hacks API key or session token
- Attacker uses the stolen key/token to access AI services
- Attacker performs queries, produces content, or develops applications
- Victim pays for the usage
What Makes it Attractive:
- AI access at premium prices
- Free access to stolen accounts
- Victims have to pay the bill
- Difficult to trace back to the attackers
The technique is quite similar to cryptojacking, in which attackers use a victim’s computing resources for mining cryptocurrencies. However, in this case, they use the AI compute.
The Black Market for AI Access
Okta found Telegram channels selling access to AI services at discounted prices. Some even offer 24/7 support and money-back guarantees.
What's Being Sold:
- Claude access
- Cursor access
- ChatGPT access
- Gemini access
- Access to specific models like Opus 4.8, Opus 4.7, and Sonnet 4.6
The Tools:
"Accessing accounts using stolen session data requires specific tooling," Okta said. "So-called 'anti-detect' browsers have features designed to use stolen authentication data and avoid security controls."
Anti-detect browsers like Camoufox and automation tools like SeleniumBase can load stolen session data from a file. They also let users configure proxies to bypass "impossible travel" detections.
What Google Is Seeing
Google's Threat Intelligence Group confirmed that the market for stolen AI accounts is growing.
"We have observed more personas seeking to purchase AI-related accounts and more sellers advertising these accounts," Google said.
In one incident response engagement handled by Google's Mandiant team, a threat actor gained initial access to a victim's cloud environment through an exposed GitHub Personal Access Token. They used it to deploy unauthorized AI infrastructure and scale high-performance compute resources.
"The cost of premium model access and high-performance compute is one of the primary barriers for threat actors seeking to operationalize AI," Google said. "This has resulted in increased targeting, exfiltration, and sale of AI accounts across cybercrime communities."
What You Should Do
1. Monitor for Session Token Reuse
Watch for logins from unusual locations or devices. Session token replay often shows up as "impossible travel" or unexpected access patterns.
2. Scope API Keys
Limit what each API key can do. Don't give a single key access to everything.
3. Use Short-Lived Tokens
OAuth 2.0 flows with short-lived tokens expire quickly. If a token is stolen, it becomes useless fast.
4. Enable Device Bound Session Credentials
Google has added support for DBSC in Chrome. This cryptographically links a session token to a device, so a stolen token can't be used elsewhere.
5. IP Allow Listing
This session replay attack can be resolved by allowing access only to certain IP addresses or blocks.
6. Training Users
Infostealers could get into the system through phishing or social engineering. The staff should be trained to recognize infostealers.
Conclusion
AI-powered account hijacking is more common now than ever before. Hackers are taking advantage of session tokens and API keys from infected machines to access premium AI services for free. This process is known as LLMjacking, which has led to the development of an underground economy for accessing AI services.
What You Need to Know
|
Key Point |
Detail |
|
Attack Type |
AI account hijacking via stolen tokens |
|
Method |
Infostealer logs, session token replay |
|
Scale |
5,871 infected machines, 162 countries |
|
Targets |
Google, Anthropic, OpenAI, Microsoft |
|
Black Market |
Telegram channels selling AI access |
|
Term |
LLMjacking |
What You Need to Do
- Watch out for session token reuse
- Scope API keys
- Use short-lived tokens
- Implement Device Bound Session Credentials
- Use IP allowlisting
- Educate end users
FAQ Section
What is LLMjacking?
LLMjacking is using stolen API keys or session tokens to access large language models without authorization. The attacker gets free AI access, and the victim gets the bill.
How do hackers gain access to AI accounts?
They leverage infostealers to get session tokens and API keys. This information is sold at underground forums and Telegram channels.
What is a session token?
A session token is a very small piece of data that authenticates your login. If an attacker gets access to it, he can login on your behalf without your credentials.
Can anything be done by MFA to prevent this from occurring?
Nothing, since this kind of attack does not need any password or other means of authentication, hence no use of MFA here.
What measures can I take to guard against this threat?
Monitor login attempts, scope API keys, use short-lived tokens, and implement Device Bound Session Credentials.