Open VSX Attack Delivers GlassWorm via Compromised Extensions
According to Cybersecurity firm Socket, a sneaky supply chain compromise on the Open VSX Registry (the open-source alternative to Microsoft's VS Code exten...
Found 104 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
According to Cybersecurity firm Socket, a sneaky supply chain compromise on the Open VSX Registry (the open-source alternative to Microsoft's VS Code exten...
Steganography conceals information within "normal" or "harmless" files (images, audio, or video) and makes it difficult to tell there is a secret hidden wi...
With parental controls in place, families can set limits on their kids’ screen time, filter out inappropriate content, keep track of their kids&rsquo...
Ethical hacking can only be conducted legally and safely. Building a home lab allows you to establish a safe and legal environment to simulate attacks, dev...
Most people worry about stolen files or hacked accounts.Very few worry about their camera or microphone.That is exactly why these are abused.When a camera...
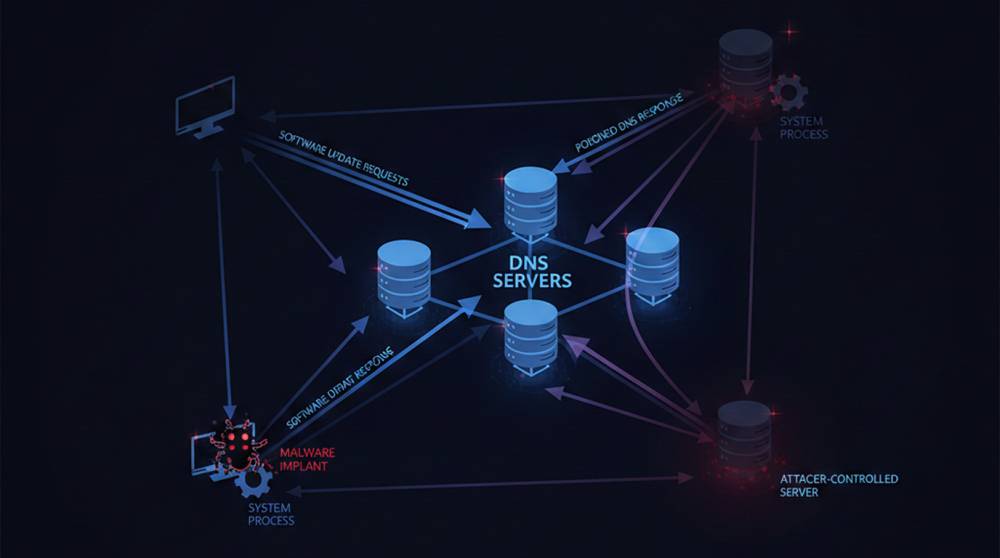
A China-linked advanced persistent threat group has been linked to a sophisticated cyber espionage campaign that weaponized poisoned Domain Name System (DN...
Researchers specializing in cyber security have found a new version of MacSync, an information-stealing application for Macs, which has been created using...
Apple has released security updates across iOS, iPadOS, macOS, tvOS, watchOS, visionOS, and Safari to fix two zero-day vulnerabilities in WebKit, the engin...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067