Notepad++ Backdoor Supply Chain Attack: Full Breakdown
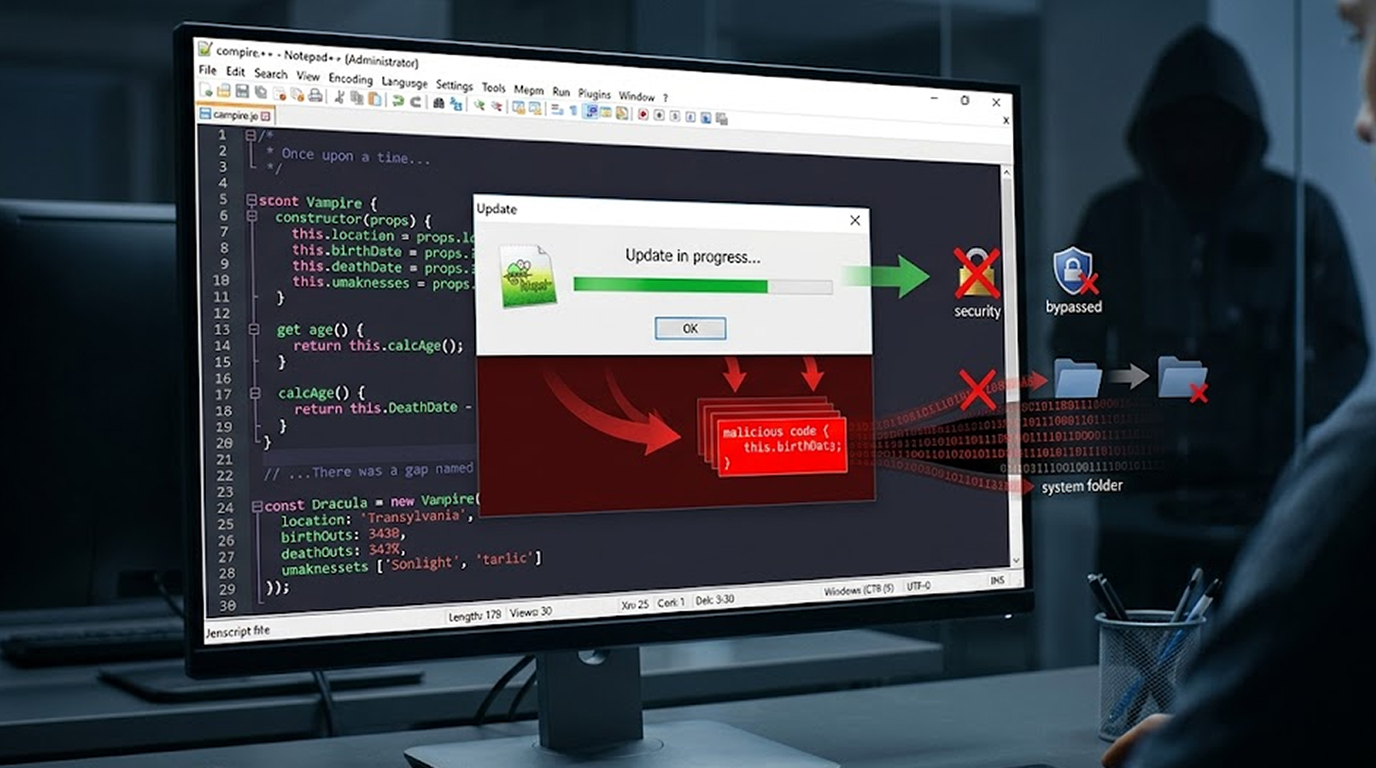
You sit down at your computer. You need to edit a configuration file. You open Notepad++. It has been on your machine for years. Lightweight. Fast. Trustwo...
Found 113 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You sit down at your computer. You need to edit a configuration file. You open Notepad++. It has been on your machine for years. Lightweight. Fast. Trustwo...
ZionSiphon malware is a specialized Operational Technology (OT) malware designed to sabotage water treatment and desalination facilities According to a rep...
There is an increase in supply chain attacks against open-source packages in 2026. Hackers or other malicious actors will either publish or compromise pack...
Local File Inclusion (LFI) is flagged as a high-severity vulnerability within the Madara Theme for Wordpress that permits unauthenticated attackers to read...
Lack of adequate secret management processes continues to create problems for businesses along the lines of breaches of sensitive data and challenges invol...
One of the smartest and most satisfying defensive tricks is turning an attacker’s own reconnaissance against them. Instead of just closing exposed ba...
The postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in th...
In 2026, the most damaging attacks rarely rely on exotic zero-days or nation-state tools. They exploit the same simple, long-standing gaps that companies k...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067