How Attackers Discover and Exploit Shared Credentials in Cloud Environments
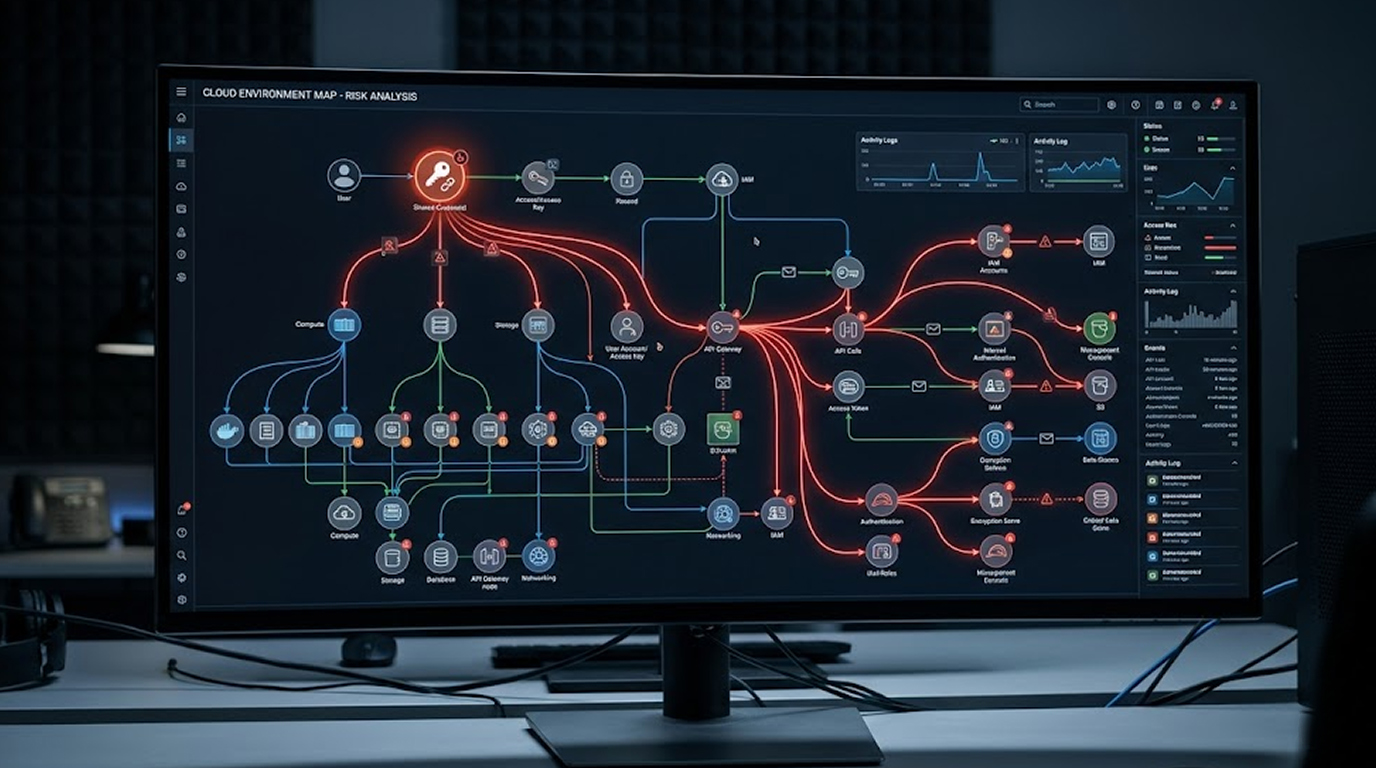
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
Found 173 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
Every year fraud can lead to losses from Business Email Compromise, bogus invoices, diversion of settlements, Smishing, and internal theft of tens of thous...
In March 2026, a threat actor aligned with Iran has conducted password-spraying attacks on Microsoft 365 accounts located in both Israel and the United Ara...
When an incident like this happens and your website is down, no way for customers to check out and Google is displaying scary security warnings. In 2025 (a...
Your website is down. Customer data is leaking. Orders have stopped. Google has flagged your site as unsafe. For thousands of small-to-medium businesses an...
Cybersecurity researchers at Huntress have raised the alarm about a fast-moving device code phishing campaign that is actively targeting Microsoft 365 acco...
Ransomware is familiar. It locks files, demands payment, and disrupts operations.Most organizations now have at least a basic plan to deal with it. Wiper...
During this tax season, Microsoft is alerting both individuals and companies about increased numbers of highly sophisticated phishing attacks that are aime...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067