36 Malicious Strapi Plugins Found on npm Registry
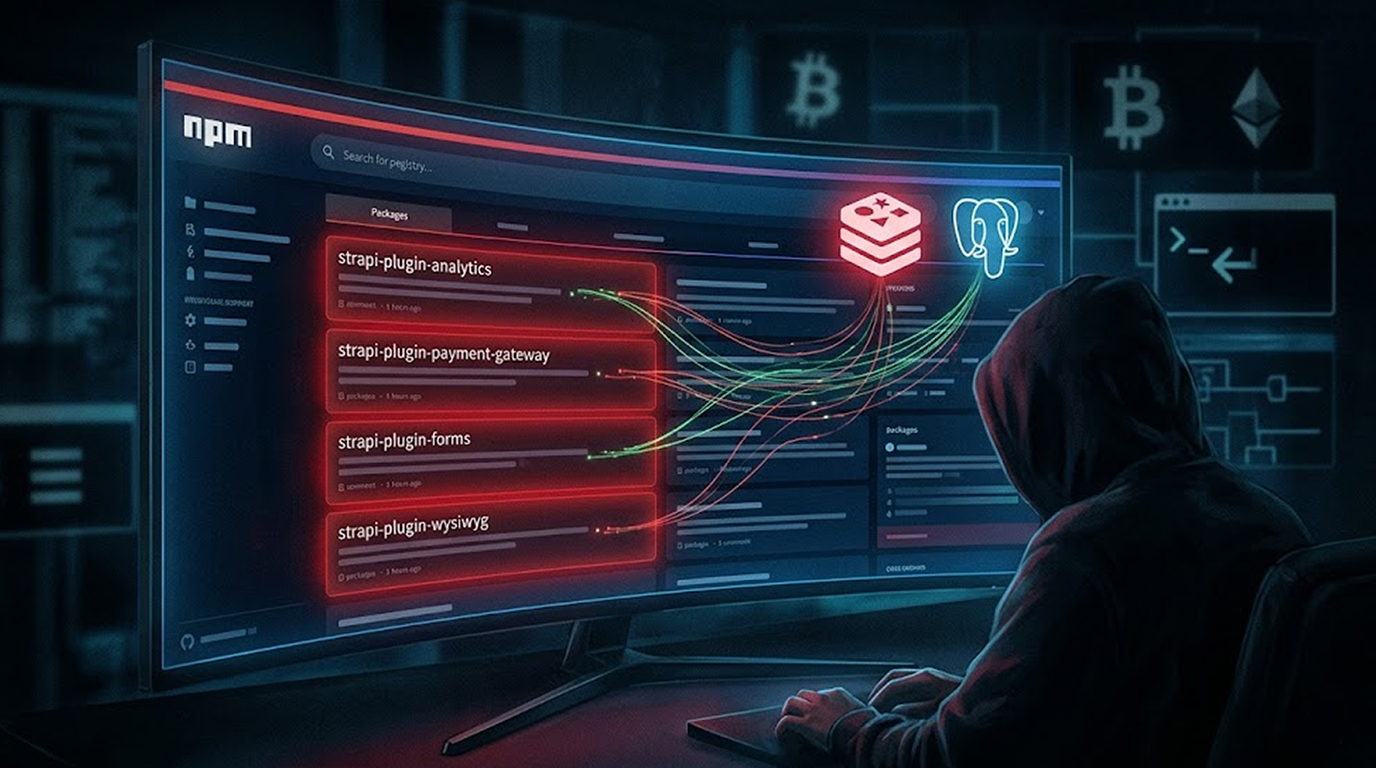
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
Found 1023 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
DarkSword is an advanced iOS spying framework that has been in use to conduct highly targeted attacks since late in 2025. DarkSword is so dangerous because...
An operation, codenamed REF1695, that has been financially motivated and active quietly since November 2023. In its use of fake software installers to deli...
According to cybersecurity investigations into an active attack on government organisations in Southeast Asia, there was a zero-day vulnerability in TrueCo...
In 2026, the borders which had once separated different areas of cybercrime from government sponsored spying and that of cyber warfare is becoming less dis...
In 2026, the loud, noisy attacks that light up every alert in your EDR and SIEM are becoming less common among sophisticated actors. The new gold standard...
Palo Alto Networks Unit 42 discovered a major vulnerability in Google Cloud's Vertex AI that could concern legitimacy of artificial intelligence (AI) agent...
Your website is down. Customer data is leaking. Orders have stopped. Google has flagged your site as unsafe. For thousands of small-to-medium businesses an...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067