npm Worm Steals Tokens to Poison Open Source Packages
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
Found 60 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
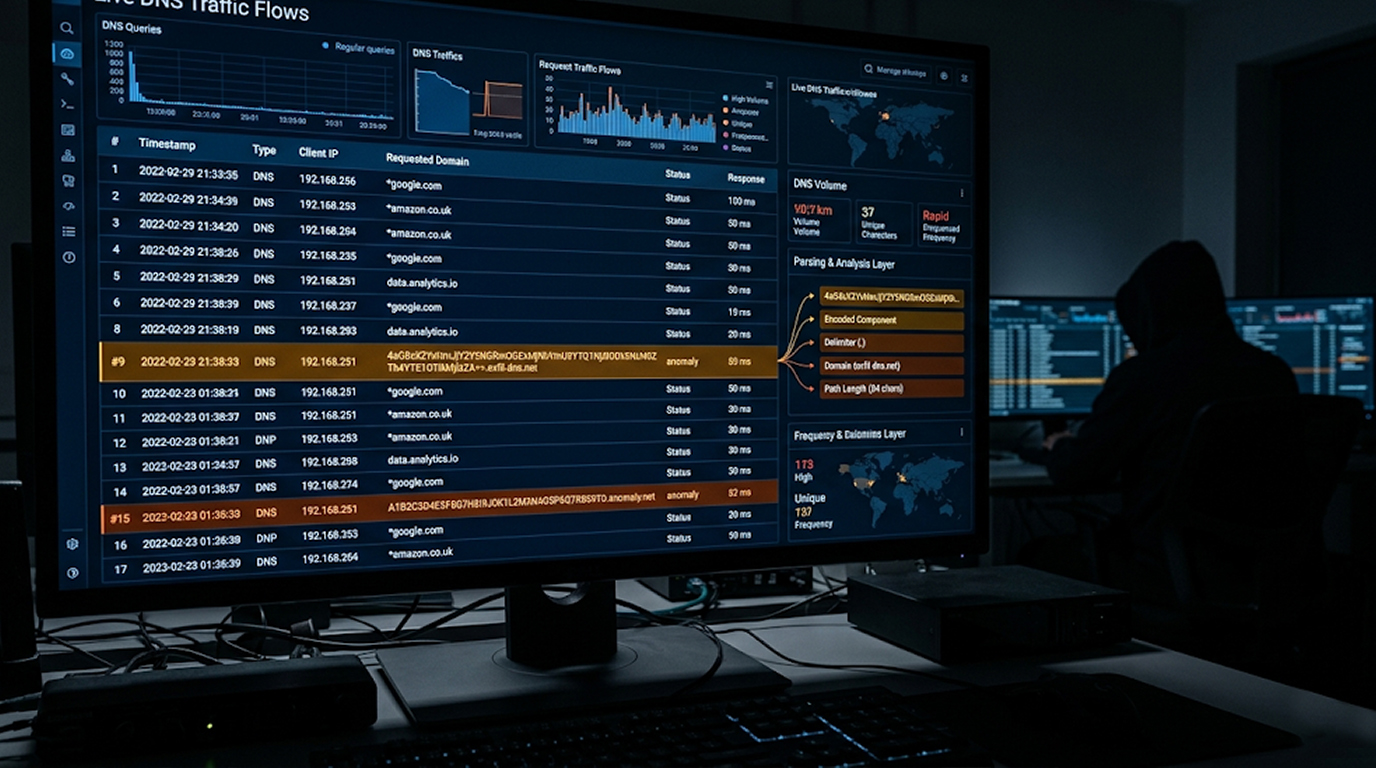
One of the most stealthy ways that attackers have been able to leak sensitive information out of a network is by conducting “DNS exfiltration.”...
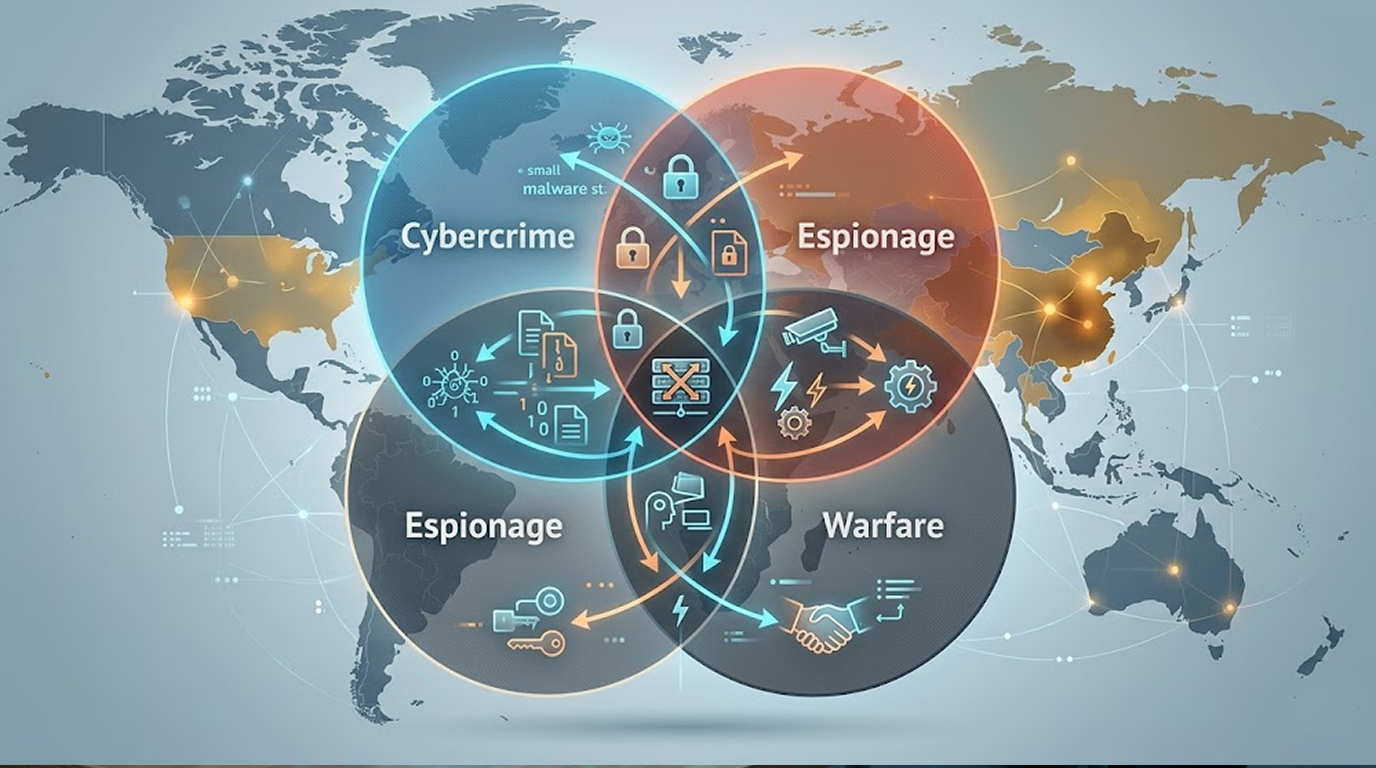
In 2026, the borders which had once separated different areas of cybercrime from government sponsored spying and that of cyber warfare is becoming less dis...
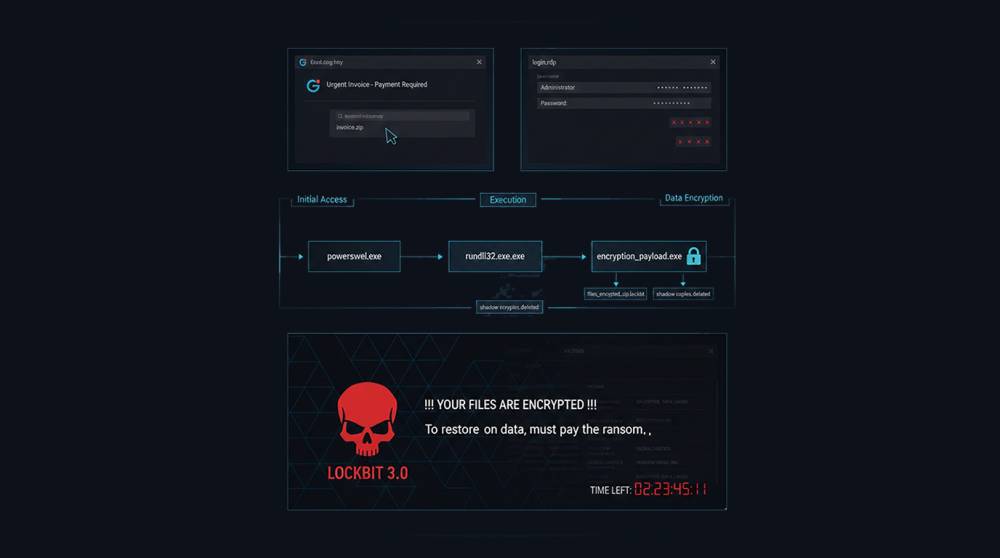
Ransomware used to be simple: encrypt your files, demand payment, and (hopefully) give you the decryption key. That model is now outdated. In 2026, almost...
Sponge-style malware, the quiet, patient threats that slowly soak up credentials, documents, browser data, and session tokens is already a serious problem...
Most organizations have a WAF and firewall, but a surprising amount of malicious traffic still slips through because the rules are either too generic or fo...
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
The Microsoft Defender team has issued an explicit alert that, for many years, malware has been a threat to Windows computer users; however, starting in la...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067