When Hackers Use Your Own Browser Session Against You
There’s this weird trend happening lately in cyber attacks and honestly, it catches people off guard because it doesn’t look like anything is w...
Found 33 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There’s this weird trend happening lately in cyber attacks and honestly, it catches people off guard because it doesn’t look like anything is w...
Attackers don’t waste time on fancy zero days unless they really need to. Most of the active exploitation you see today comes from old, unpatched, ea...
Session hijacking happens when an attacker takes over your active online session. This gives them access to your accounts without needing your password. Th...
As businesses and individuals increasingly rely on cloud services, cybercriminals have found new ways to exploit misconfigured security settings and stolen...
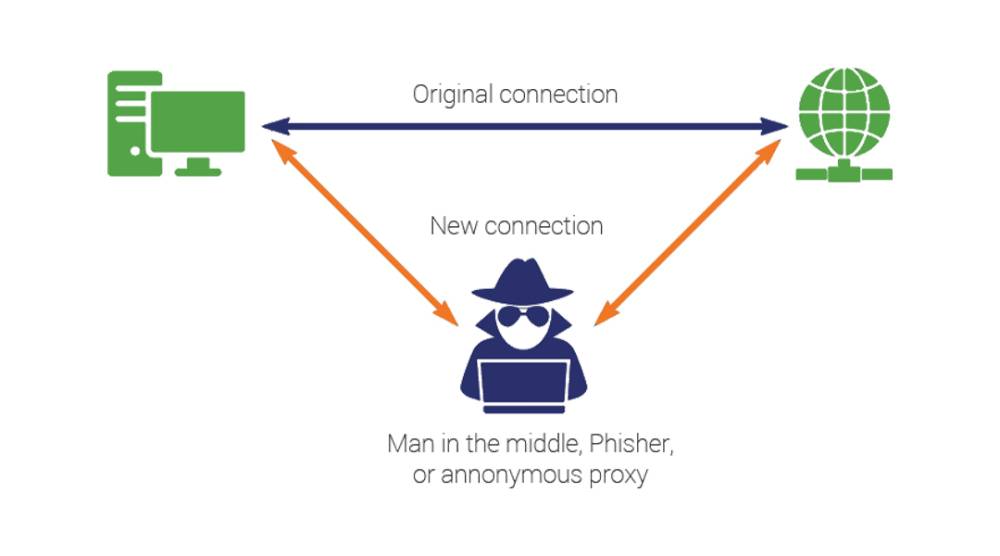
A Man-in-the-Middle (MITM) attack occurs when a hacker secretly intercepts and potentially alters the communication between two parties. This attack can co...
Session cookies play a key role in keeping you logged into websites, storing temporary information that maintains your session as you browse. Unfortunately...
Man-in-the-Middle (MitM) attacks are a dangerous type of cyberattack where an attacker secretly intercepts and possibly alters the communication between tw...
Cross-Site Scripting (XSS) attacks are among the most common and dangerous types of security vulnerabilities found in web applications. XSS attacks occur w...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067