Anthropic Accidentally Leaks Claude Code Source Code
Anthropic has acknowledged there were human errors made which caused the accidental publishing of a significant section of Claude Source Code via an open-s...
Found 529 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Anthropic has acknowledged there were human errors made which caused the accidental publishing of a significant section of Claude Source Code via an open-s...
When you receive a “login from an unusual location” alert, whether from Google, Microsoft, Apple, your bank, or a crypto exchange, it’s e...
A China-based cybercriminal group known as Silver Fox (also referred to as SwimSnake / Valley Thief / Void Arachne) is currently using a typosquatting tech...
Your website is down. Customer data is leaking. Orders have stopped. Google has flagged your site as unsafe. For thousands of small-to-medium businesses an...
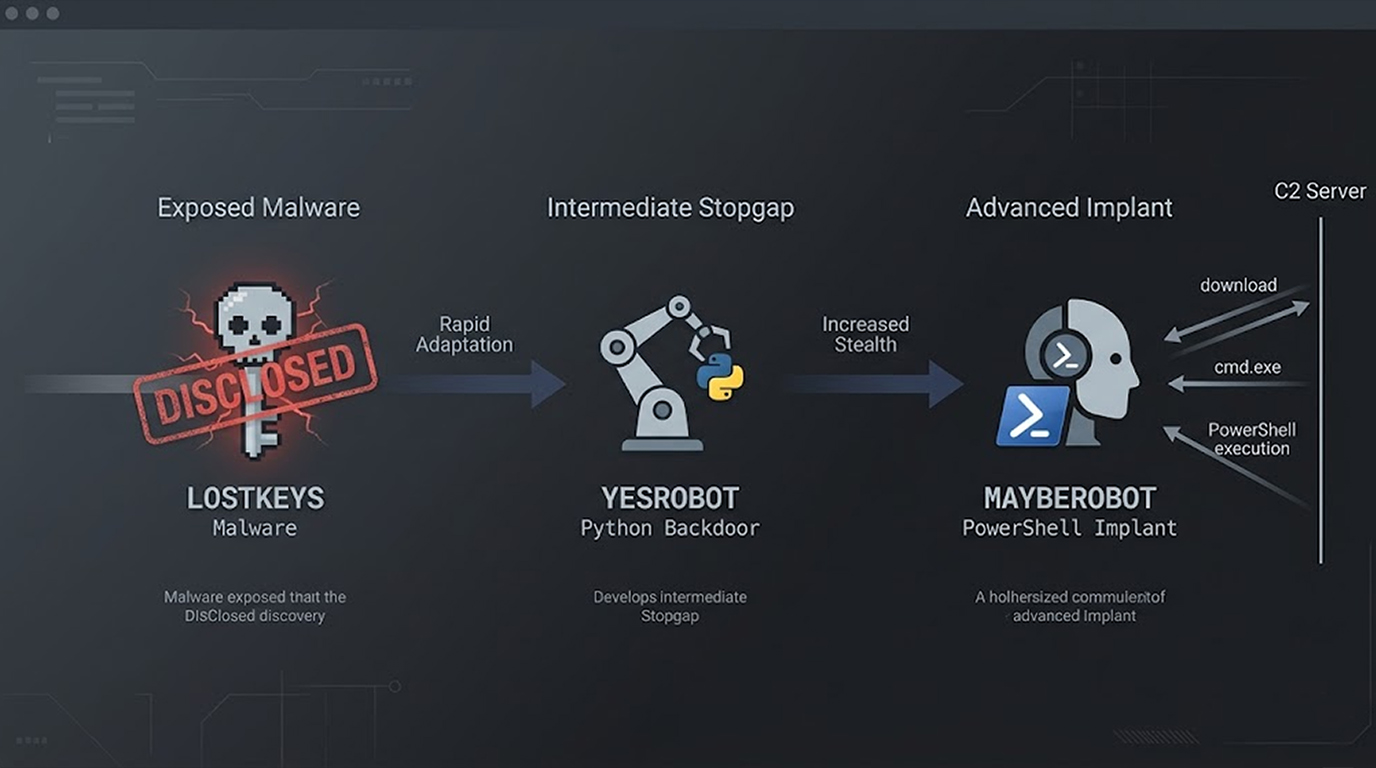
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not t...
Local AI malware represents a major shift in 2026. Instead of sending everything to a remote C2 server, these threats embed small on-device language models...
Sponge-style malware, the quiet, patient threats that slowly soak up credentials, documents, browser data, and session tokens is already a serious problem...
One of the smartest and most satisfying defensive tricks is turning an attacker’s own reconnaissance against them. Instead of just closing exposed ba...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067