Event ID 4104/4103: Catch Malicious PowerShell Scripts
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
Found 389 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
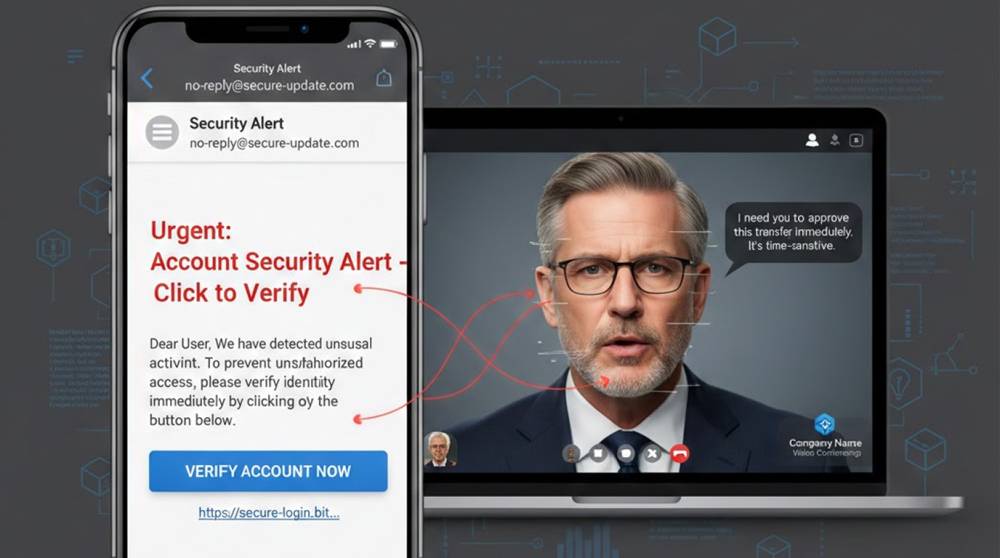
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
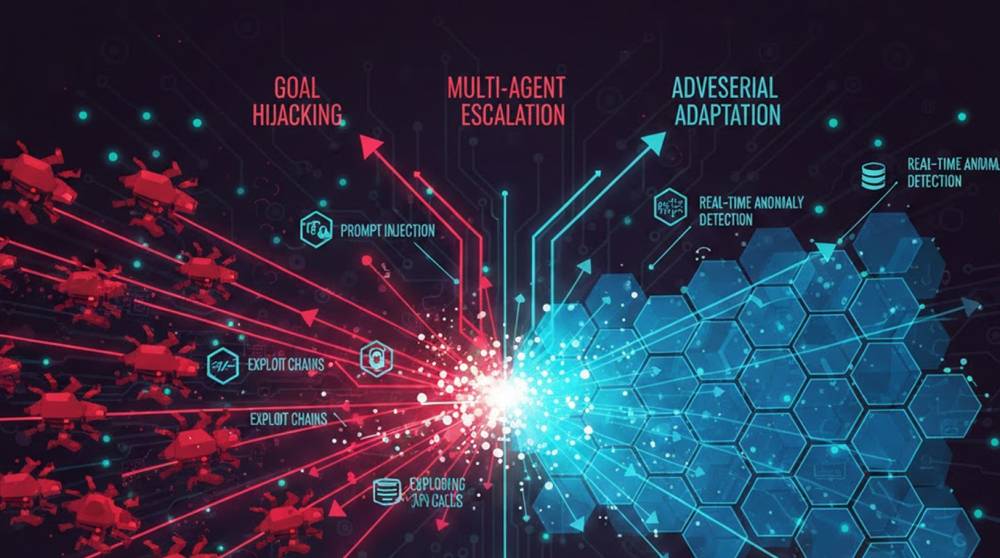
We’ve entered the phase where the most interesting (and dangerous) cyber conflicts are no longer human hacker vs. human defender. They’re incre...
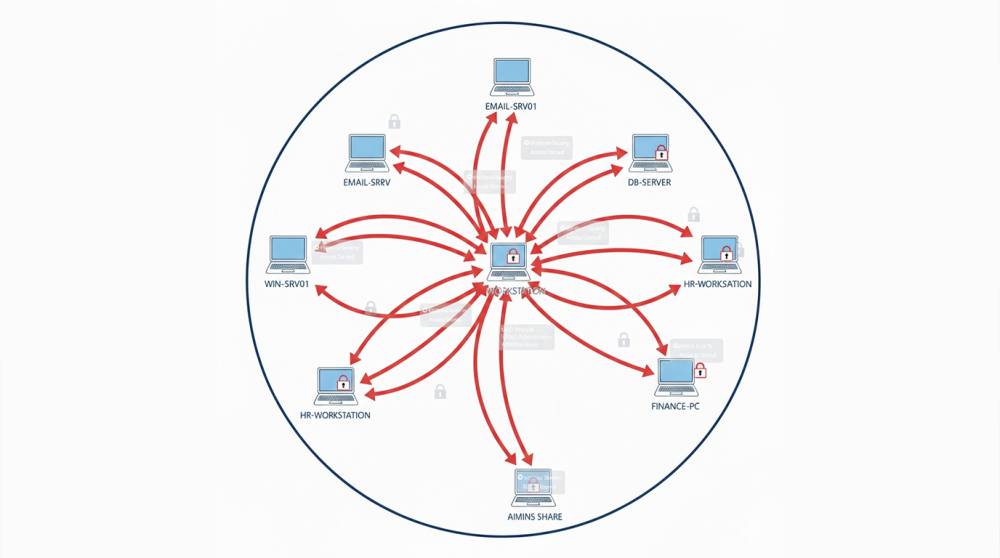
The SMB (Server Message Block) is a popular protocol used by ransomware gangs to move between computers in networked environments like Windows. Port 445 is...
Malware sometimes deliberately triggers a Blue Screen of Death (BSOD) on Windows systems. It’s not a bug , it’s a tactic. The crash either hide...
Malware honeypots are decoy systems set up on purpose to look easy to hack. The idea is simple: make them seem like juicy targets (unpatched servers, open...
When hospitals or medical schools get hit by ransomware or other cyber attacks, it’s not just an IT headache , it becomes a direct threat to patient...
Local privilege escalation vulnerability in the glibc library affects versions 2.35 to 2.38 (build tested: 2.35-0ubuntu3.3) and allows an unprivileged user...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067