Notepad++ Backdoor Supply Chain Attack: Full Breakdown
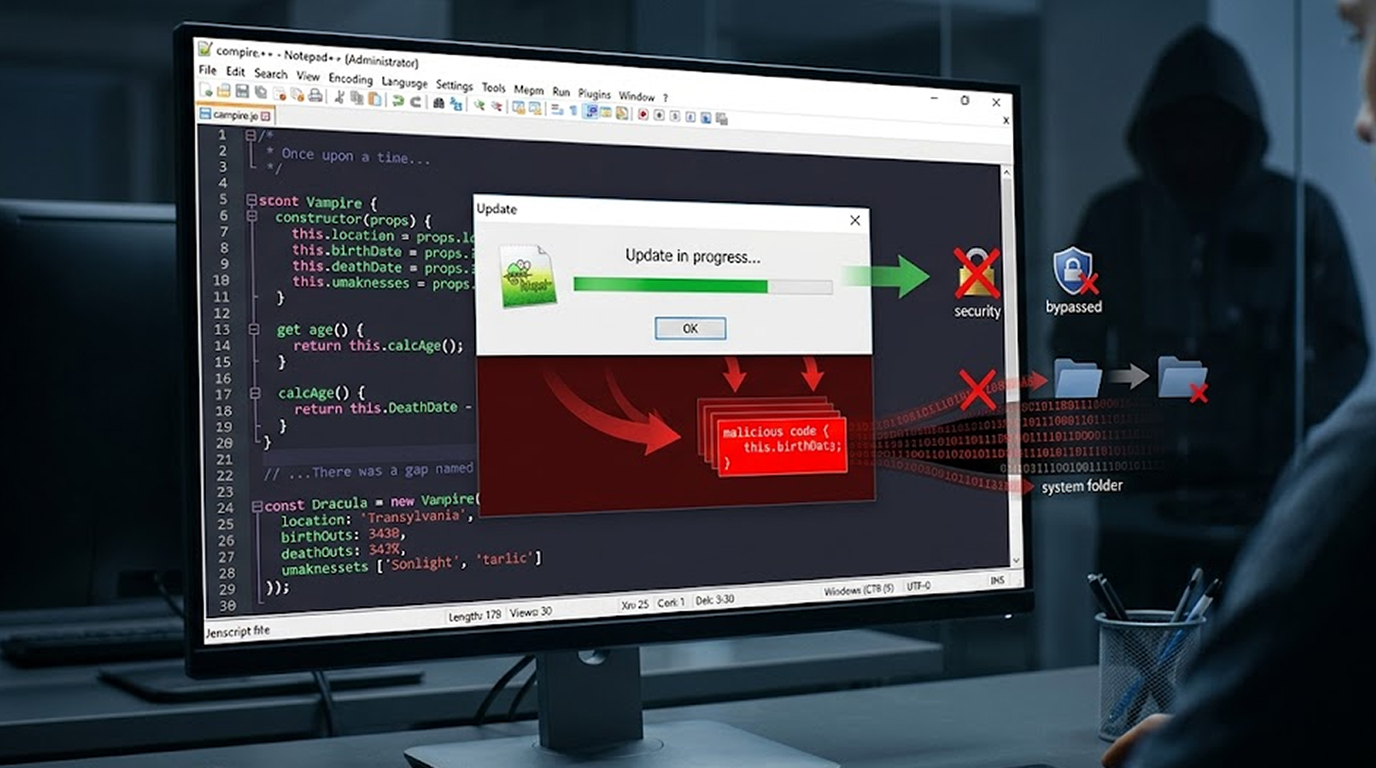
You sit down at your computer. You need to edit a configuration file. You open Notepad++. It has been on your machine for years. Lightweight. Fast. Trustwo...
Found 44 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You sit down at your computer. You need to edit a configuration file. You open Notepad++. It has been on your machine for years. Lightweight. Fast. Trustwo...
PHANTOMPULSE RAT is a newly developed and highly advanced Remote Access Trojan (RAT) that is getting a lot of attention within the cybersecurity community...
According to a joint report by the Google Mandiant and Google Threat Intelligence Group, a suspected China-related threat cluster identified as "UNC6201" h...
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
Modern software applications continue to fuel a significant increase in zero-day vulnerabilities and their associated exploitation. Zero-day vulnerabilitie...
Ivanti disclosed and patched two high-severity (CVSS 9.8) code injection vulnerabilities (CVE-2026-1281 and CVE-2026-1340) affecting Ivanti Endpoint Manage...
You can’t patch what you don’t know exists. Zero-day exploits, unknown vulnerabilities, and novel attack chains are the nightmare scenario for...
A China-nexus advanced persistent threat (APT), tracked as UAT-8837 by Cisco Talos, has been observed targeting critical infrastructure sectors in North Am...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067