Linux Kernel proc readdir Use After Free Leads to Root
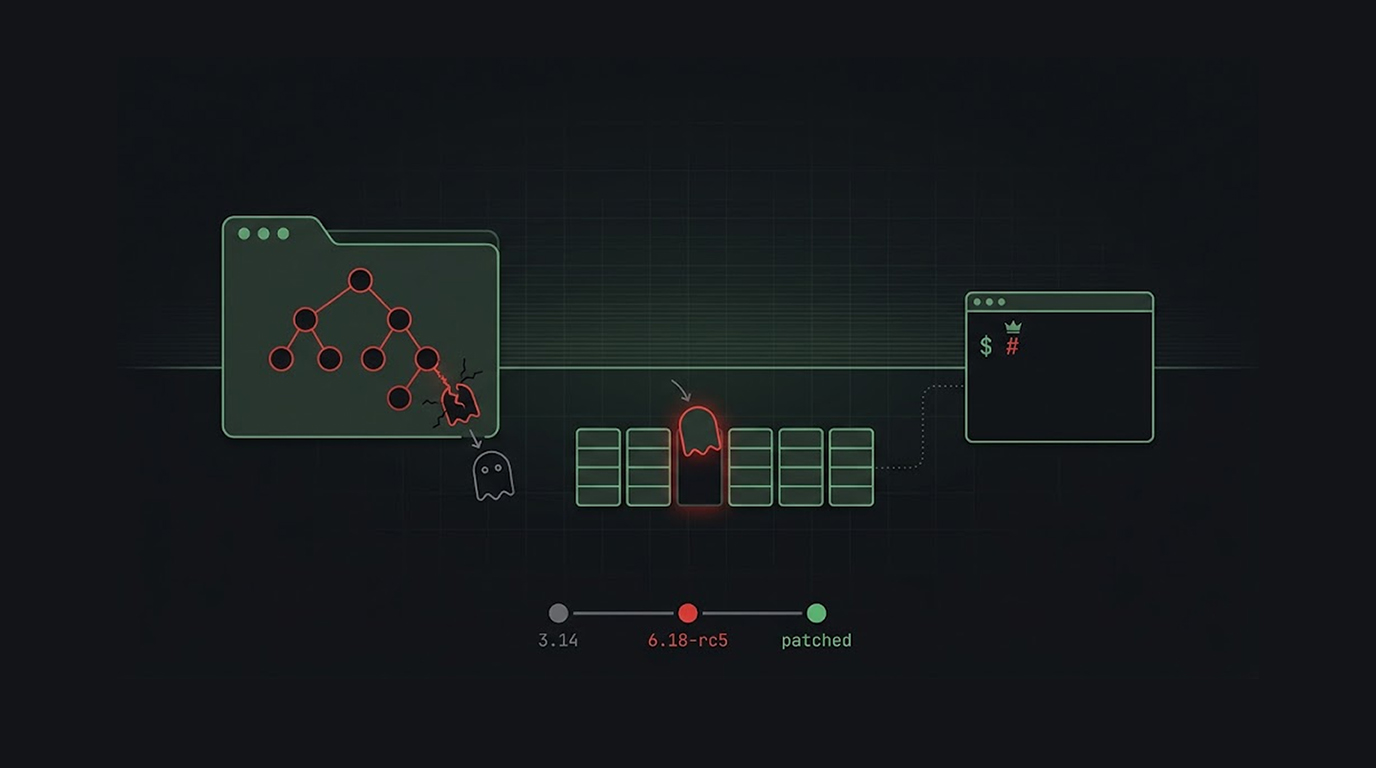
A kernel bug that has lurked in Linux for over a decade can turn any local user into root. The flaw sits in how the proc filesystem handles directory entri...
Found 50 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A kernel bug that has lurked in Linux for over a decade can turn any local user into root. The flaw sits in how the proc filesystem handles directory entri...
Your website is down. Customer data is leaking. Orders have stopped. Google has flagged your site as unsafe. For thousands of small-to-medium businesses an...
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
Malware sometimes deliberately triggers a Blue Screen of Death (BSOD) on Windows systems. It’s not a bug , it’s a tactic. The crash either hide...
Atomic Red Team is an open-source library of small, focused tests mapped to the MITRE ATT&CK framework. These tests simulate real adversary behaviors t...
Piranha CMS version 12.0, which was released approximately halfway through 2025, has a stored cross-site scripting (XSS) vulnerability (CVE-2025-57692). An...
Living off the Land is a modern malware technique that exploits built-in Windows tools, and legitimate programs, as opposed to leaving behind nefarious fil...
A multi-layer phishing operation that targets users in Russia across multiple stages using schemes isn't an uncommon tactic in this arena of internet-based...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067