Email Spoofing Techniques That Bypass SPF, DKIM & DMARC
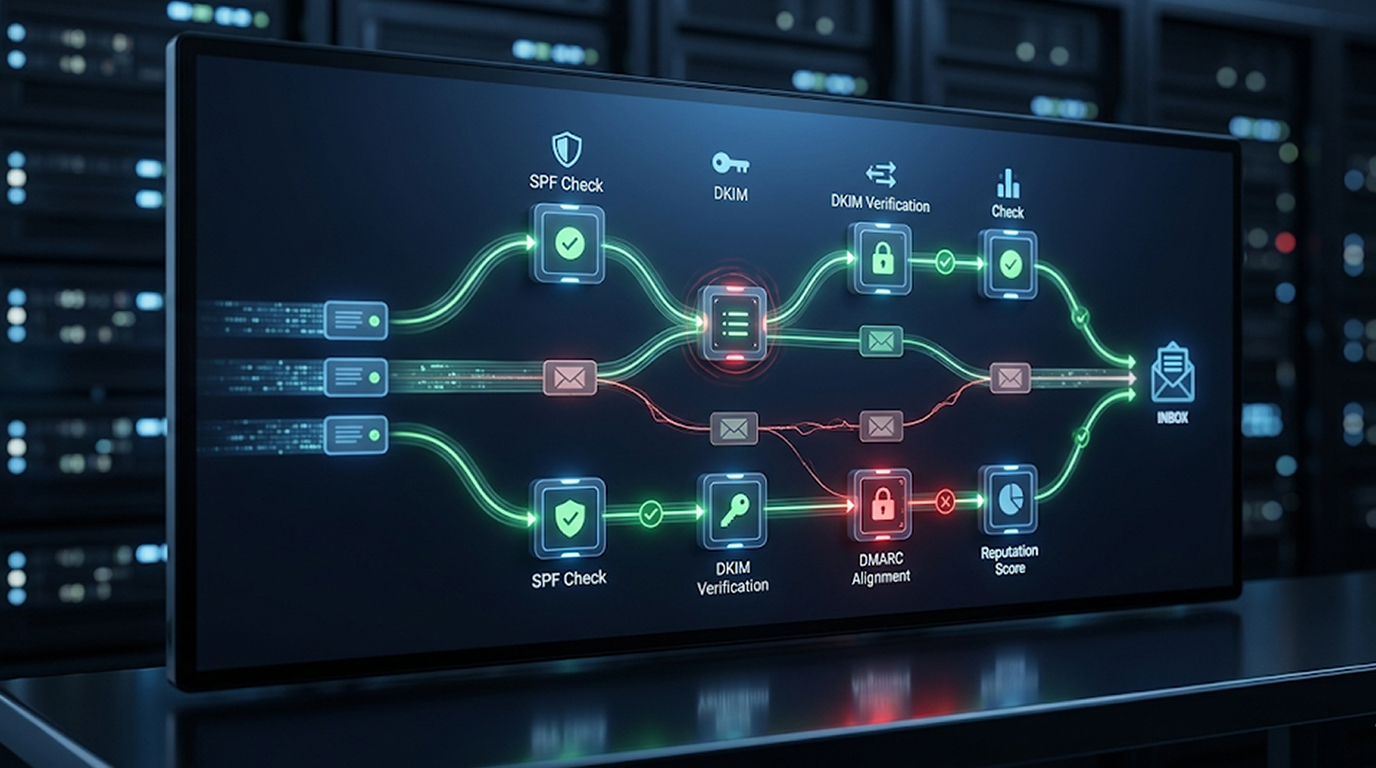
While there has been a significant improvement in the use of SPF, DKIM, and DMARC, sophisticated methods for email spoofing are still able to succeed in 20...
Found 26 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
While there has been a significant improvement in the use of SPF, DKIM, and DMARC, sophisticated methods for email spoofing are still able to succeed in 20...
Every year fraud can lead to losses from Business Email Compromise, bogus invoices, diversion of settlements, Smishing, and internal theft of tens of thous...
CEO-targeted scams, or Business Email Compromise (BEC) or CEO Fraud as they are more commonly referred to, are one of the top financial cyber threats of 20...
Google Postmaster Tools is a free dashboard provided by Google that lets email senders (companies, marketers, newsletter creators, anyone sending bulk mail...
Email headers are the behind the scenes information that are associated with every email. Think of them as "envelopes" and "stamps" on physical letters. Em...
Red team exercises simulate real-world attackers to find weaknesses before malicious actors do. When the tools are used correctly, they don’t just sh...
A blacklisted domain doesn't just fail quietly; its real-life effects include: 1. Emails being sent directly to the spam folder 2. Visitors seein...
Most ransomware attacks do not begin with malware.They begin with trust being misused.Attackers succeed because:1. They use tools already present in enviro...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067