Email Spoofing Techniques That Bypass SPF, DKIM & DMARC
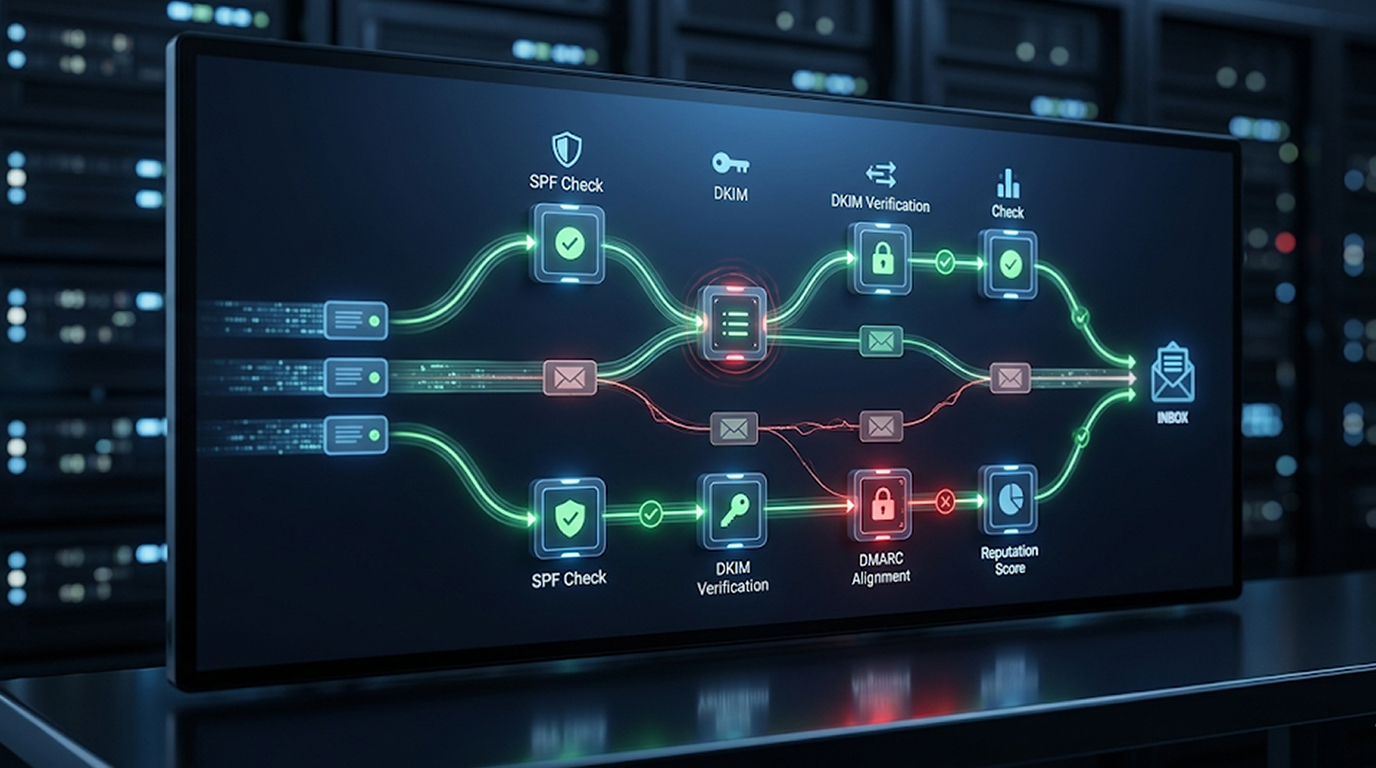
While there has been a significant improvement in the use of SPF, DKIM, and DMARC, sophisticated methods for email spoofing are still able to succeed in 20...
Found 272 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
While there has been a significant improvement in the use of SPF, DKIM, and DMARC, sophisticated methods for email spoofing are still able to succeed in 20...
Whether you are scrolling, playing games, or checking email, it will happen to you: a loud siren goes off and you get a very scary red banner saying, &ldqu...
Persistence is an essential phase of any kind of red team operation or malware. The payloads will need to survive reboot and user logoffs and other routine...
A lot of people think that their phones' cameras only turn on when they use the camera app. However, malicious apps can activate either the front or back c...
In 2026, malware developers are becoming interested in Zig due to its use as a modern day replacement for C as a systems programming language. Whereas legi...
Undocumented (or “hidden”) API endpoints often called shadow APIs represent one of the biggest risks in modern web applications. These endpoint...
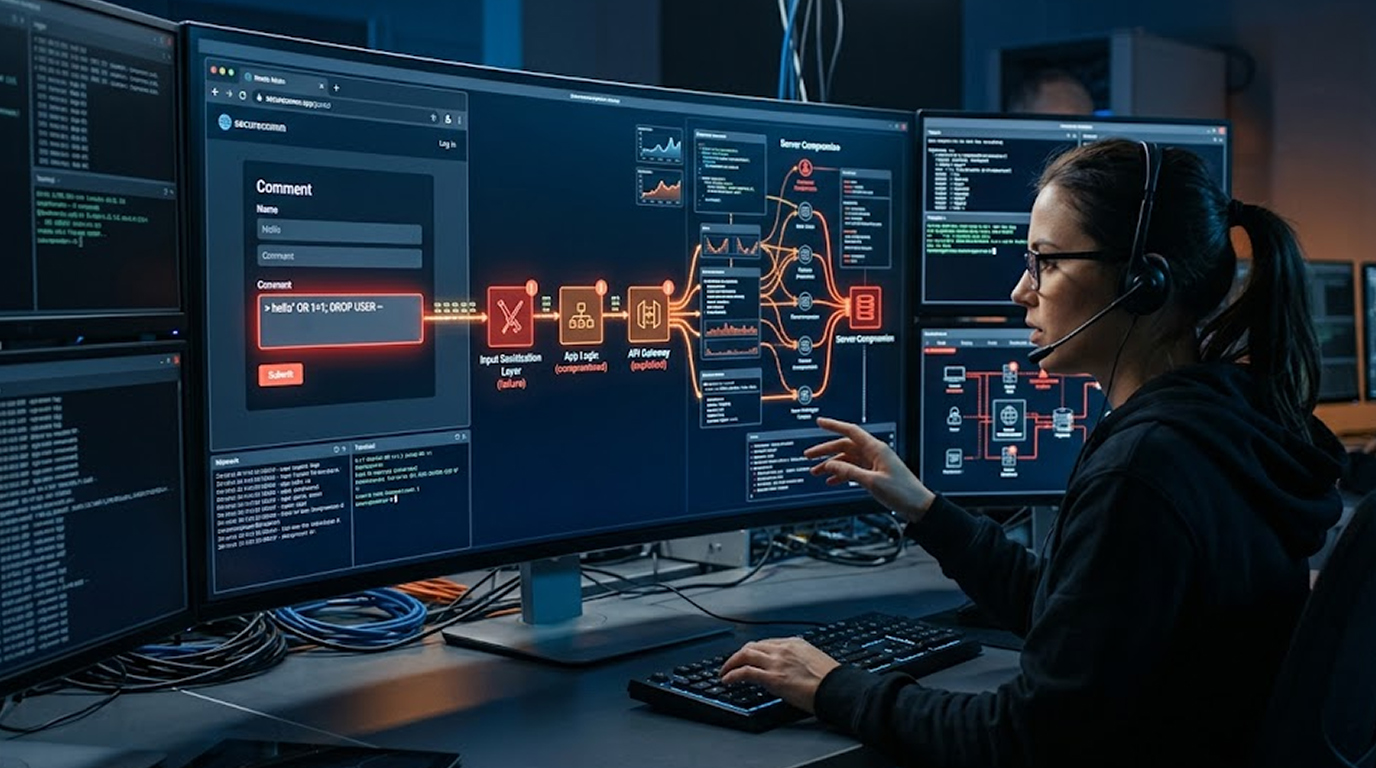
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
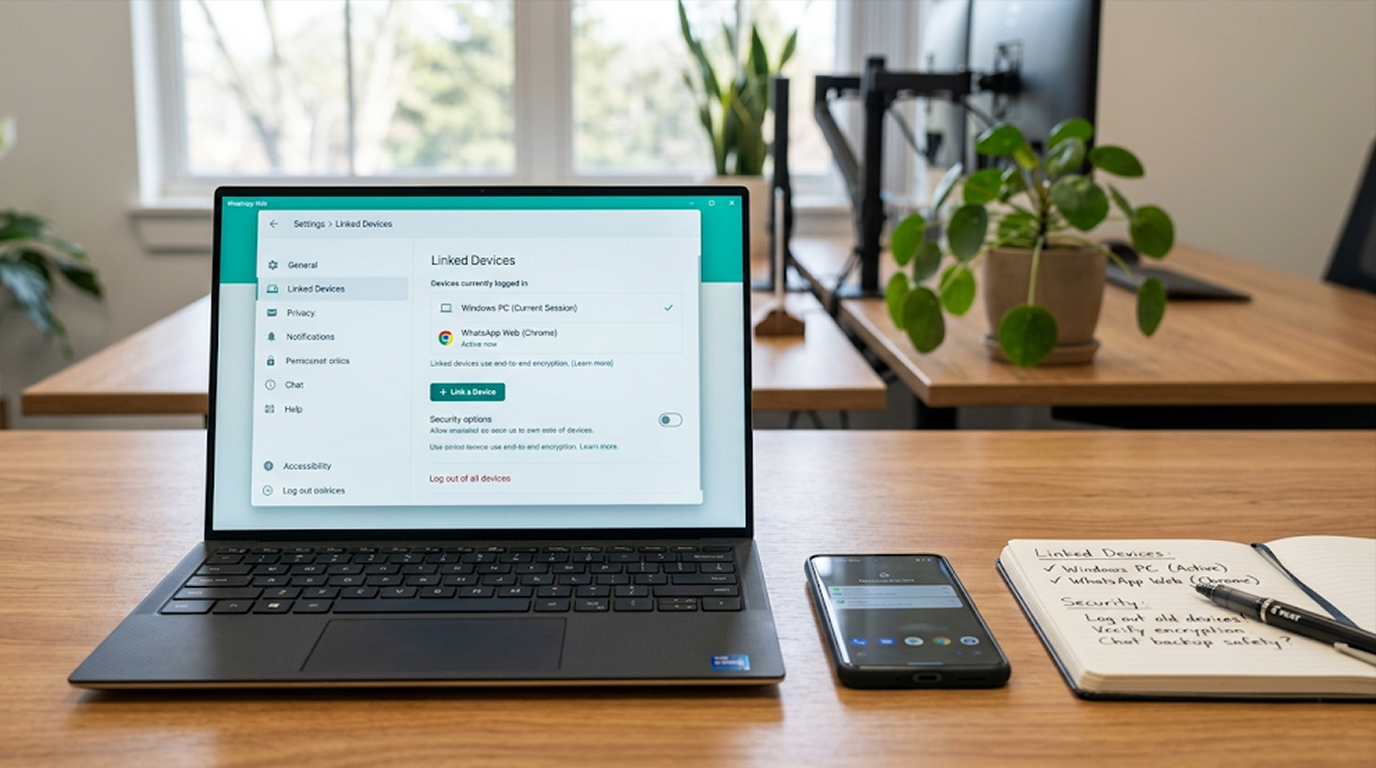
Many people assume their private chats on messaging apps like WhatsApp, Signal, or Telegram stay visible only on their own devices. However, a common and e...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067