Where to Practice SQLmap: 7 Legal Targets for Ethical Hacking
You've now heard of SQLmap, and now you want to try it out for yourself. This tool is definitely powerful, and you would like to see how it works. However,...
Found 386 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You've now heard of SQLmap, and now you want to try it out for yourself. This tool is definitely powerful, and you would like to see how it works. However,...
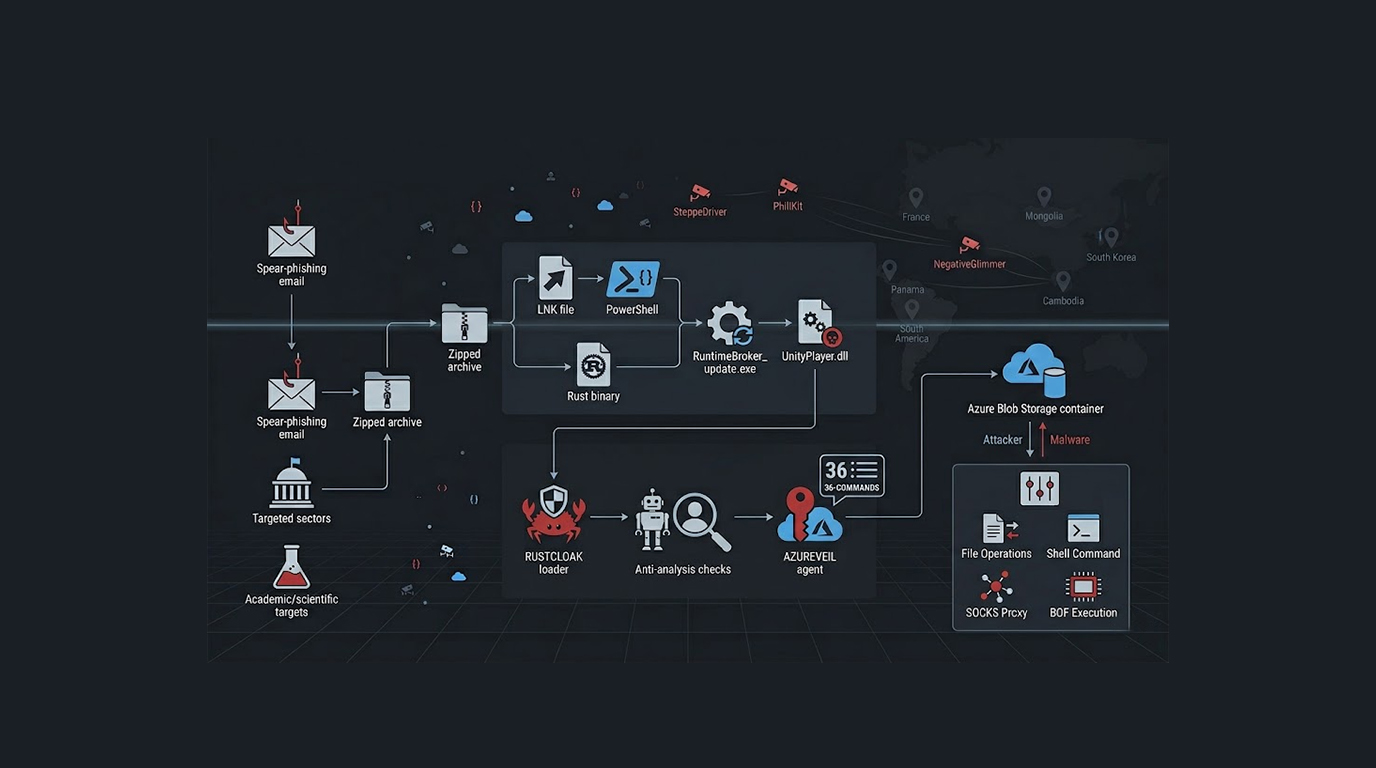
Officials and citizens in the Czech Republic and Taiwan have become victims of a new cyber espionage operation called Operation Dragon Weave. Attackers are...
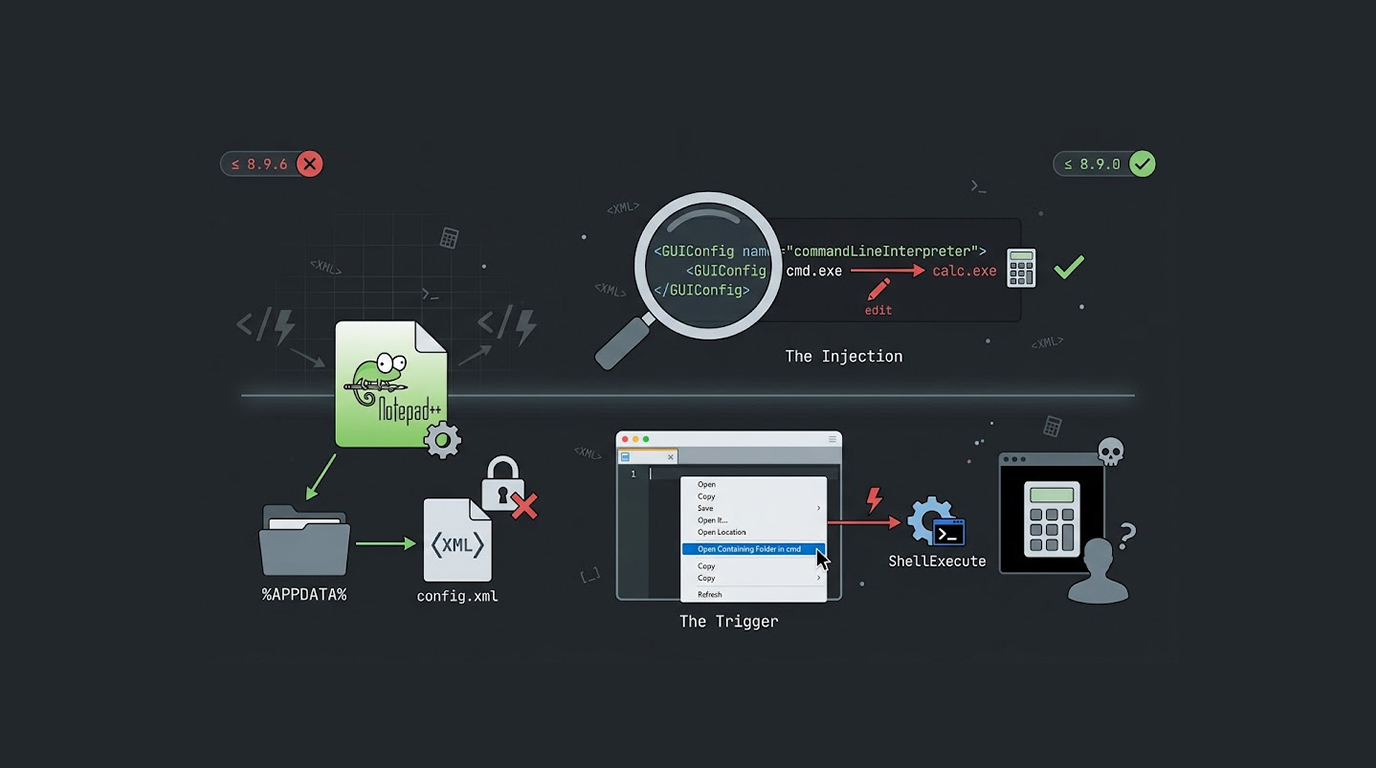
A vulnerability was found in Notepad++ that permits attackers to execute any arbitrary code by modifying a configuration file. The vulnerability affects al...
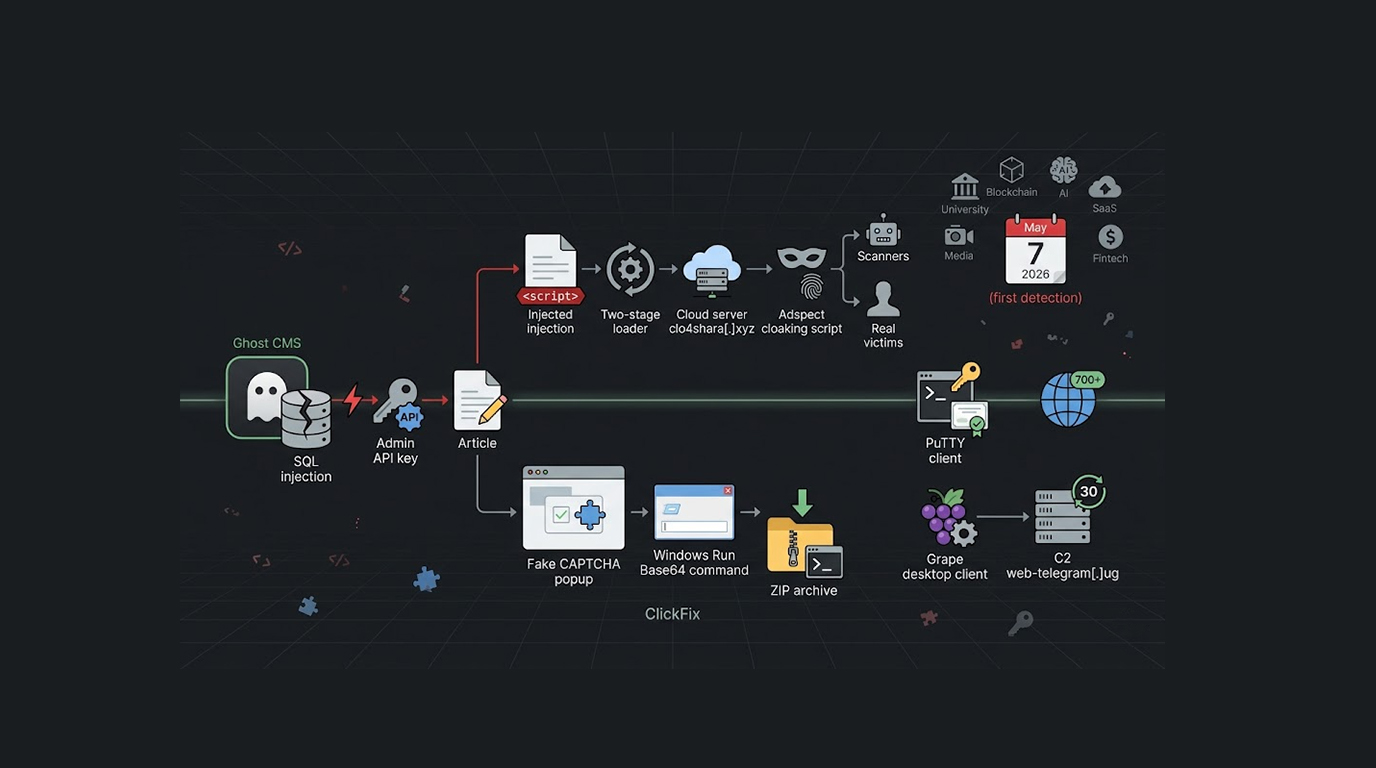
Threat actors took advantage of a critical SQL injection vulnerability present in Ghost CMS to insert malicious Javascript code into ClickFix campaigns lau...
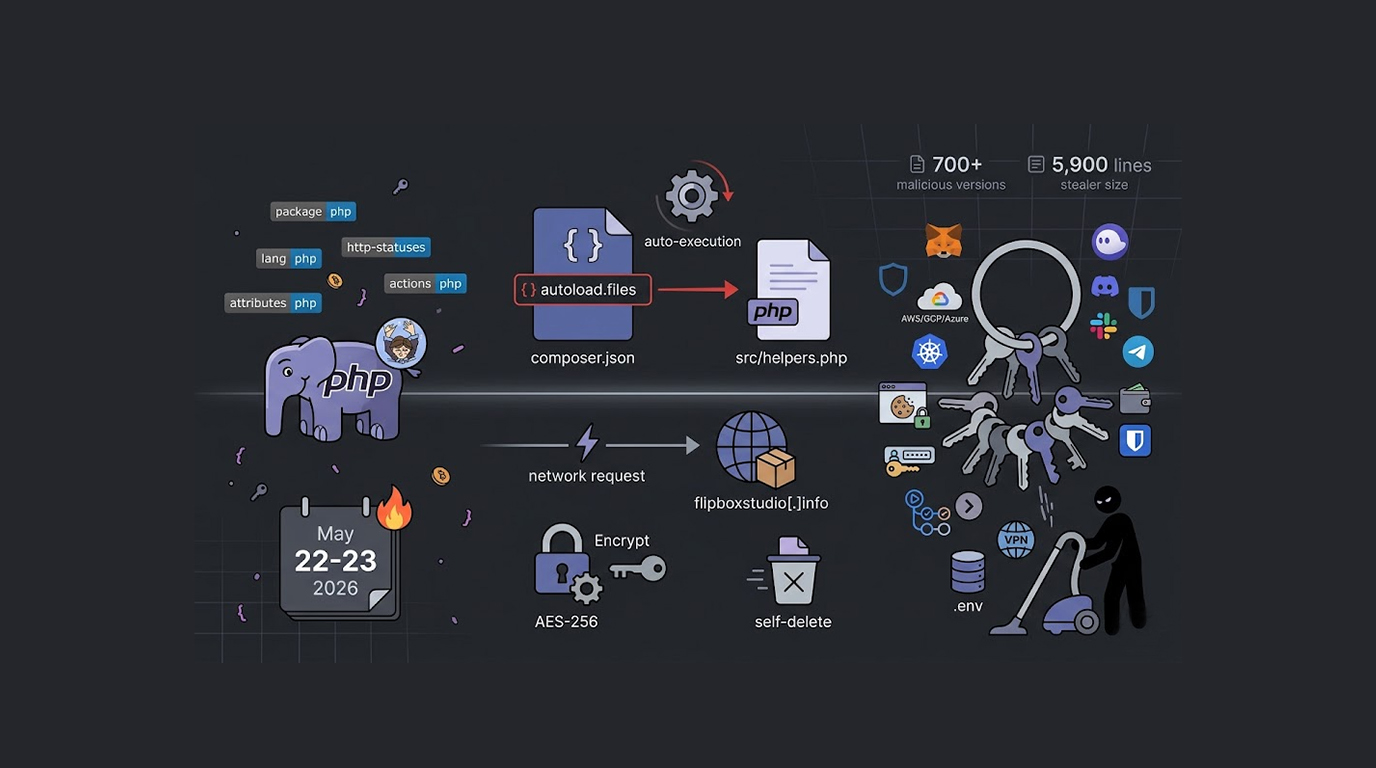
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
An issue with Remote Sunrise Helper, made by RS Ltd for Windows, allows unauthorized users access to view all files and folders on the device and has since...
A single click on a malicious link, a quick approval of the "Open Snipping Tool" prompt, and your Windows password hash is on its way to an attacker. The...
Showboat malware targets MT companies in the Middle East. It looks like was created by someone linked to Chinese-sponsored organizations and has been utili...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067