Monitoring Gap: Why Runtime Detection Misses Attacks
Your dashboards are green, your EDR is running, your SIEM is ingesting logs, and your SOC is staffed, everything looks healthy, and yet attackers are insid...
Found 34 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your dashboards are green, your EDR is running, your SIEM is ingesting logs, and your SOC is staffed, everything looks healthy, and yet attackers are insid...
You are browsing the web. Everything looks normal. You log into your bank, check your email, pay a few bills. Nothing seems out of the ordinary. But somet...
You need to monitor your network traffic. You have heard of Suricata, Snort, and Zeek. But which one should you use? And can you run more than one at the s...
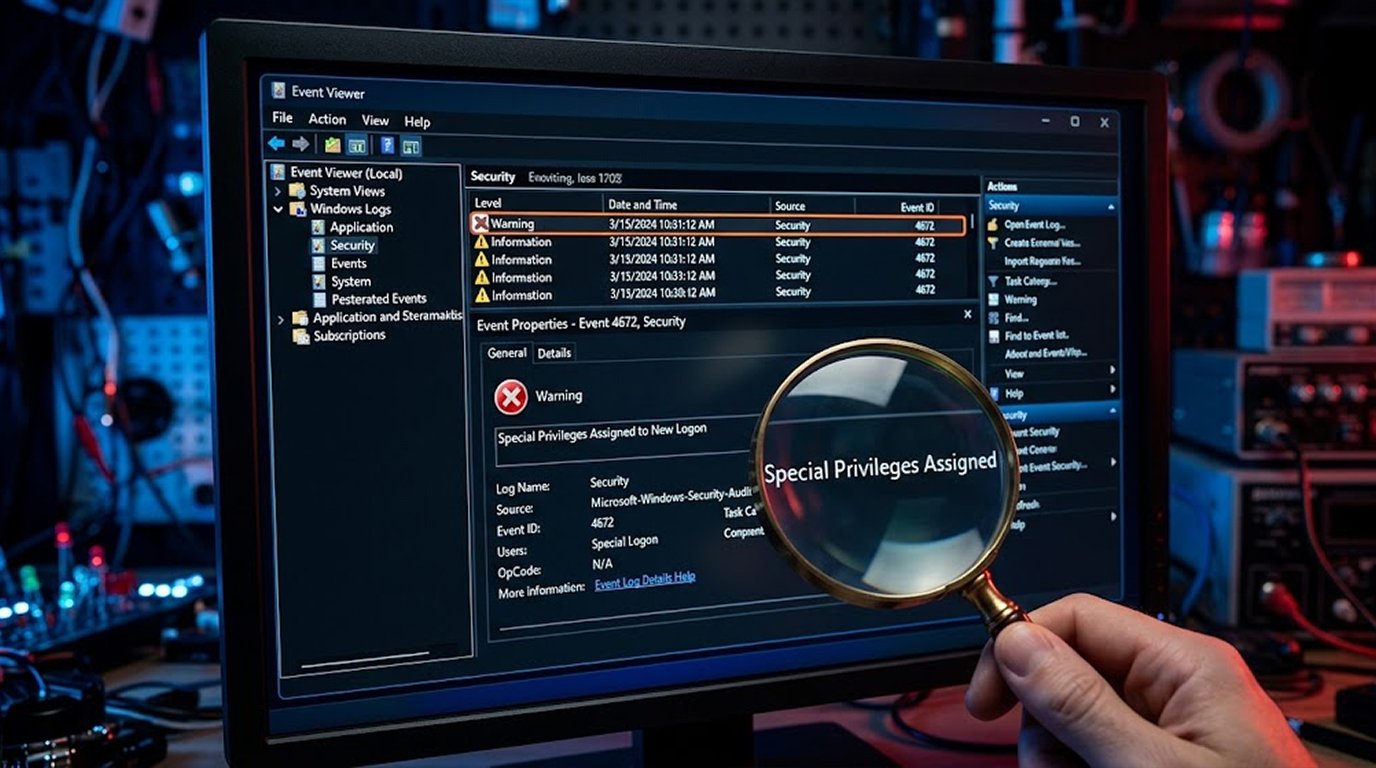
You are sitting there going through your Windows event logs. Everything looks fine. Then you spot it. Event ID 4672. Special privileges assigned to a new l...
A critical severity vulnerability in the Progress Kemp LoadMaster load balancer has been added to CISA’s Known Exploited Vulnerabilities list. The ad...
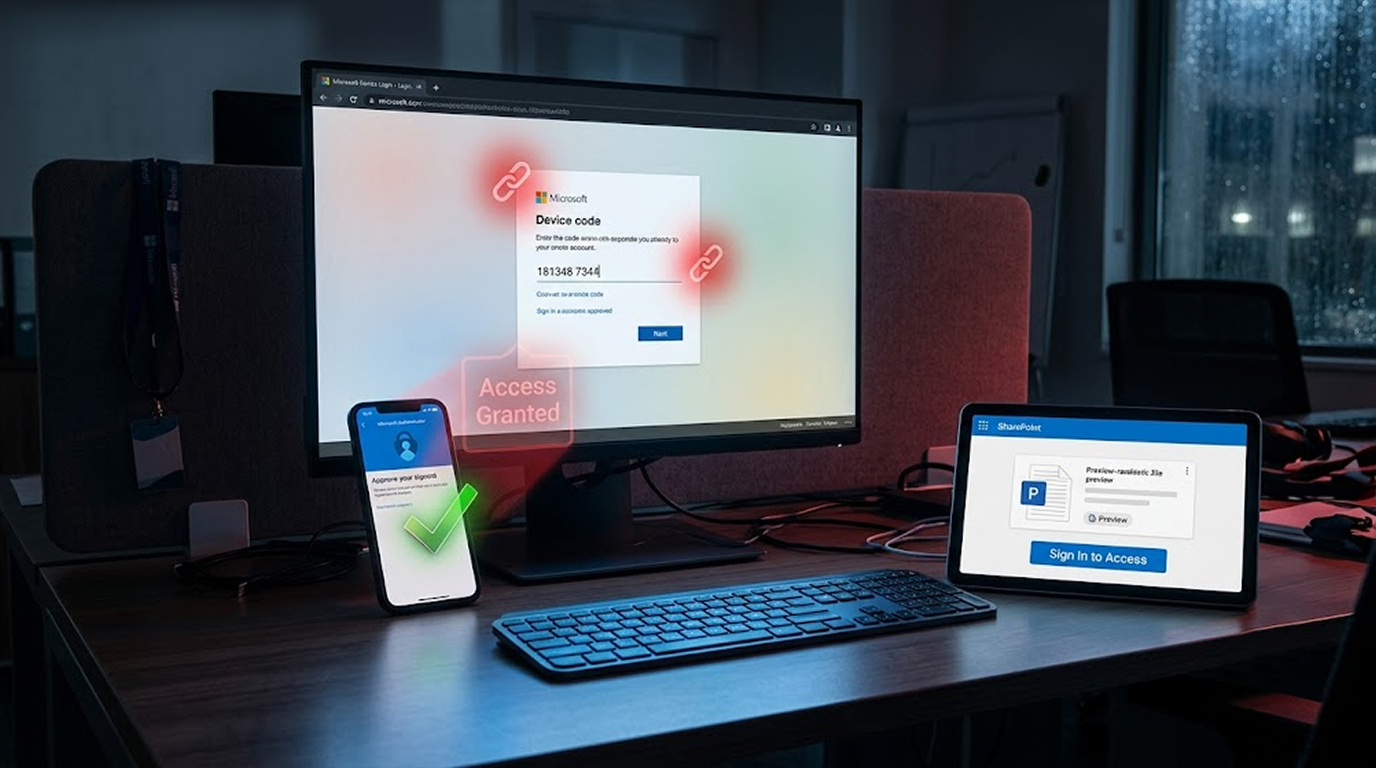
A phishing kit called Kali365 is turning a legitimate Microsoft login into a gateway to corporate data. The kit targets US organizations with attacker-cont...
Traditional antivirus looks for known signatures. It has a list of bad files and checks every file against that list. If the malware is new, the antivirus...
Bot problem? The malicious bots are scraping your site, stealing your content, and overwhelming your servers. You have tried blocking IP addresses, but the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067