Generative AI for Event ID 4625 Simulation: Training ML Models
You are building a machine learning model to detect failed logon attempts. You need thousands of Event ID 4625 samples. But you only have a few hundred in...
Found 12 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You are building a machine learning model to detect failed logon attempts. You need thousands of Event ID 4625 samples. But you only have a few hundred in...
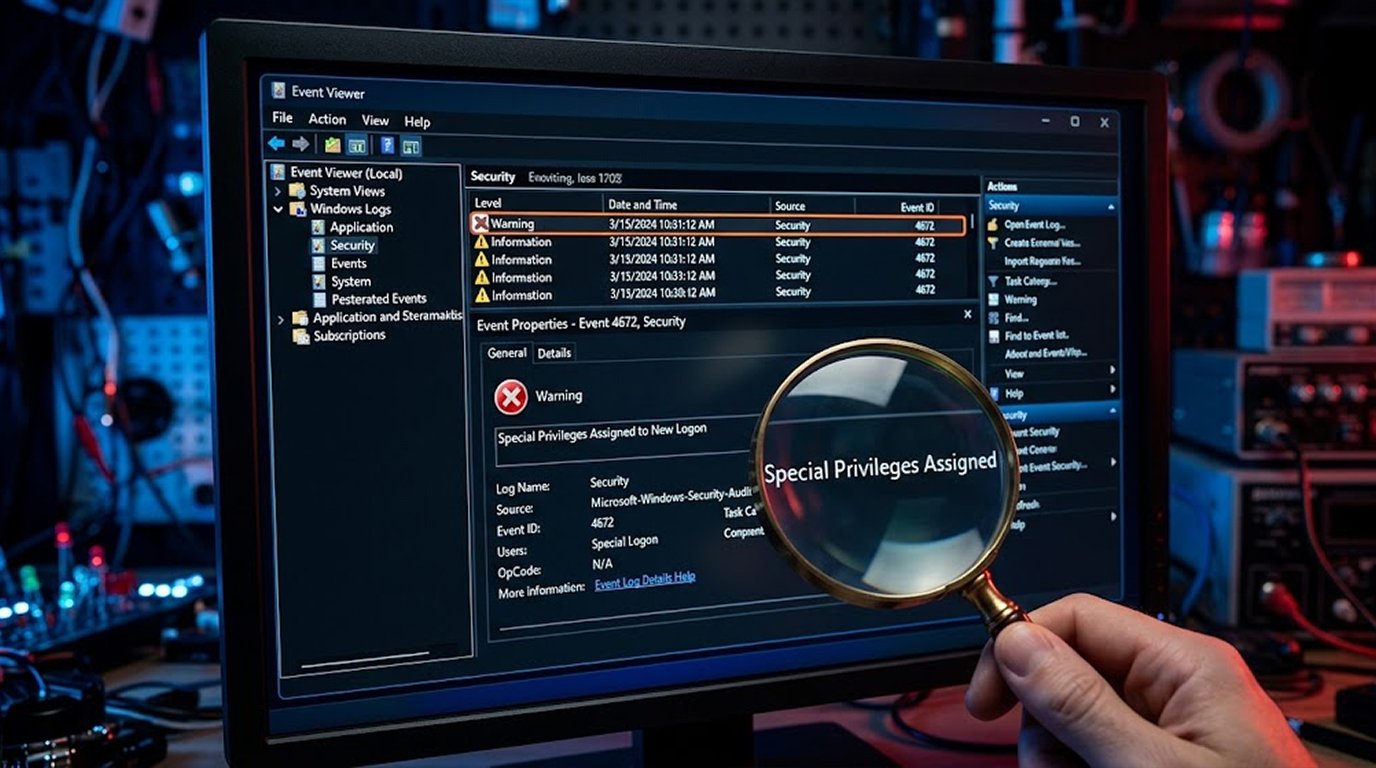
You are sitting there going through your Windows event logs. Everything looks fine. Then you spot it. Event ID 4672. Special privileges assigned to a new l...
Your network is set up like this, employees plug into the switch, servers plug into the same switch, everything can talk to everything, it is simple, it is...
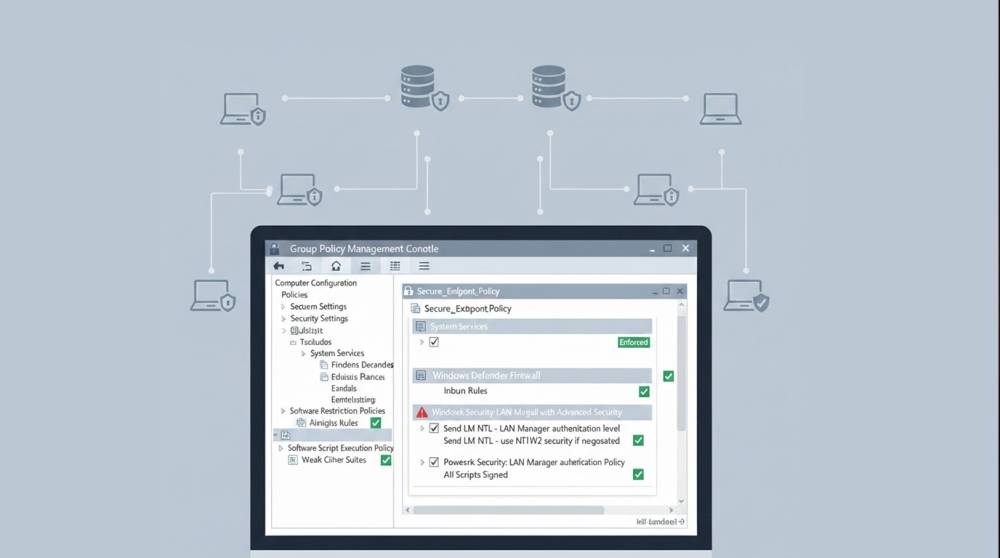
GPO (Group Policy Object) is one of the most effective, but also underused, tools for providing security to Windows networks as well as providing centraliz...
You can’t patch what you don’t know exists. Zero-day exploits, unknown vulnerabilities, and novel attack chains are the nightmare scenario for...
The security models of the past are based on the assumption that once someone has gained access to the internal network, that person can be trusted and all...
Not every attack relies on PowerShell, SMB, or RDP.There’s a long tail of tools that look harmless, or “IT-related” in logs.That’s...
Most breaches don’t begin with malware detonating everywhere.They begin quietly.Someone logs in.They look around.They test limits.If you replay the l...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067