Event ID 4672: How to Detect Admin Access and Privilege Escalation
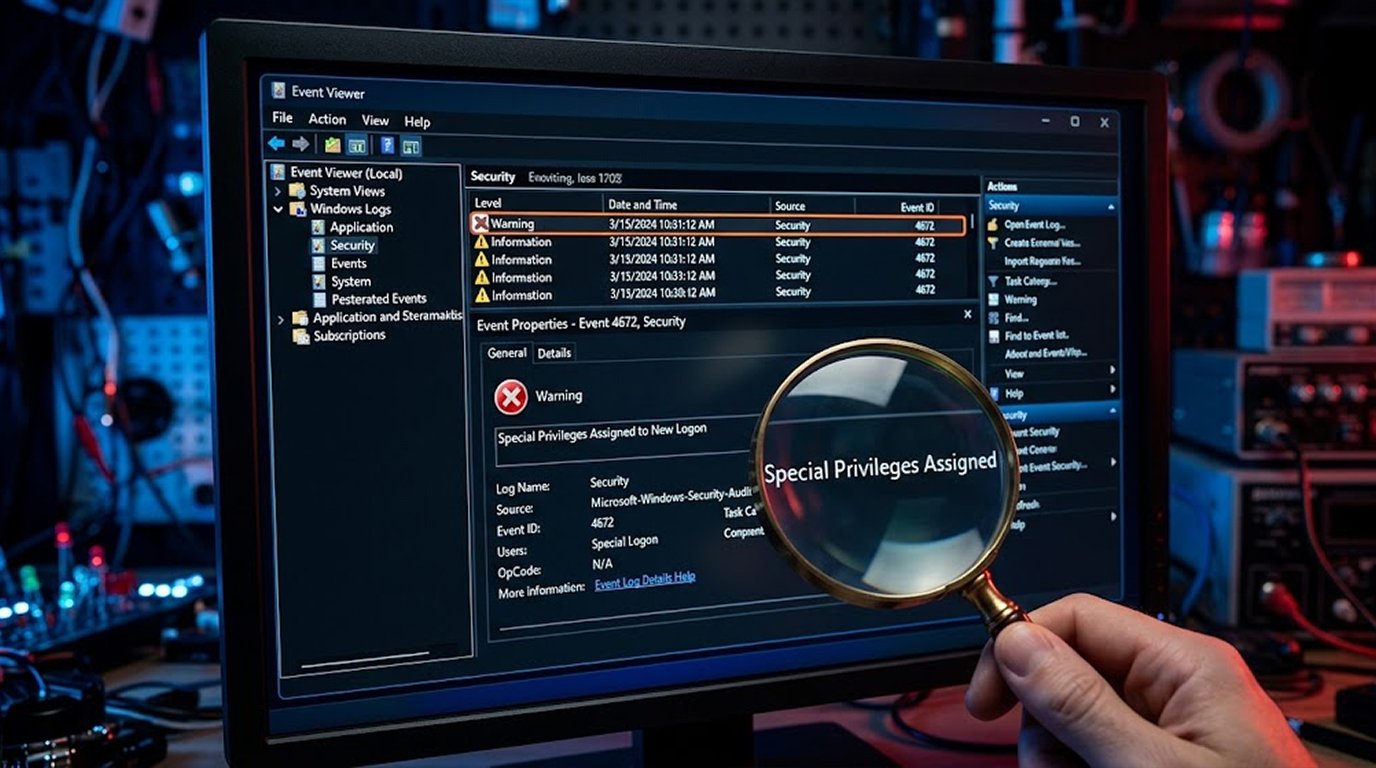
You are sitting there going through your Windows event logs. Everything looks fine. Then you spot it. Event ID 4672. Special privileges assigned to a new l...
Found 15 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You are sitting there going through your Windows event logs. Everything looks fine. Then you spot it. Event ID 4672. Special privileges assigned to a new l...
Remember the script kiddie, that cliché of a teenage hacker sitting in their parents' basement, running pre-written code they barely understood, cli...
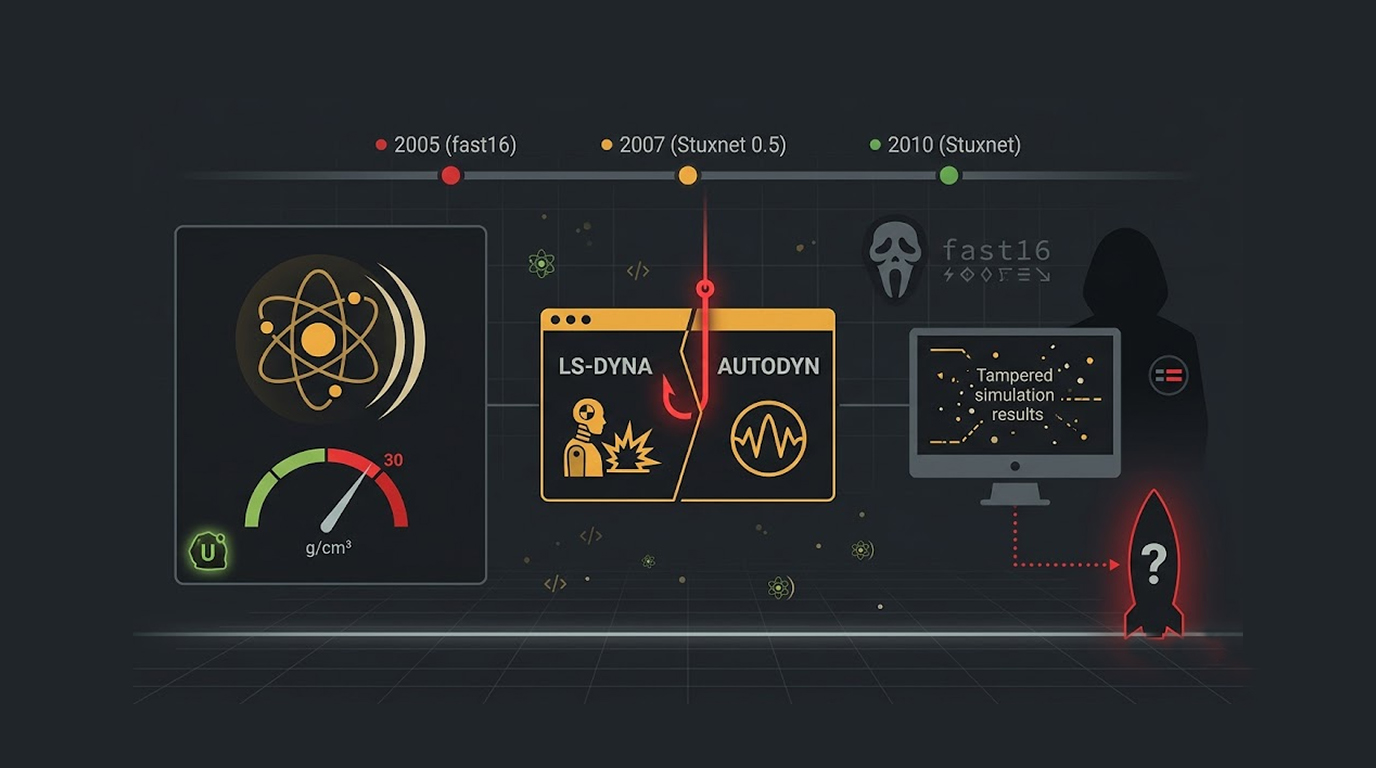
A new analysis of the Lua-based fast16 malware has confirmed that it was a cyber sabotage tool designed to tamper with nuclear weapons testing simulations,...
You do not have time for a 20-page threat intelligence report. You have a board meeting in an hour. Your SOC is flagging anomalies. And there is a new thre...
Red teams simulate real-world attacks ethically (with permission) to identify vulnerabilities before malicious actors do. Exploit tools automate discovery,...
Most people worry about stolen files or hacked accounts.Very few worry about their camera or microphone.That is exactly why these are abused.When a camera...
Breaking web apps usually doesn’t start with zero-days or Hollywood hacking.It starts with someone opening the same tools developers and testers alre...
Most real-world breaches don’t rely on flashy malware.They rely on tools that look familiar, and completely legitimate in logs.If something blends in...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067