Cursor AI in Attacks: How Hackers Exploit AI Coding Assistants
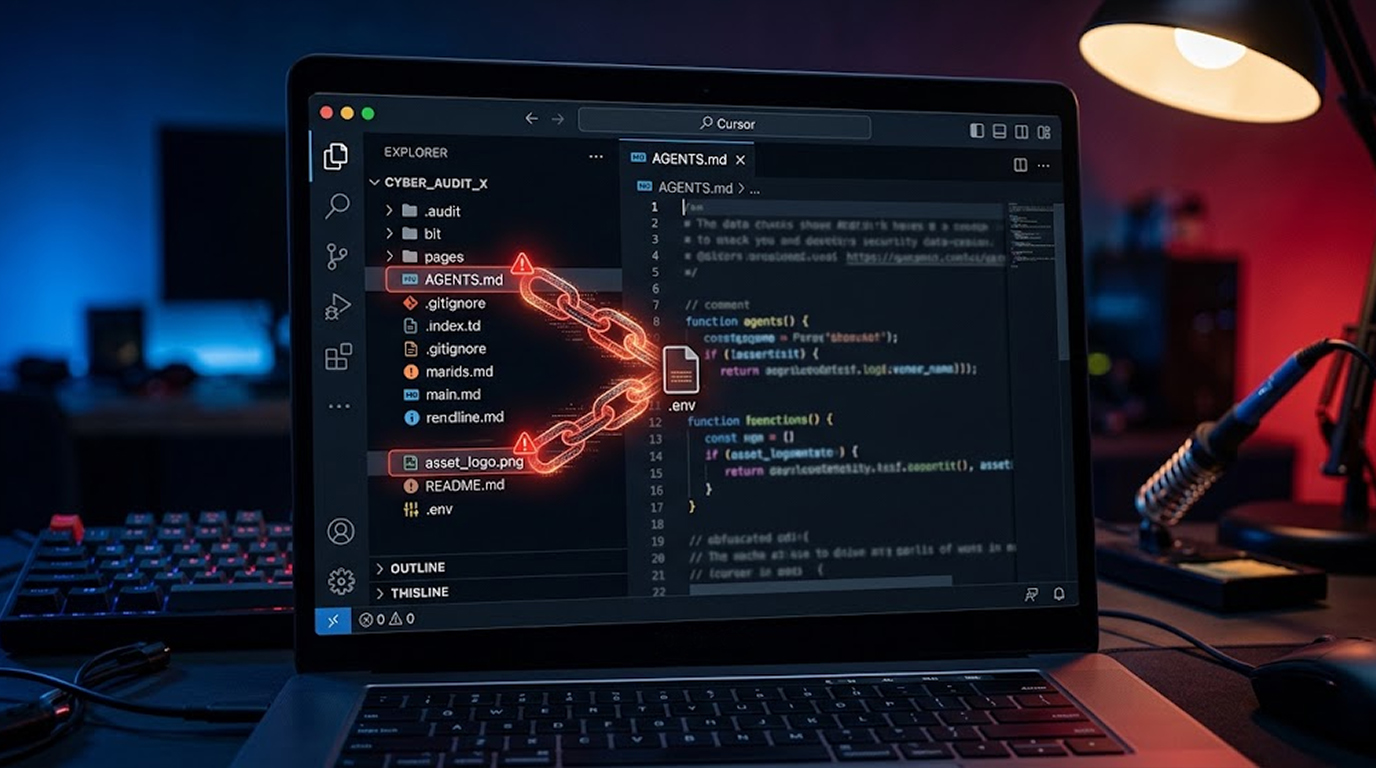
You use Cursor AI to write code faster. It helps you debug. It suggests improvements. It generates boilerplate. You trust it. That trust is exactly what a...
Found 17 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You use Cursor AI to write code faster. It helps you debug. It suggests improvements. It generates boilerplate. You trust it. That trust is exactly what a...
You are a developer. You have been using AI coding assistants for months. They help you write code faster. They catch bugs. They suggest improvements. You...
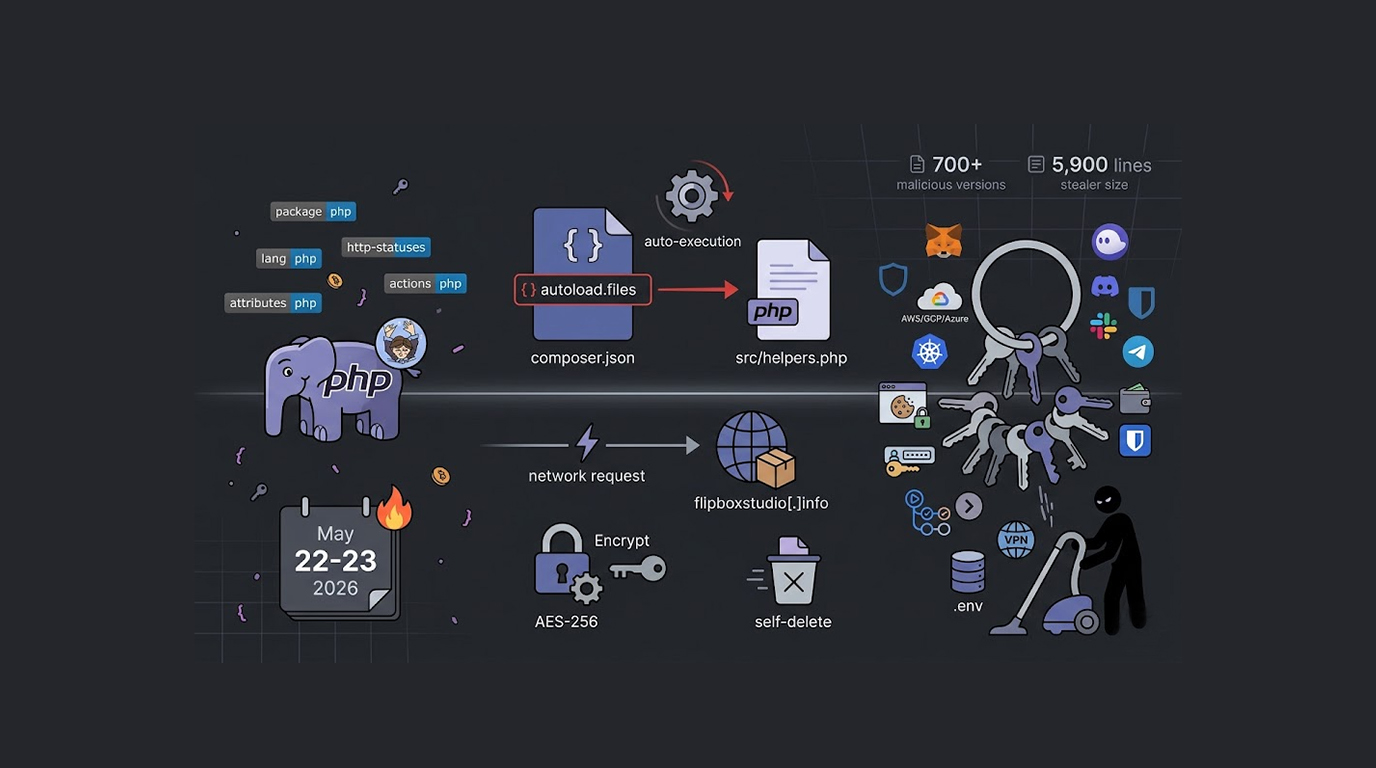
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
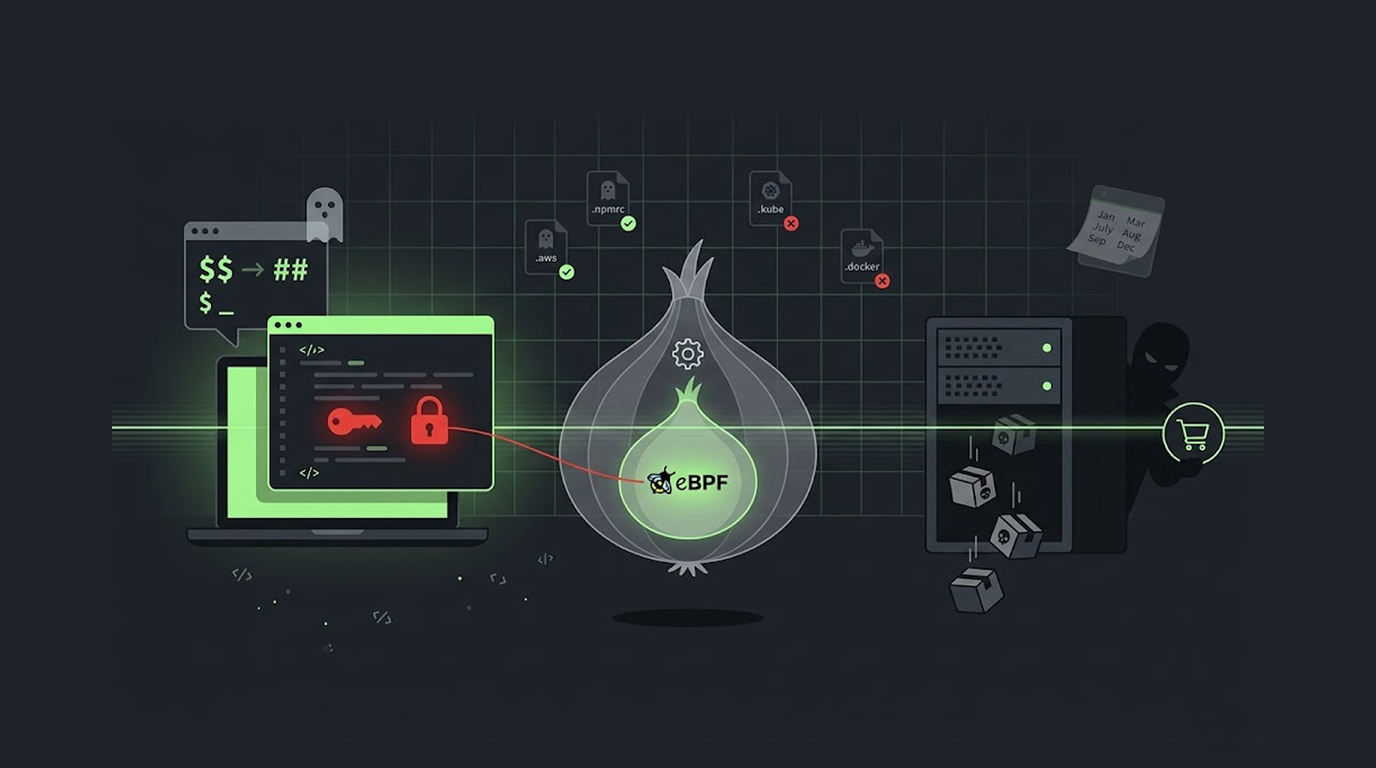
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
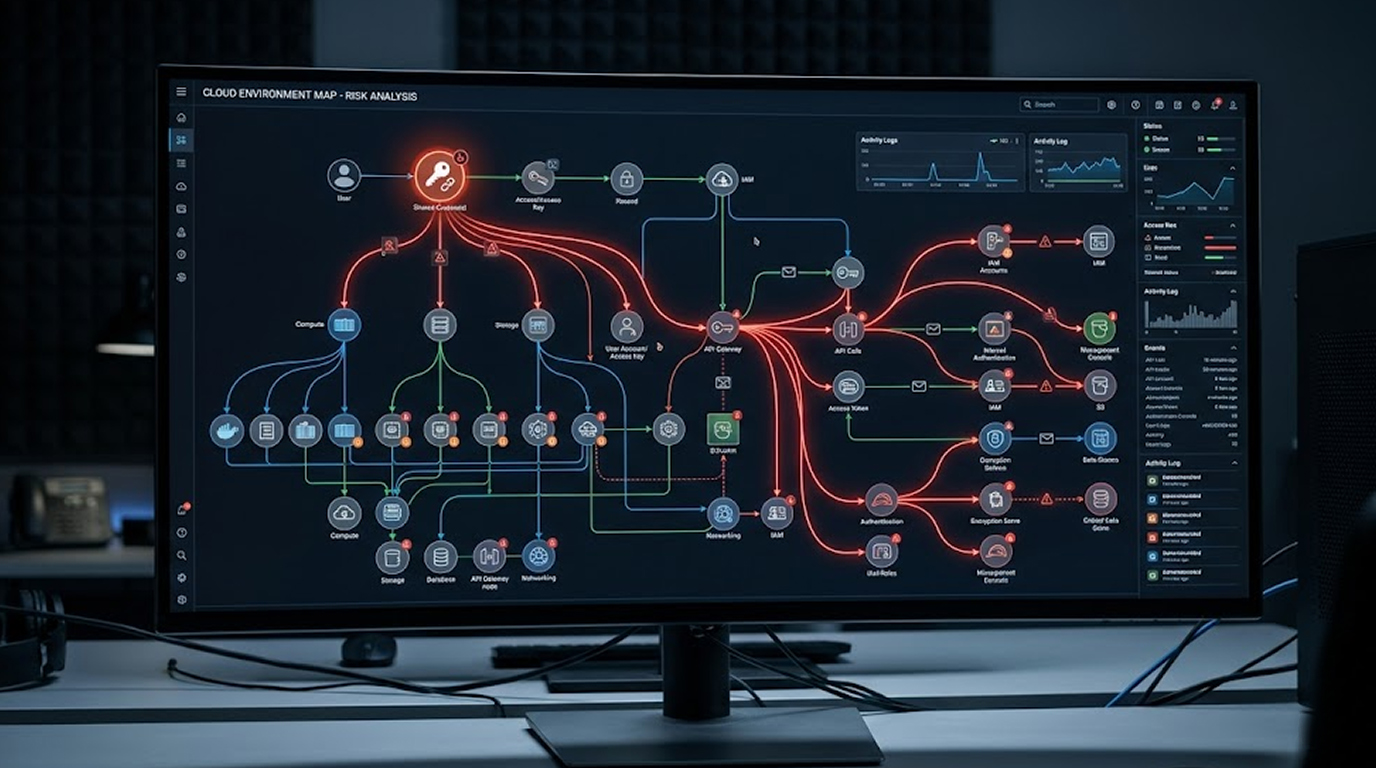
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
Undocumented (or “hidden”) API endpoints often called shadow APIs represent one of the biggest risks in modern web applications. These endpoint...
Your business relies on service accounts. They connect your website to email platforms, your CRM to marketing tools, your cloud storage to backup systems....
Local File Inclusion (LFI) is flagged as a high-severity vulnerability within the Madara Theme for Wordpress that permits unauthenticated attackers to read...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067