GitHub comments abused to push malware via Microsoft repo URLs
A GitHub flaw, or possibly a design decision, is being abused by threat actors to distribute malware using URLs associated with Microsoft repositories, mak...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
A GitHub flaw, or possibly a design decision, is being abused by threat actors to distribute malware using URLs associated with Microsoft repositories, making the files appear trustworthy. While most...
Read Full ArticleA GitHub flaw, or possibly a design decision, is being abused by threat actors to distribute malware using URLs associated with Microsoft repositories, mak...
Key considerations for conducting ethical hacking experiments One of the fundamental considerations for conducting ethical hacking experiments is understa...
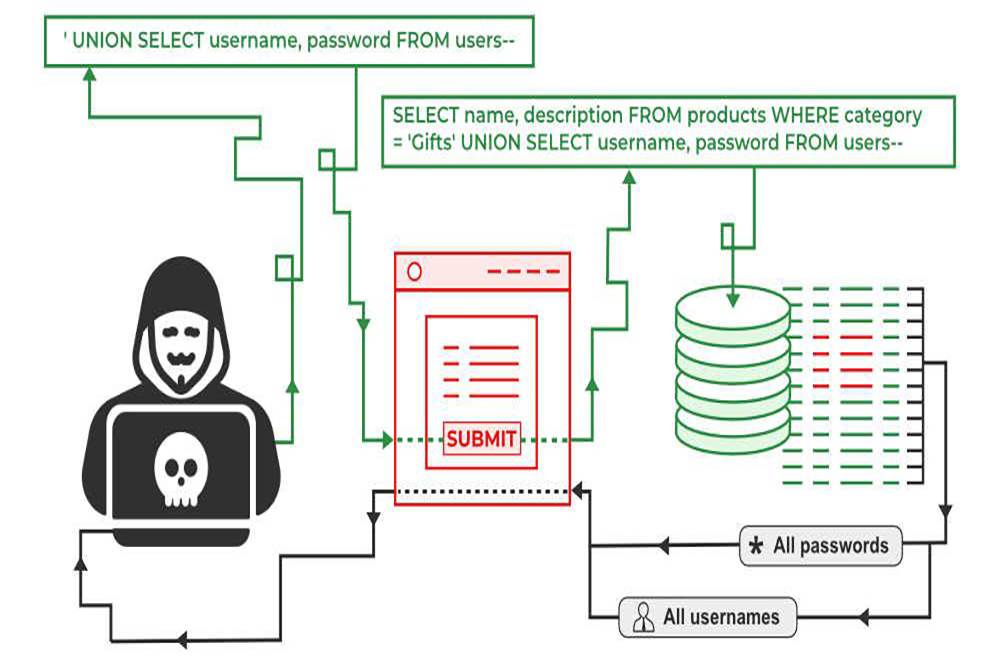
SQL injection (or SQLi) attacks alter SQL queries by injecting malicious code through application vulnerabilities. SQLi attacks that are successful allow a...
Security researchers issued an advisory on six unique XSS vulnerabilities discovered in the Elementor Website Builder and its Pro version that may allow at...
Security researchers have released a proof-of-concept (PoC) exploit for a critical vulnerability in Fortinet's FortiClient Enterprise Management Server (EM...
What if we told you… that the Bad “USB” attack could be performed… without the “USB” element of it, purely...
Solving PwnLab: Init CTF Wellcome to "PwnLab: init", my first Boot2Root virtual machine. Meant to be easy, I hope you enjoy it and maybe learn something....
Using Burpsuite in kali linux - Hack The Box Machine
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067