Keyv npm Worm Spreads Credential-Stealing Malware
An npm worm targeting credentials was released for the first time in keyv@6.0.0 on August 4, 2026. From there, it spread beyond the Keyv and Cacheable name...
Found 9 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An npm worm targeting credentials was released for the first time in keyv@6.0.0 on August 4, 2026. From there, it spread beyond the Keyv and Cacheable name...
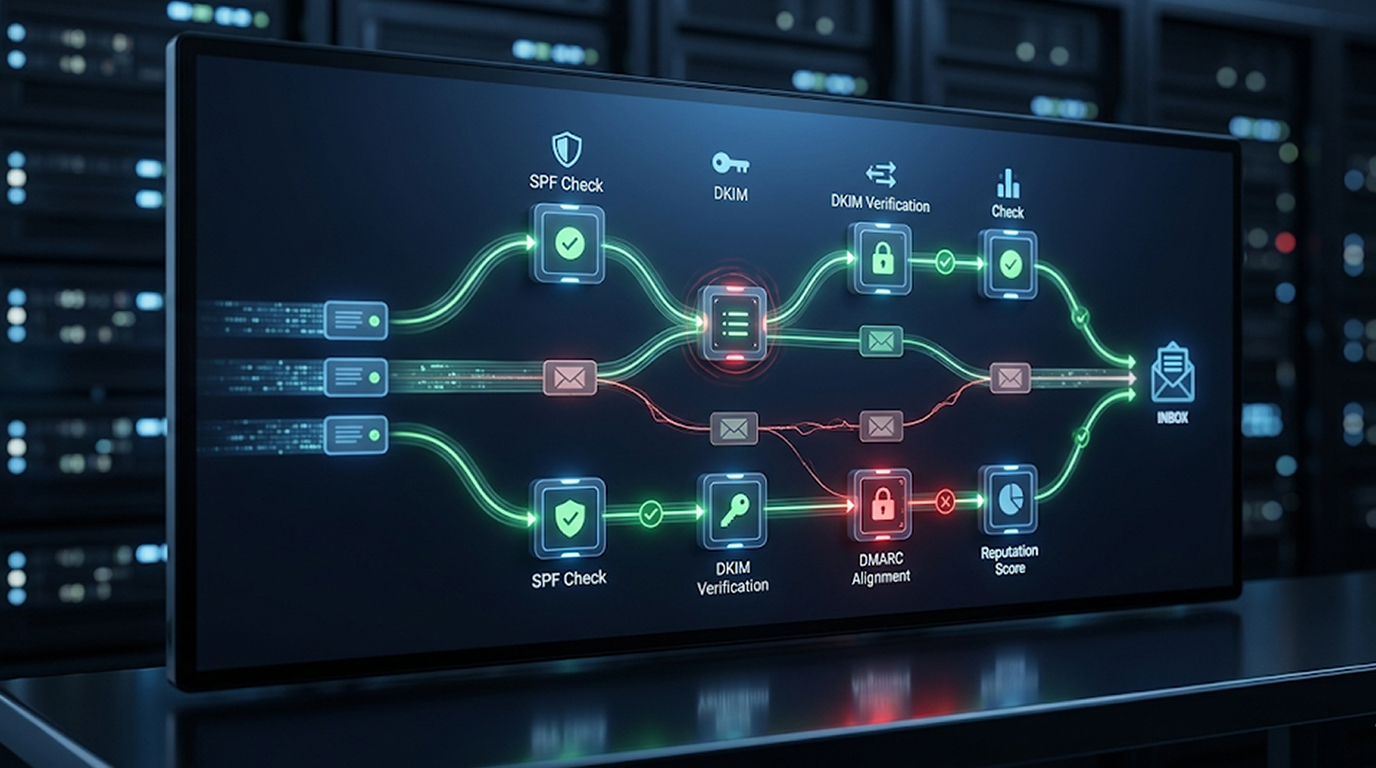
While there has been a significant improvement in the use of SPF, DKIM, and DMARC, sophisticated methods for email spoofing are still able to succeed in 20...
Users often have two needs in conflict: 1. Convenience.2. Privacy.Business objectives create the same tension:1. Easy onboarding means a high conversi...
Not every compromised website is used to steal data or deploy malware.Many are repurposed quietly to generate traffic.The site stays online.Pages still loa...
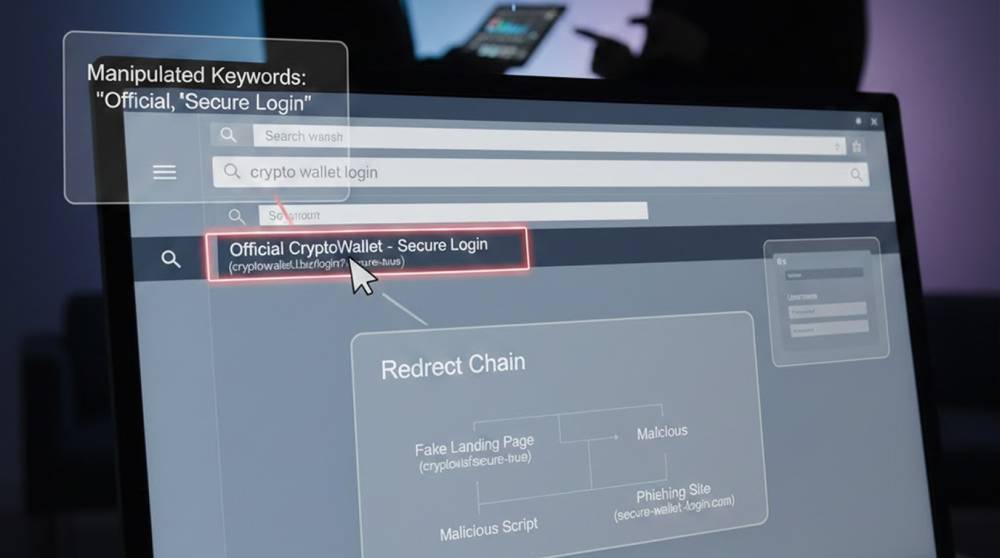
Some phishing campaigns never send a message.Instead of pushing links into inboxes, attackers wait for users to search.The trust comes from Google, not the...
Cross-Site Request Forgery (CSRF) attacks are one of the most underrated web attacks, and this is even more common in legacy applications, particularly in...
Cybersecurity researchers have identified SpyLoan, a malware embedded in more than a dozen Android apps available on the Google Play Store, collectively do...
In an increasingly digital world, having a modern website is no longer just a matter of aesthetics; it’s a critical component of cybersecurity. A con...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067