Operation IXIM: The 2 Million Rogue Updates
Security researchers often find themselves waiting for a vendor to release a patch, but when the vendor is a decade-old abandoned piracy app, waiting is no...
Found 18 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Security researchers often find themselves waiting for a vendor to release a patch, but when the vendor is a decade-old abandoned piracy app, waiting is no...
Most security teams are drowning in work. There are applications to test, compliance deadlines to hit, and a never-ending stream of vulnerabilities to chas...
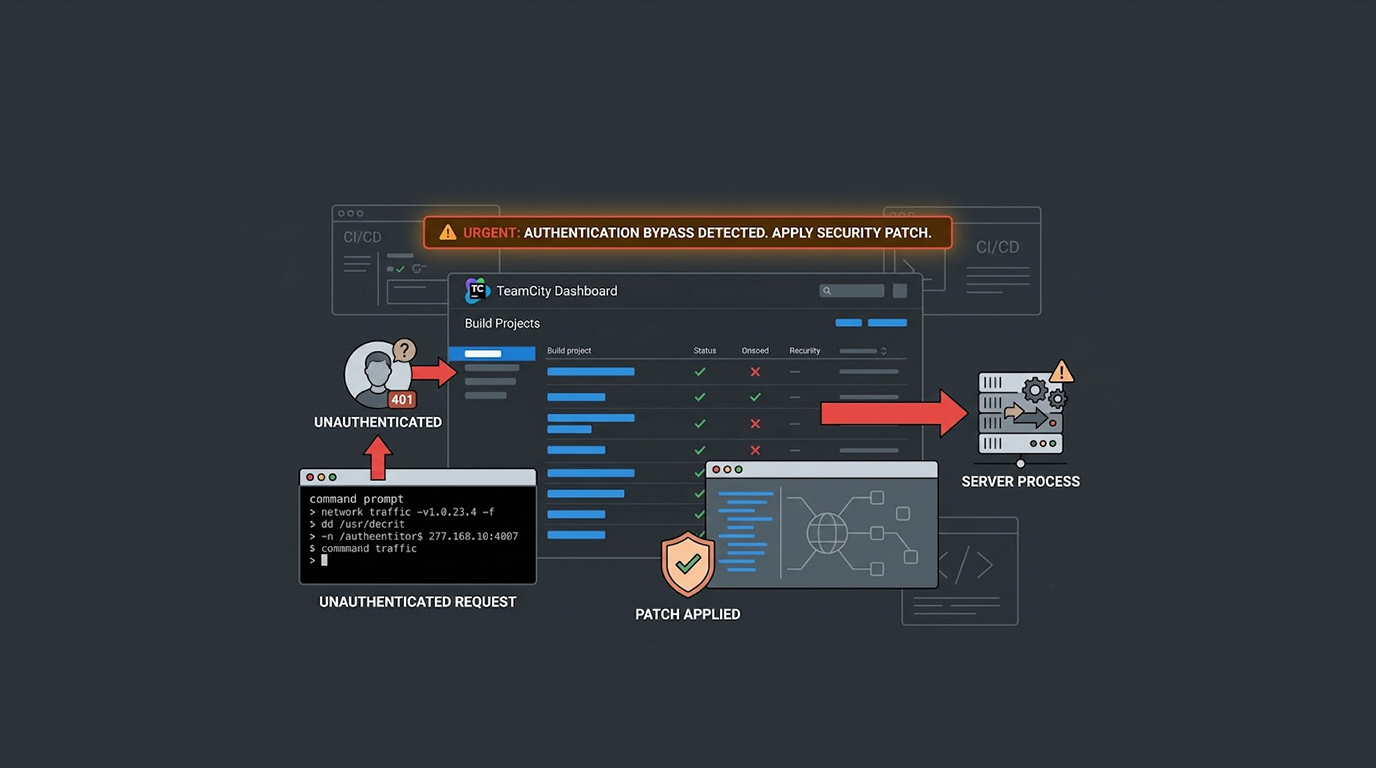
If you are running an on-premises version of JetBrains TeamCity, you have a critical update to apply. A security vulnerability has been discovered that cou...
You are in a coffee shop typing on your laptop. Music plays softly from the speakers above. You do not think twice about it. It is just background noise....
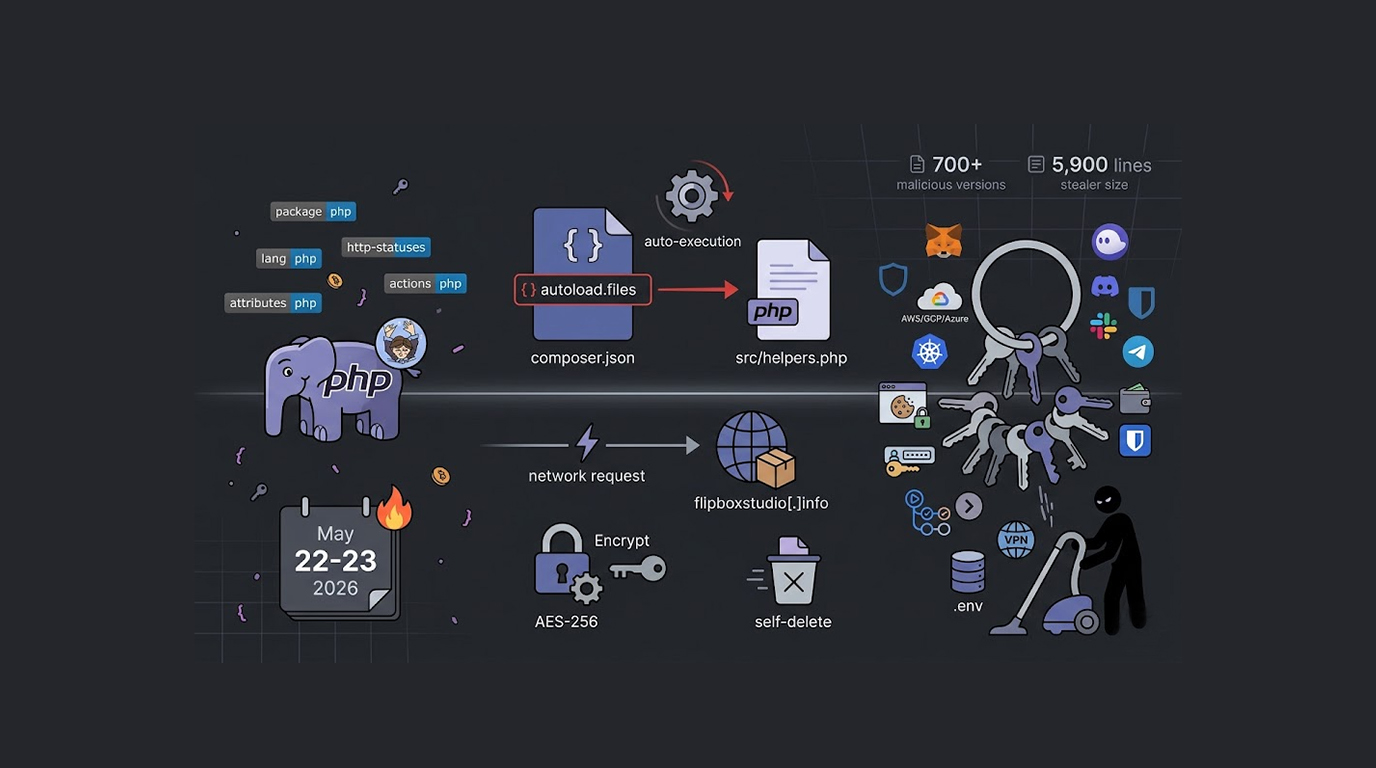
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
You sit down at your computer. You need to edit a configuration file. You open Notepad++. It has been on your machine for years. Lightweight. Fast. Trustwo...
New malware called STX RAT was discovered as the first RAT to be able to use invisibility techniques and perform a variety of operations. This was first se...
In the last couple of years, the cybersecurity community has started seeing a new family of threats nicknamed “Sponge” malware. These aren&rsqu...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067