indexed-btree Malicious npm Package Uses Runtime Code
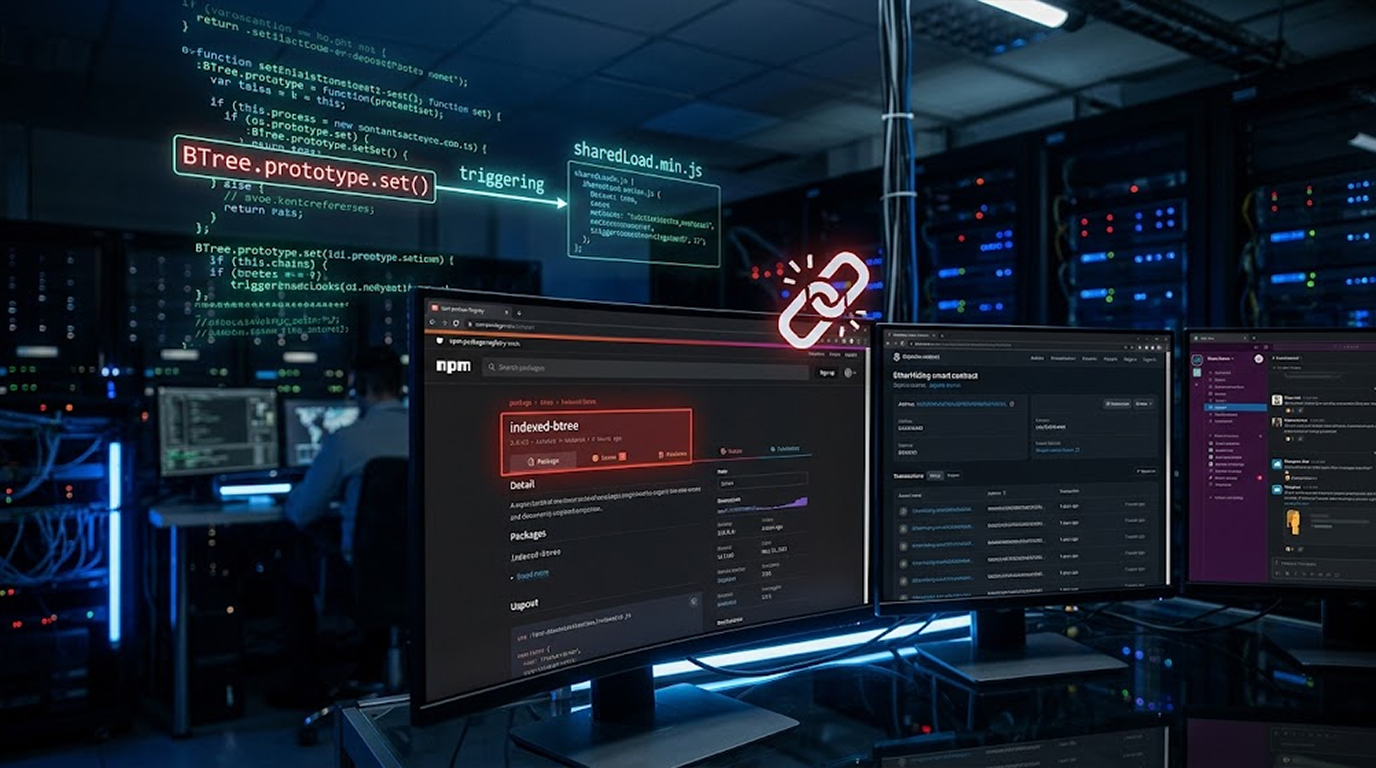
A malicious npm package called indexed-btree has been caught hiding its payload inside application code, rather than using lifecycle scripts, which is a si...
Found 4 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A malicious npm package called indexed-btree has been caught hiding its payload inside application code, rather than using lifecycle scripts, which is a si...
Signed Windows tools are:1. Trusted by the operating system2. Often allowed by security policies3. Installed by default Attackers don’t need malware...
Most breaches don’t begin with malware detonating everywhere.They begin quietly.Someone logs in.They look around.They test limits.If you replay the l...
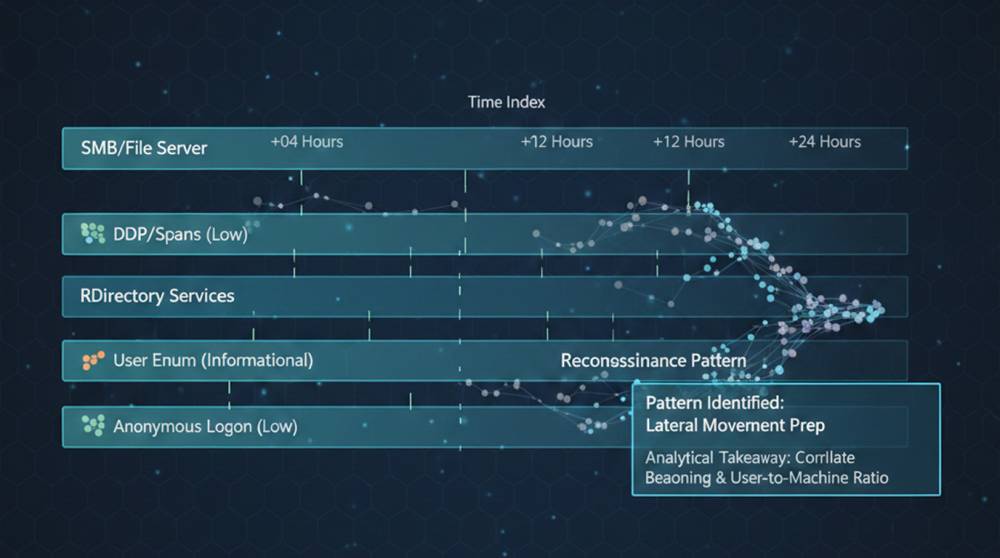
Network reconnaissance isn’t loud, it doesn’t trip alarms or crash systems, it’s someone looking around carefully, touching many things a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067