VMware vCenter CVE-2026-59310 Exploitation Underway
Threat actors have started to target a critical security vulnerability that has been recently patched by Broadcom VMware vCenter. The vulnerability gives a...
Found 30 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Threat actors have started to target a critical security vulnerability that has been recently patched by Broadcom VMware vCenter. The vulnerability gives a...
You just copied your crypto wallet address. You paste it into the transaction window, you double-check it looks right, and you hit send. Your money is gone...
You find yourself sitting in a job interview for a role in Cybersecurity when the interviewer leans forward with genuine interest and asks, “What is...
The Vietnam-aligned threat actor known as OceanLotus has spent more than a decade targeting foreign entities, especially China. But something changed recen...
PHANTOMPULSE RAT is a newly developed and highly advanced Remote Access Trojan (RAT) that is getting a lot of attention within the cybersecurity community...
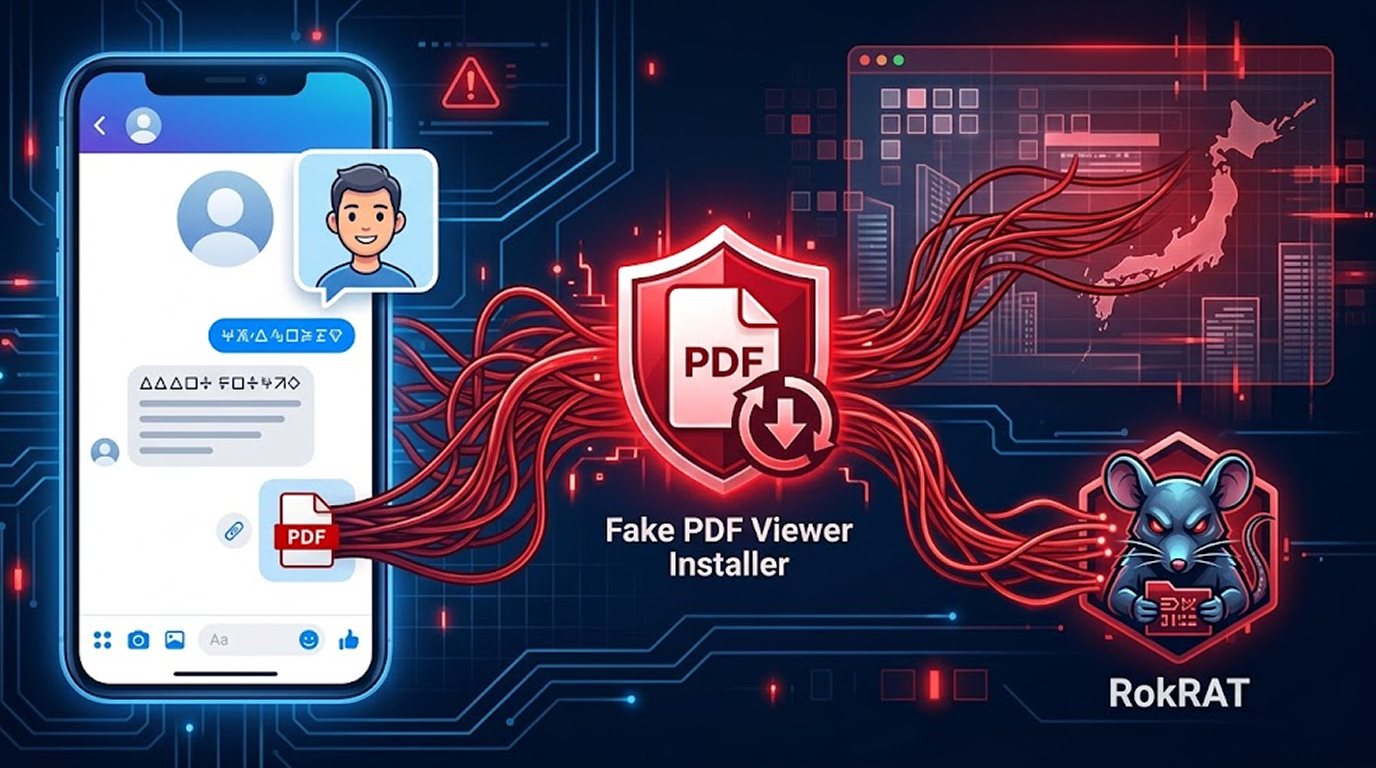
The North Korean hacking group known as APT37 (also called ScarCruft) has been linked to a targeted social engineering campaign that uses Facebook to deliv...
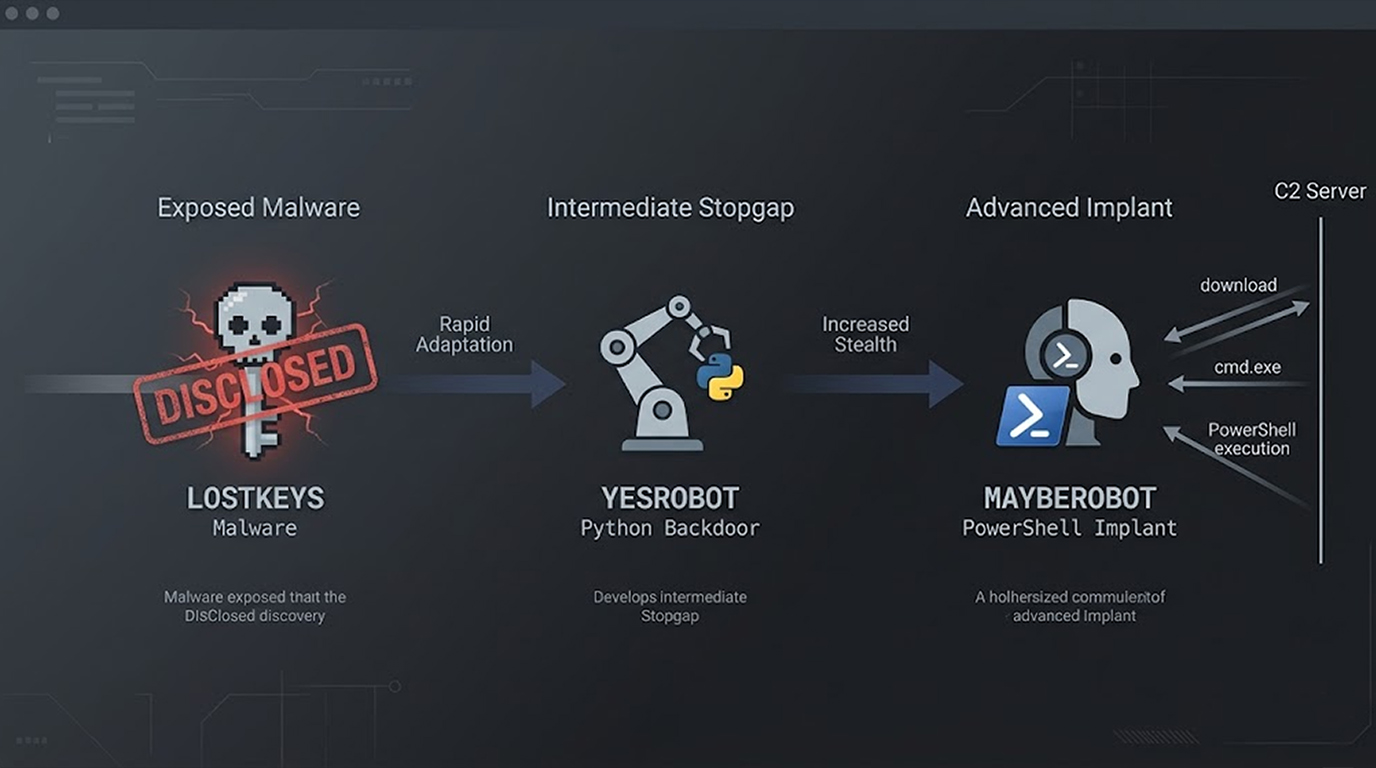
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not t...
The term "Garage APTs" (Advanced Persistent Threats/small teams) in cyber security defines entities that are small, but now can implement APT level operati...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067