How Attackers Discover and Exploit Shared Credentials in Cloud Environments
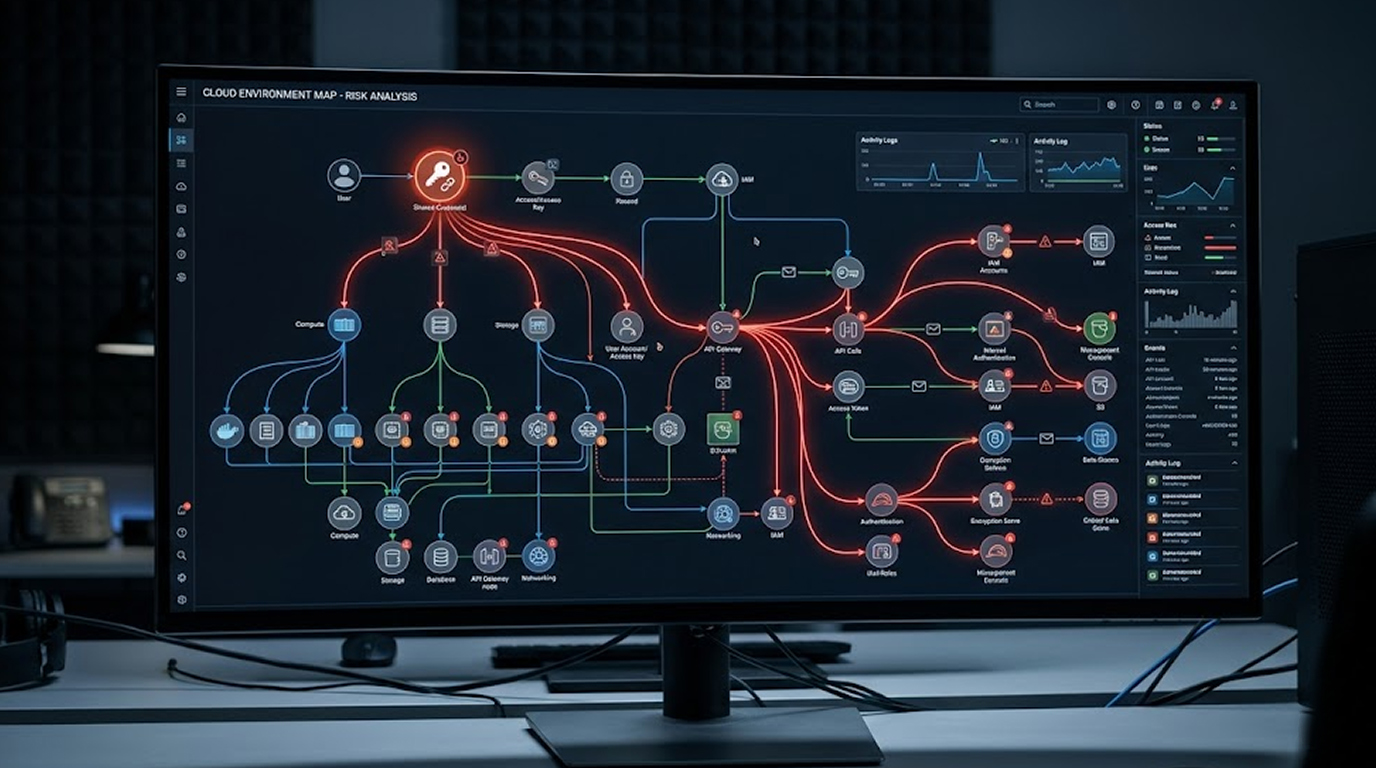
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
Found 185 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
New malware called STX RAT was discovered as the first RAT to be able to use invisibility techniques and perform a variety of operations. This was first se...
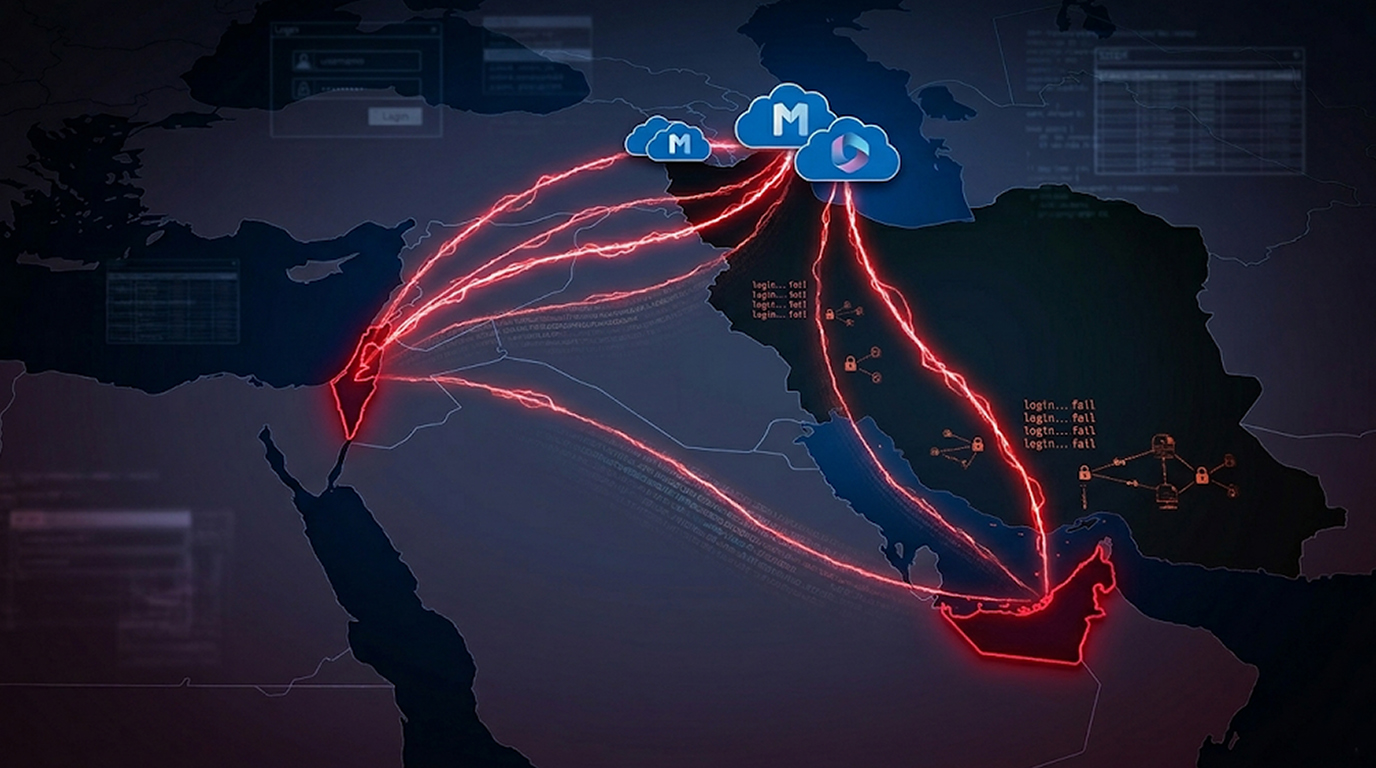
In March 2026, a threat actor aligned with Iran has conducted password-spraying attacks on Microsoft 365 accounts located in both Israel and the United Ara...
DarkSword is an advanced iOS spying framework that has been in use to conduct highly targeted attacks since late in 2025. DarkSword is so dangerous because...
WhatsApp and Telegram have become two of the most common delivery channels for scams and malware in 2026. Attackers send files disguised as “AI filte...
When you receive a “login from an unusual location” alert, whether from Google, Microsoft, Apple, your bank, or a crypto exchange, it’s e...
A China-based cybercriminal group known as Silver Fox (also referred to as SwimSnake / Valley Thief / Void Arachne) is currently using a typosquatting tech...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067