AUR Malware Attack: 400+ Packages Hijacked
Here's a nightmare scenario for Arch Linux users. You install or update a package from the Arch User Repository, the community-driven collection that makes...
Found 113 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Here's a nightmare scenario for Arch Linux users. You install or update a package from the Arch User Repository, the community-driven collection that makes...
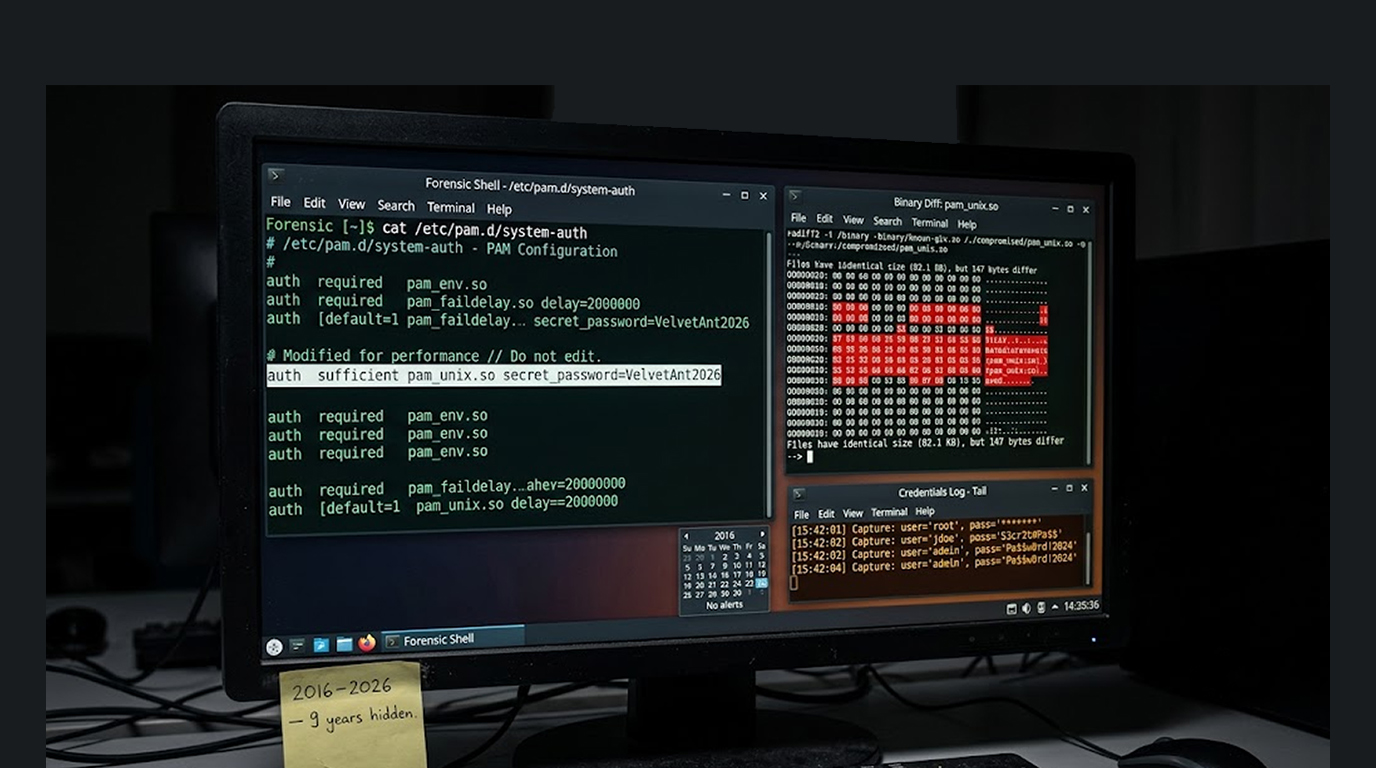
For nearly a decade, a China-nexus threat group avoided every tool defenders use to catch intruders. They didn't drop suspicious files on laptops or server...
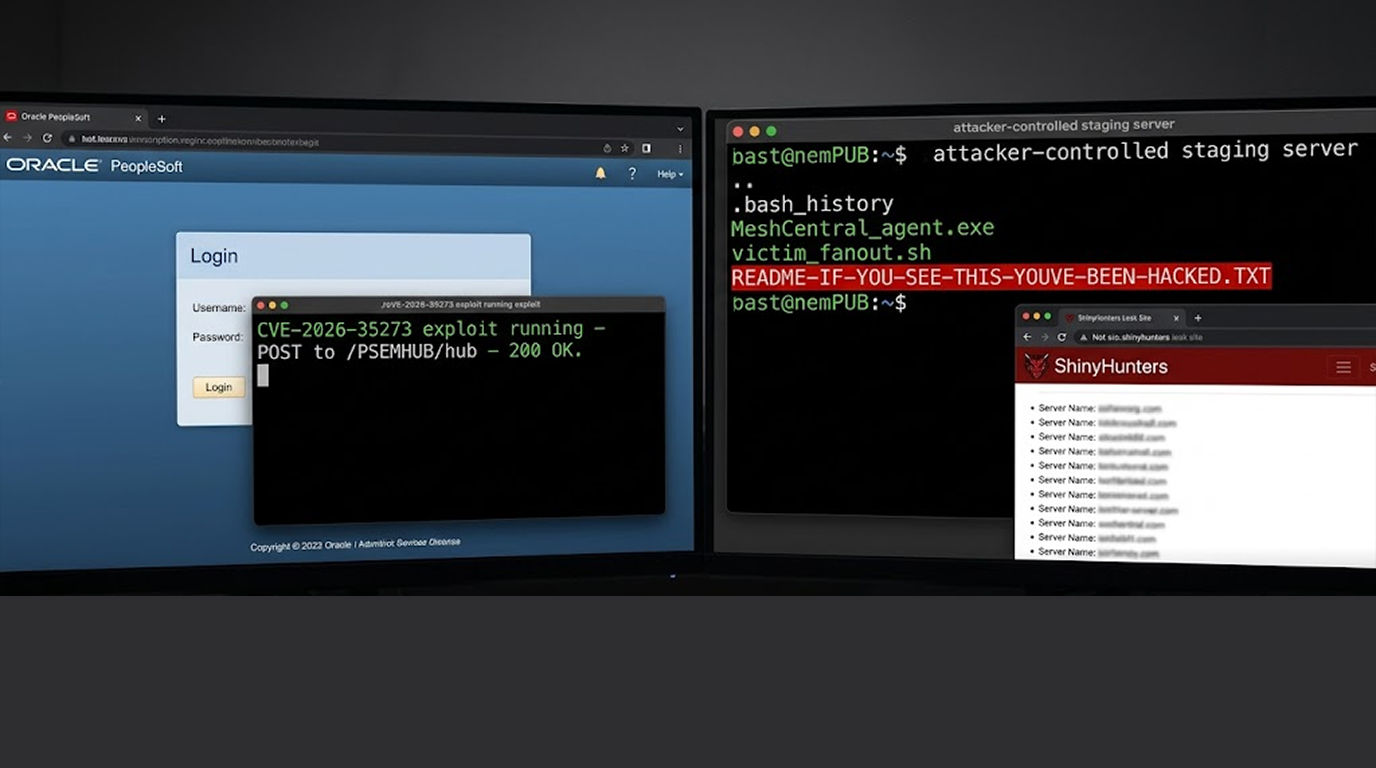
The ShinyHunters extortion crew pulled off something unusual. They exploited an unpatched vulnerability in Oracle PeopleSoft to break into enterprise syste...
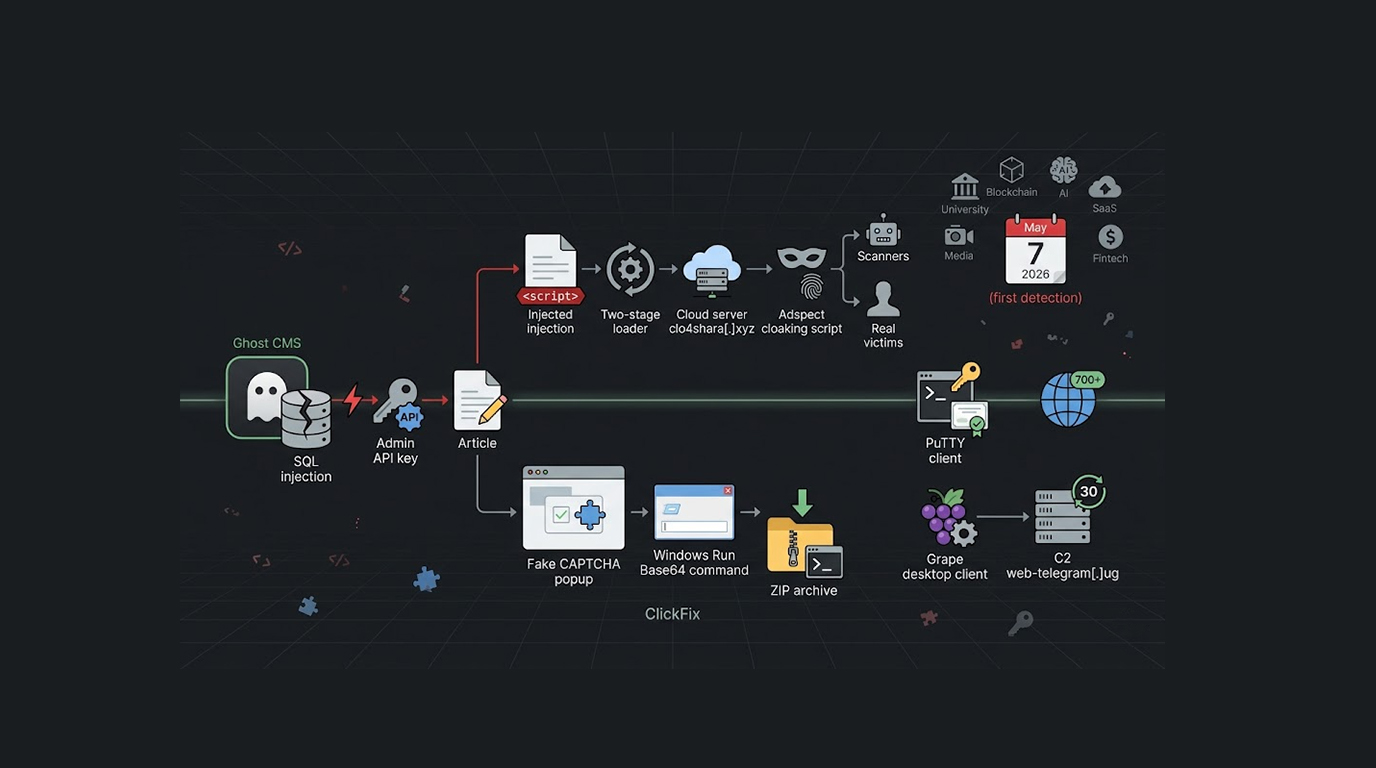
Threat actors took advantage of a critical SQL injection vulnerability present in Ghost CMS to insert malicious Javascript code into ClickFix campaigns lau...
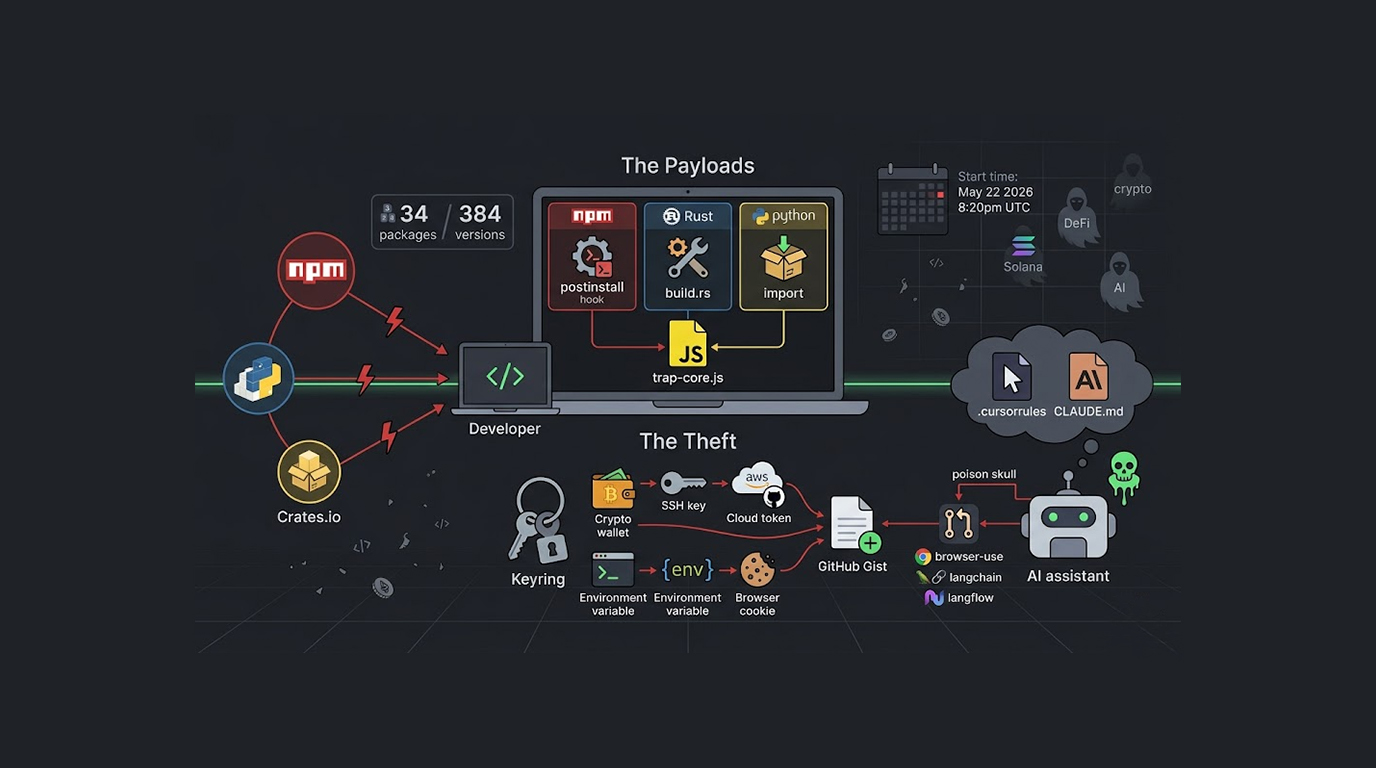
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
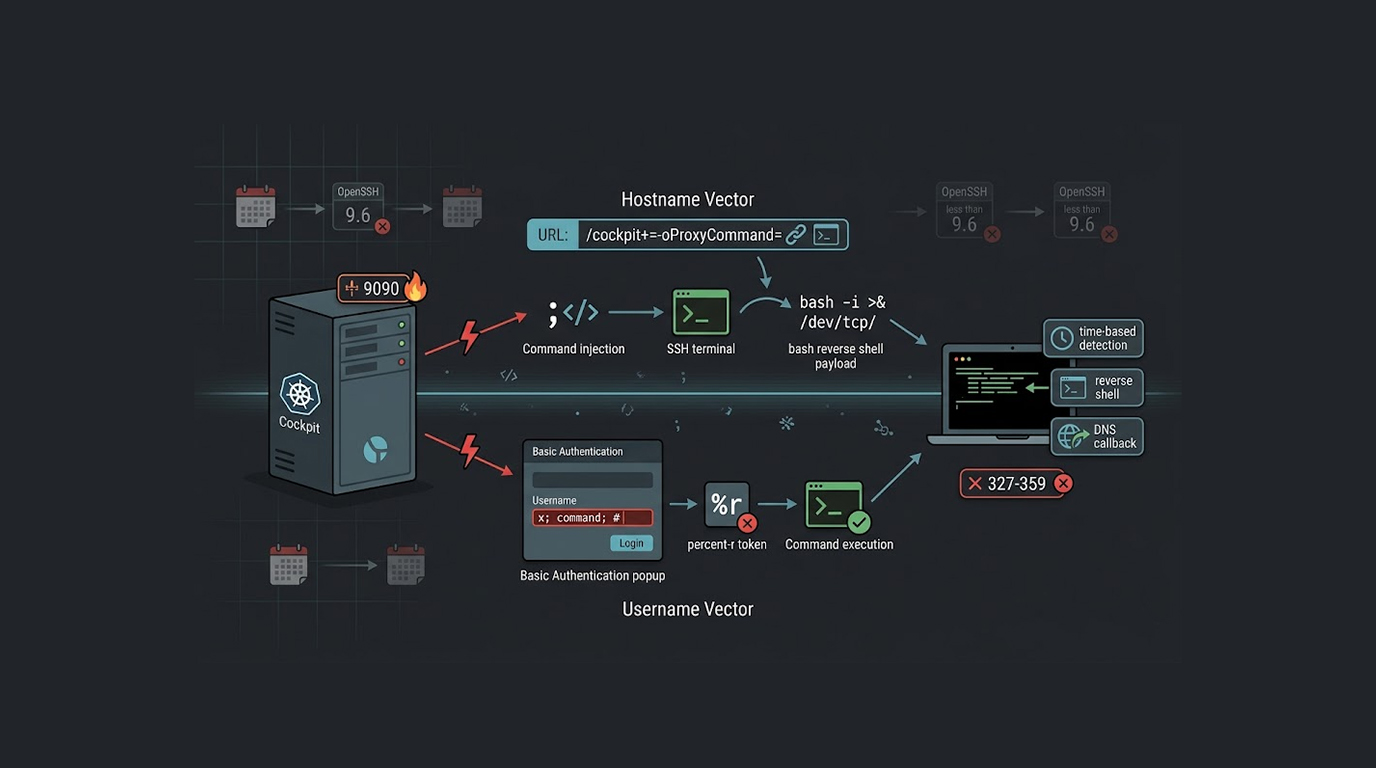
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
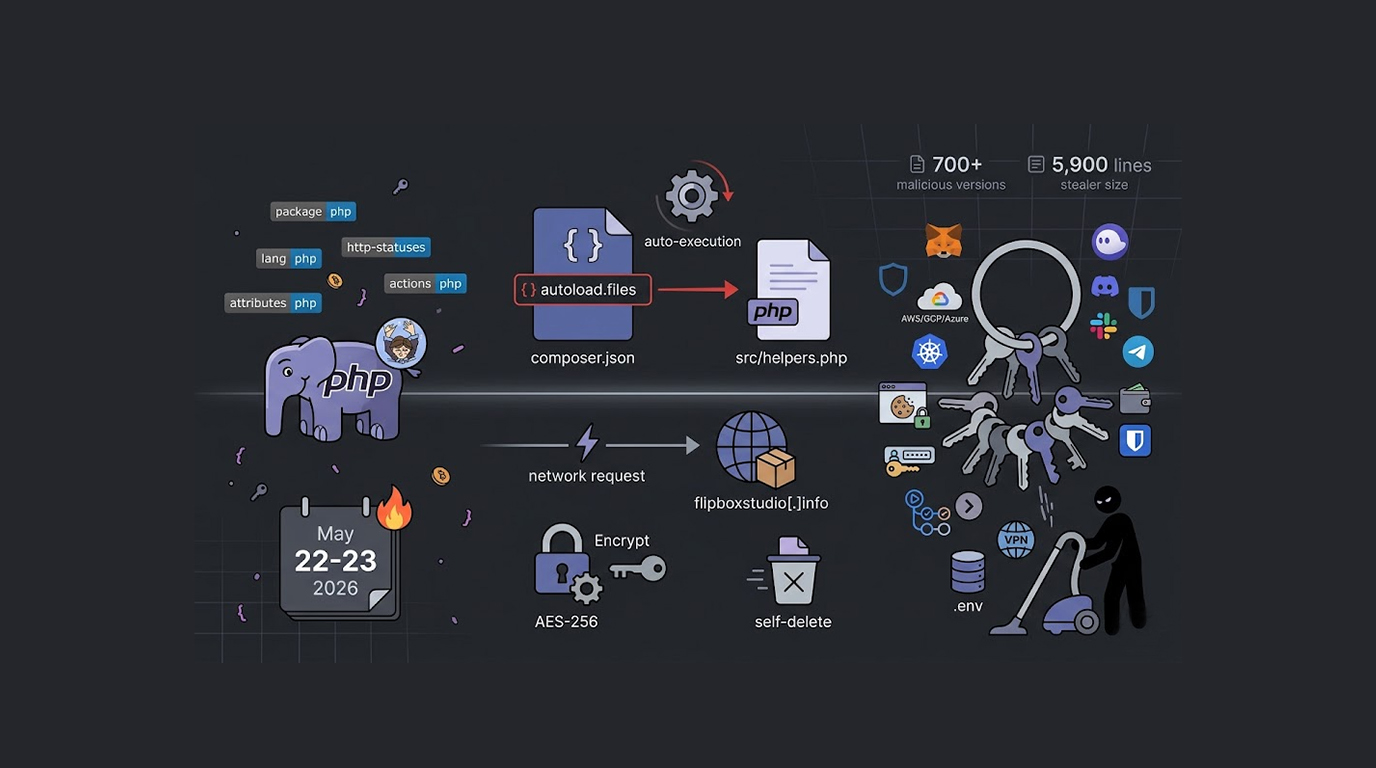
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
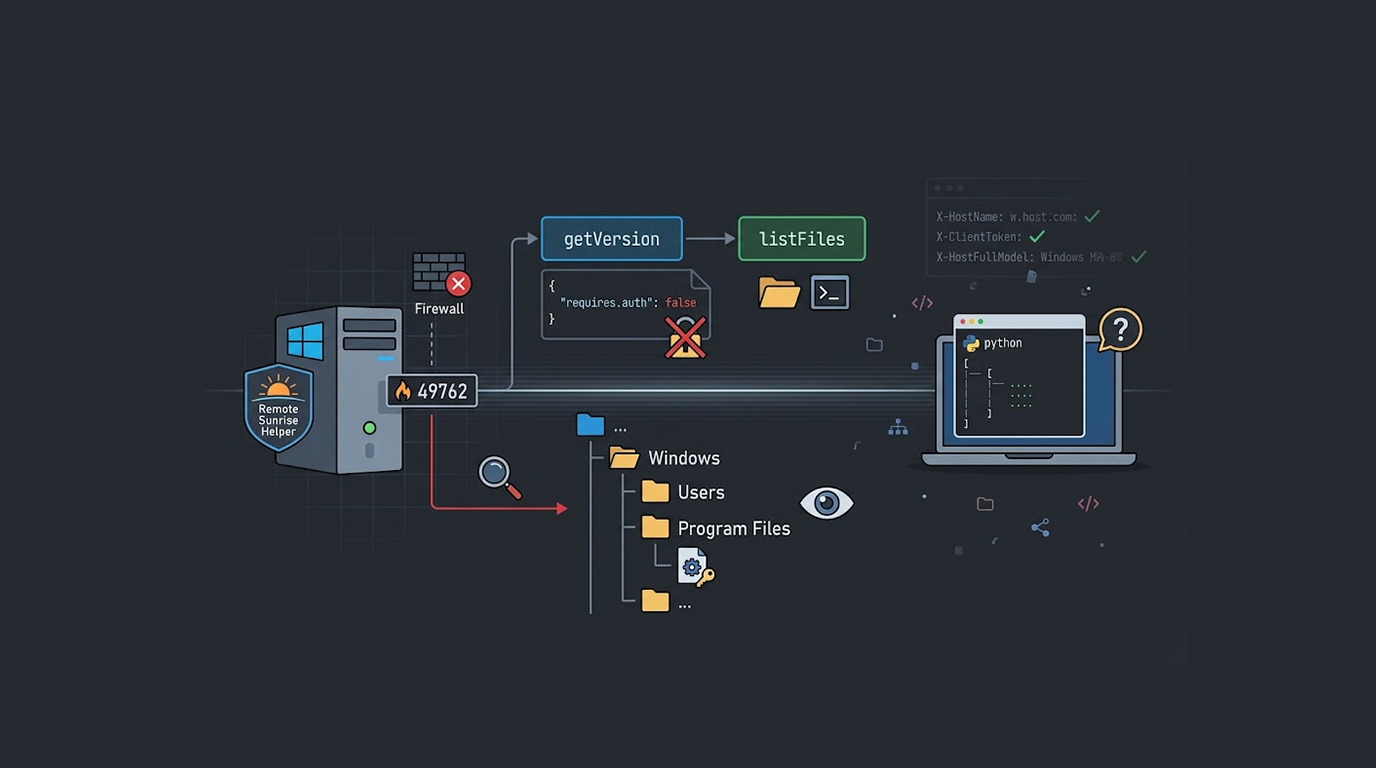
An issue with Remote Sunrise Helper, made by RS Ltd for Windows, allows unauthorized users access to view all files and folders on the device and has since...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067