APT37 Uses Facebook Pretexting to Deliver RokRAT Malware
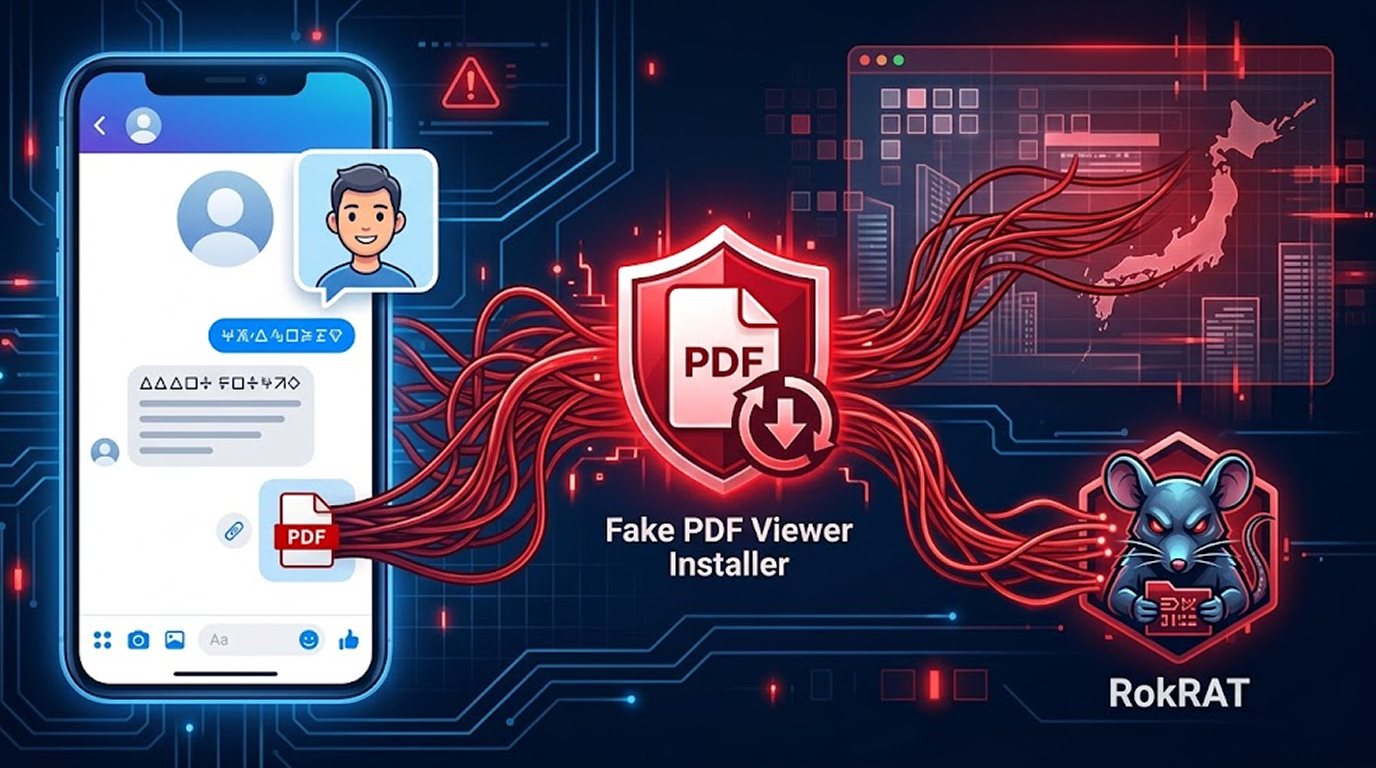
The North Korean hacking group known as APT37 (also called ScarCruft) has been linked to a targeted social engineering campaign that uses Facebook to deliv...
Found 111 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The North Korean hacking group known as APT37 (also called ScarCruft) has been linked to a targeted social engineering campaign that uses Facebook to deliv...
Many organizations invest heavily in security tools, training completion rates, and compliance checklists, yet these often do not lead to a reduction of ac...
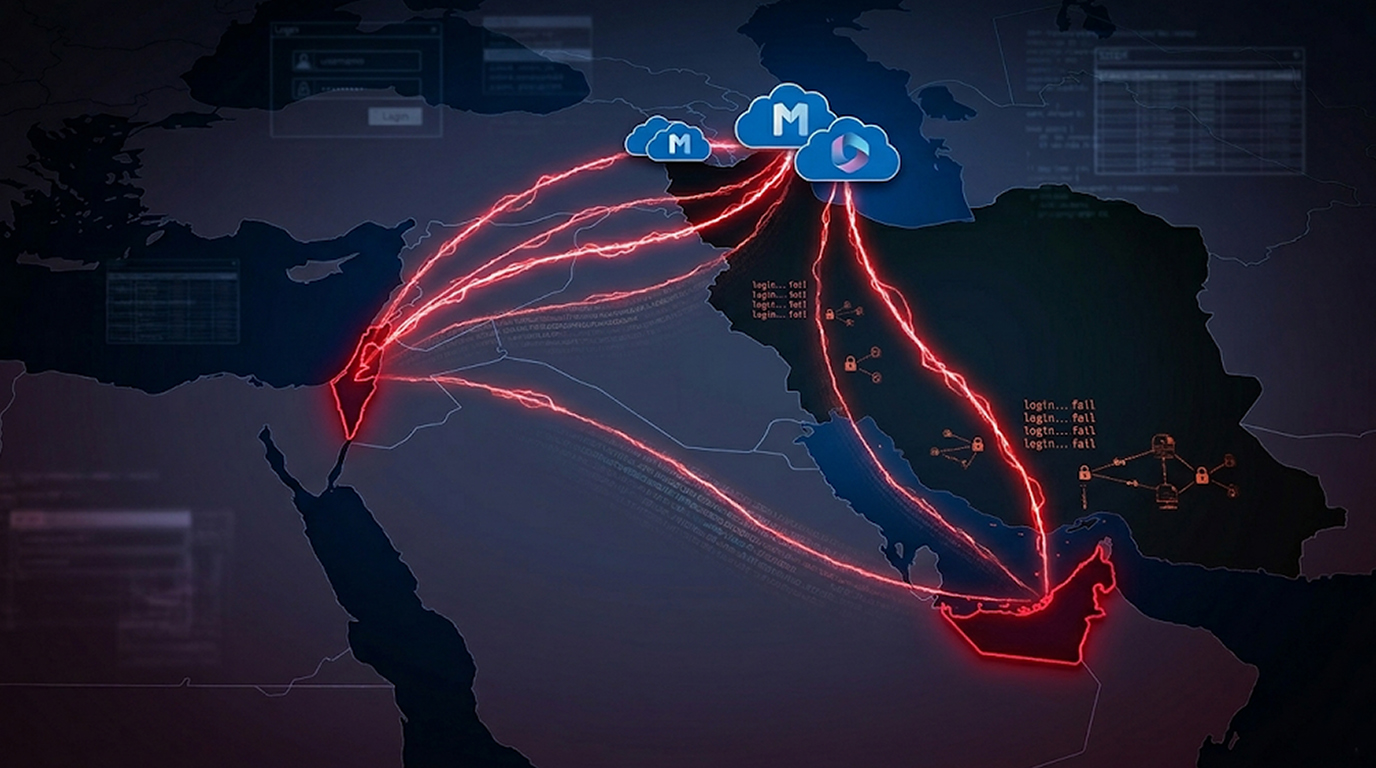
In March 2026, a threat actor aligned with Iran has conducted password-spraying attacks on Microsoft 365 accounts located in both Israel and the United Ara...
According to cybersecurity investigations into an active attack on government organisations in Southeast Asia, there was a zero-day vulnerability in TrueCo...
Your website is down. Customer data is leaking. Orders have stopped. Google has flagged your site as unsafe. For thousands of small-to-medium businesses an...
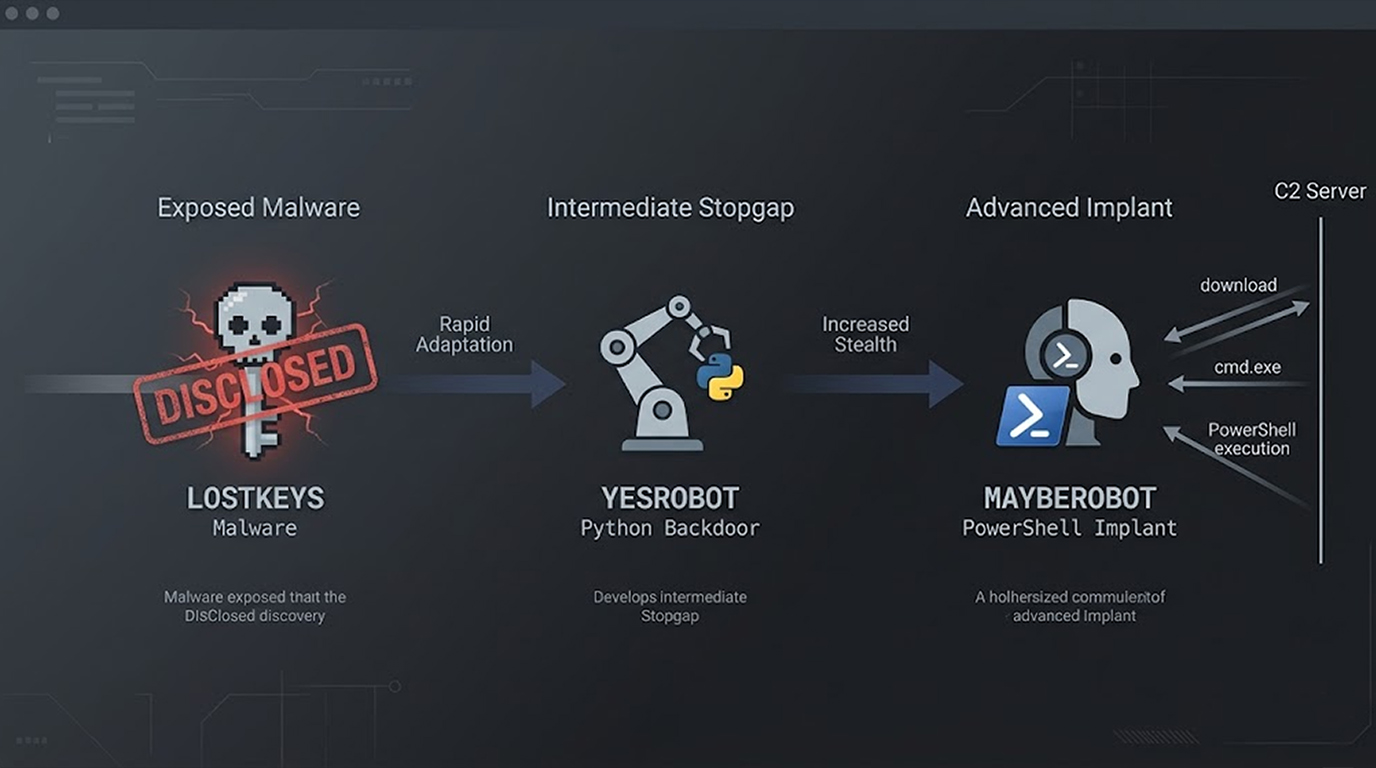
Typically, when a sophisticated threat actor's primary malware is publicly exposed, they will take time to regroup from that event. However, that was not t...
At this moment in March of 2026, hundreds of thousands of cyber attacks happen around the world every hour including instances of malware detection, phishi...
Cybersecurity researchers have spotted yet another clever attempt to slip malicious code into developers' toolkits, this time by impersonating one of the m...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067