Anubis Ransomware Exploits Citrix Bleed 2 for Initial Access
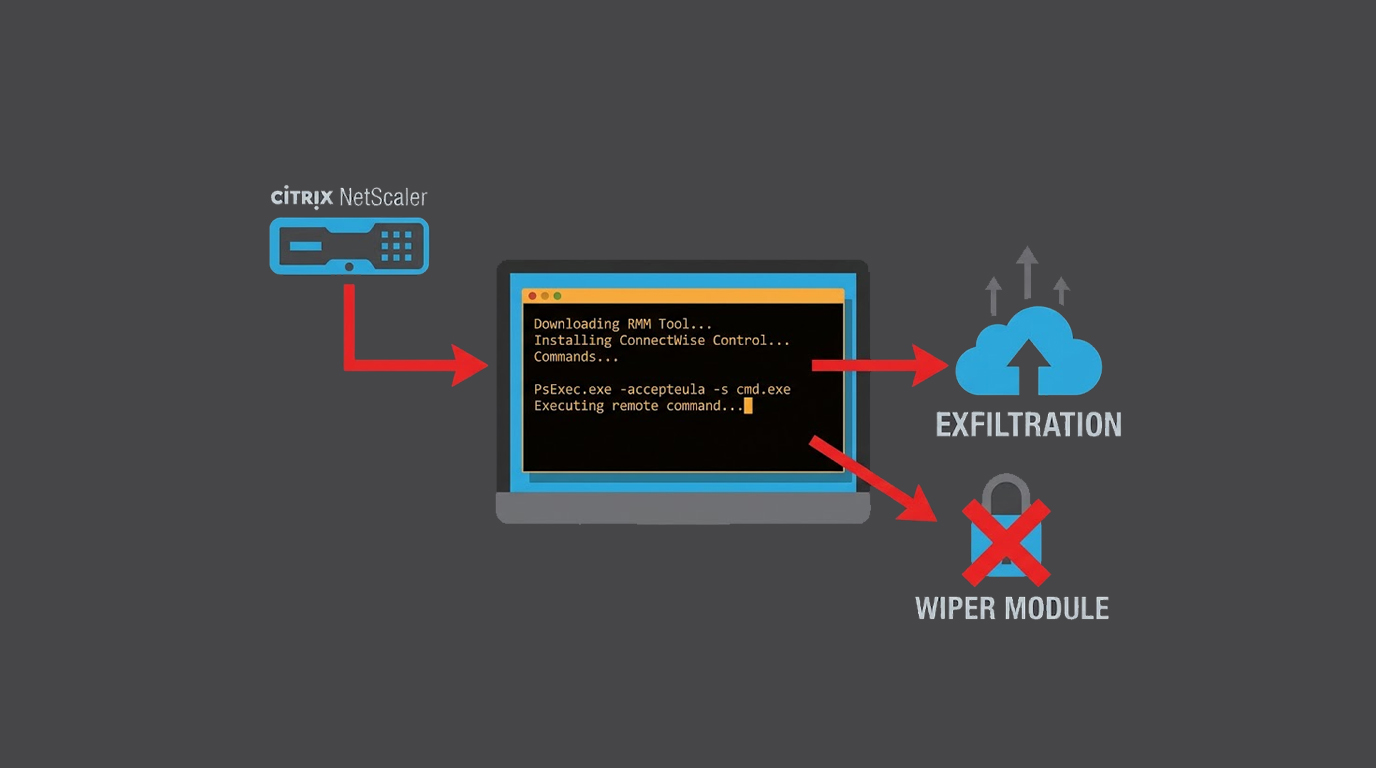
The Anubis Ransomware Campaigns are known to exploit the Citrix Bleed 2 Vulnerability as an initial access vector. The Citrix Bleed 2 Vulnerability i...
Found 63 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The Anubis Ransomware Campaigns are known to exploit the Citrix Bleed 2 Vulnerability as an initial access vector. The Citrix Bleed 2 Vulnerability i...
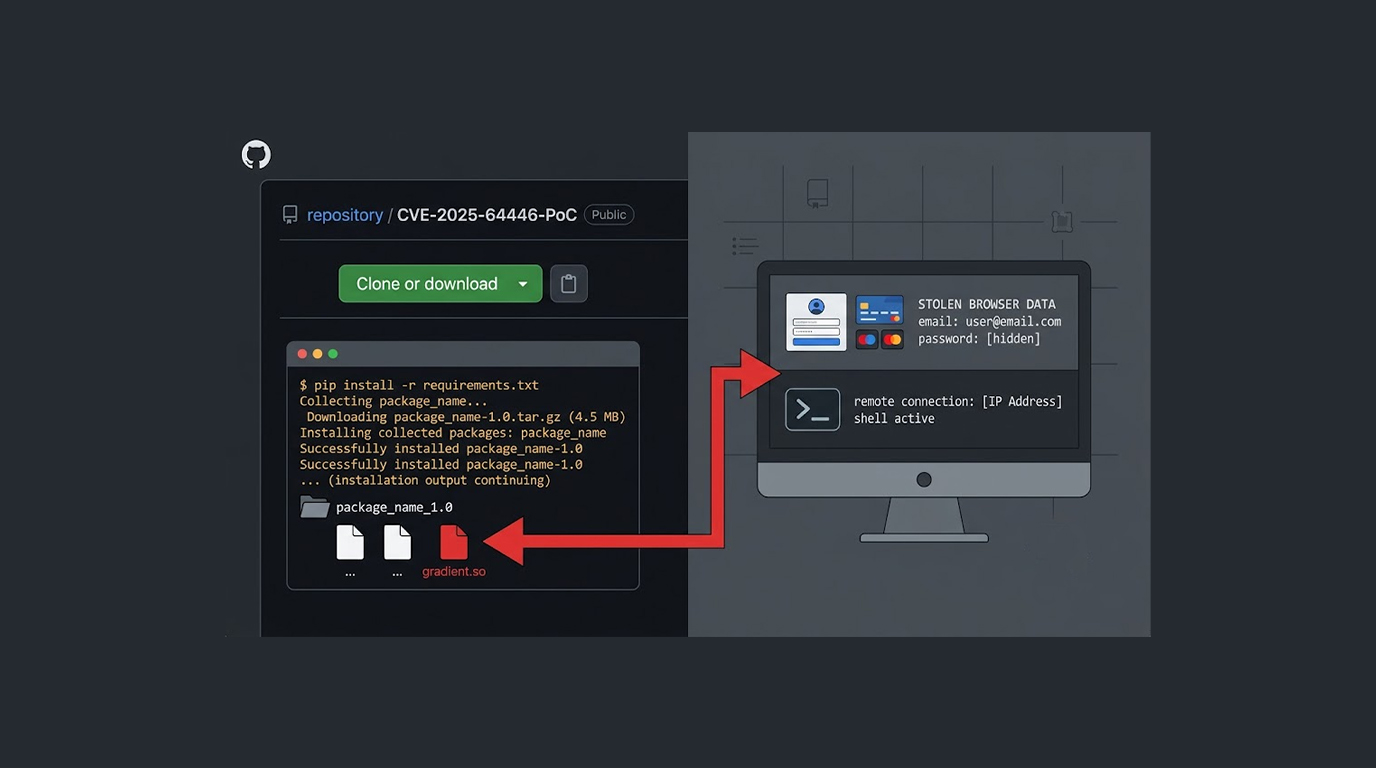
There's a new twist in the ongoing battle between researchers and attackers. Malicious actors are now planting data-stealing malware inside proof-of-concep...
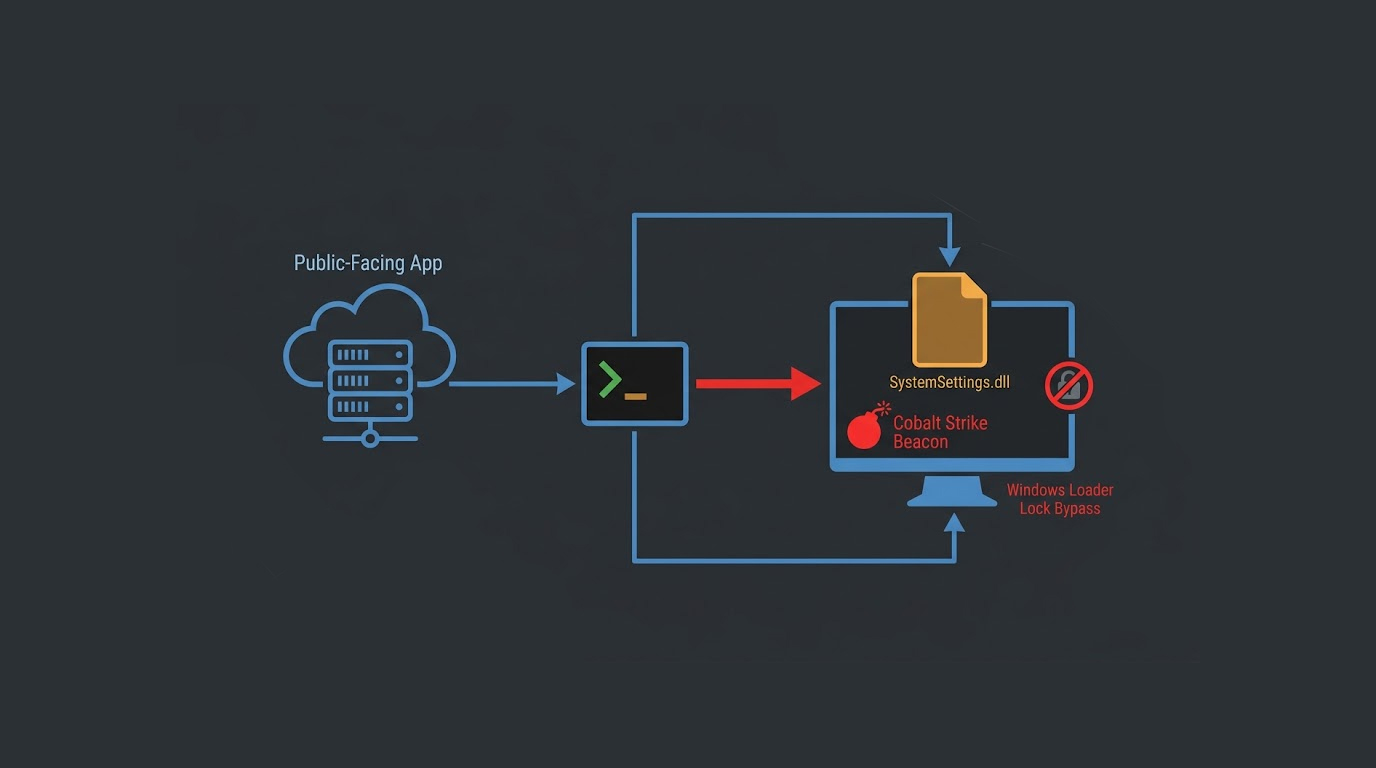
This new wave of attacks includes an unknown variant of malware known as SharkLoader. SharkLoader functions as a loader for distributing Cobalt Strike Beac...
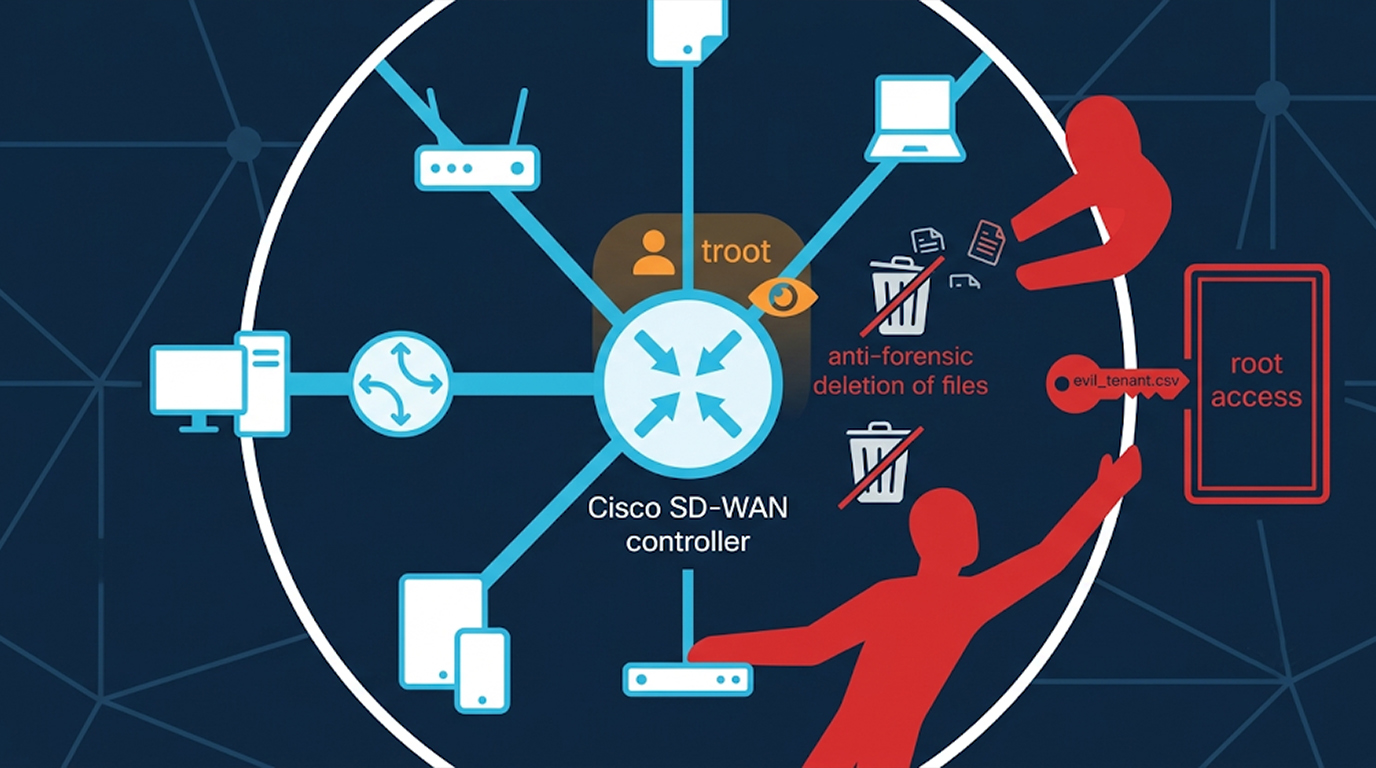
When Cisco disclosed CVE-2026-20245 earlier this month, the company acknowledged that it was already aware of exploitation. Now Mandiant has revealed the f...
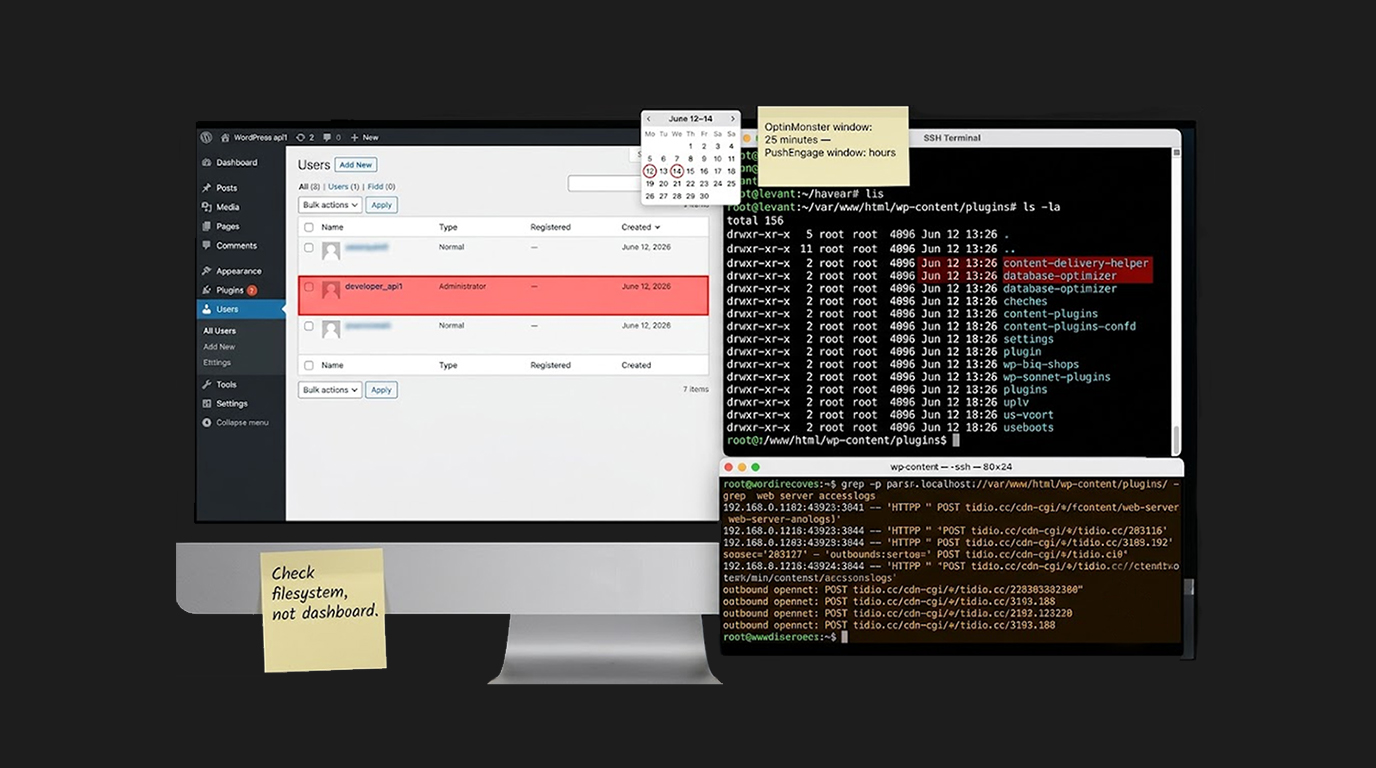
You install PushEngage for push notifications. OptinMonster for popups. TrustPulse for social proof. They are trusted brands. Millions of sites use them.La...
You've now heard of SQLmap, and now you want to try it out for yourself. This tool is definitely powerful, and you would like to see how it works. However,...
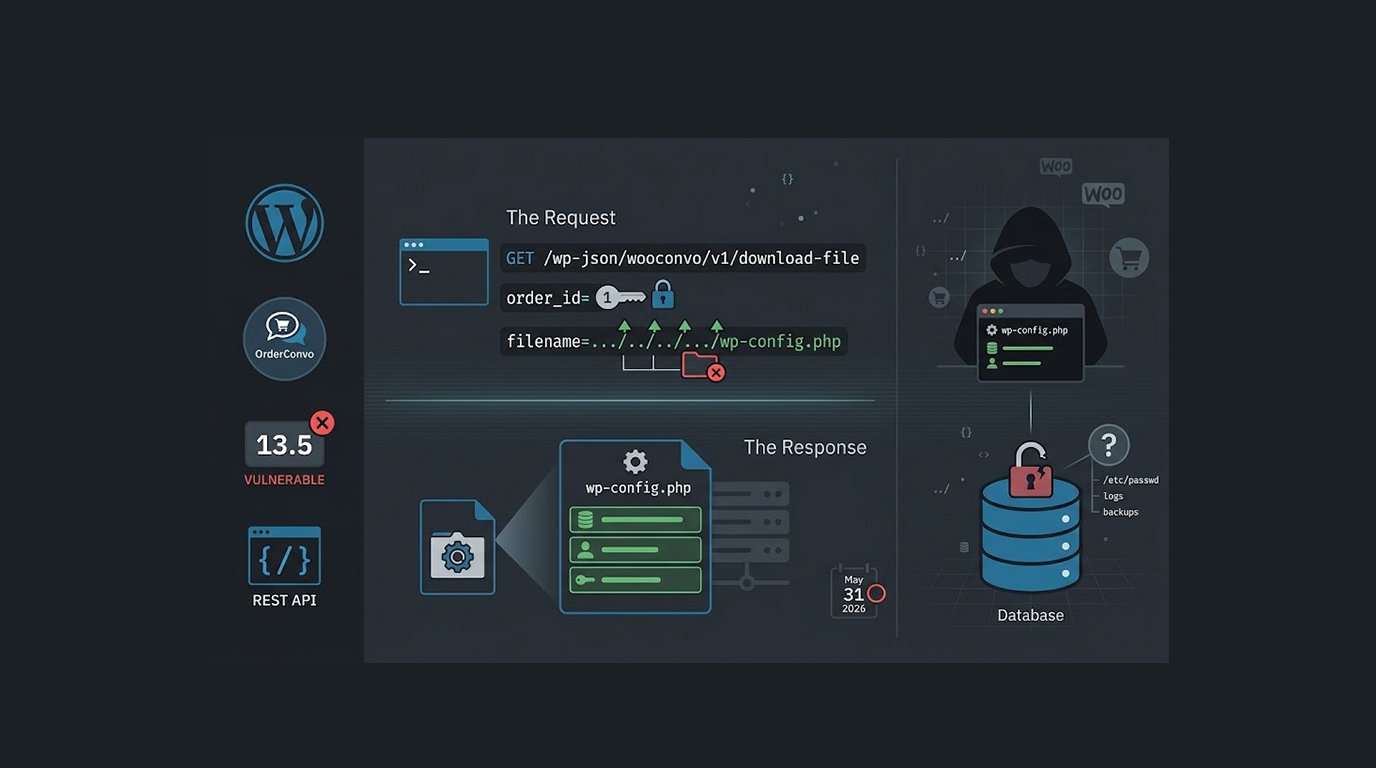
The OrderConvo WooCommerce Plugin contains a security issue that allows users not logged in to a WordPress account to access arbitrary files located on the...
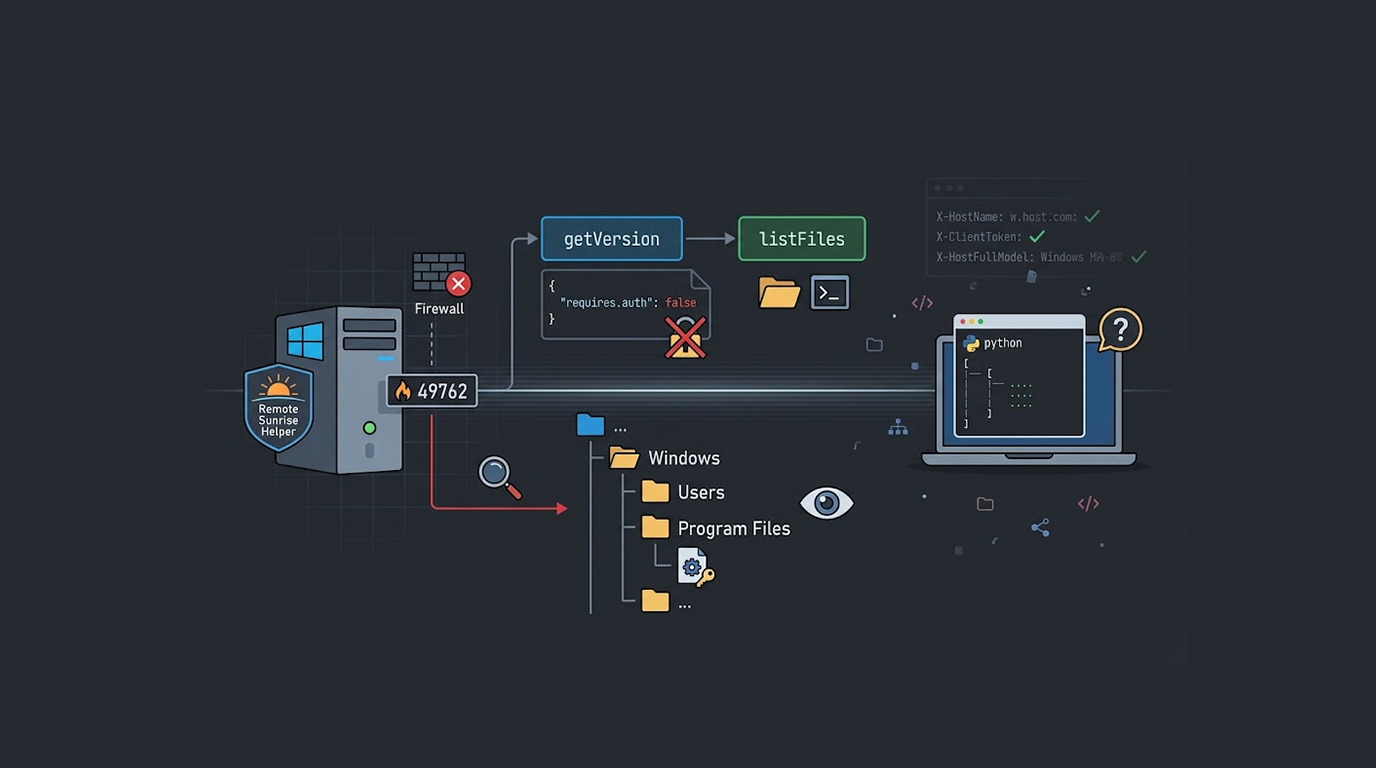
An issue with Remote Sunrise Helper, made by RS Ltd for Windows, allows unauthorized users access to view all files and folders on the device and has since...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067