PDF Forensics: Extracting Metadata & Hidden Payloads Like a Pro
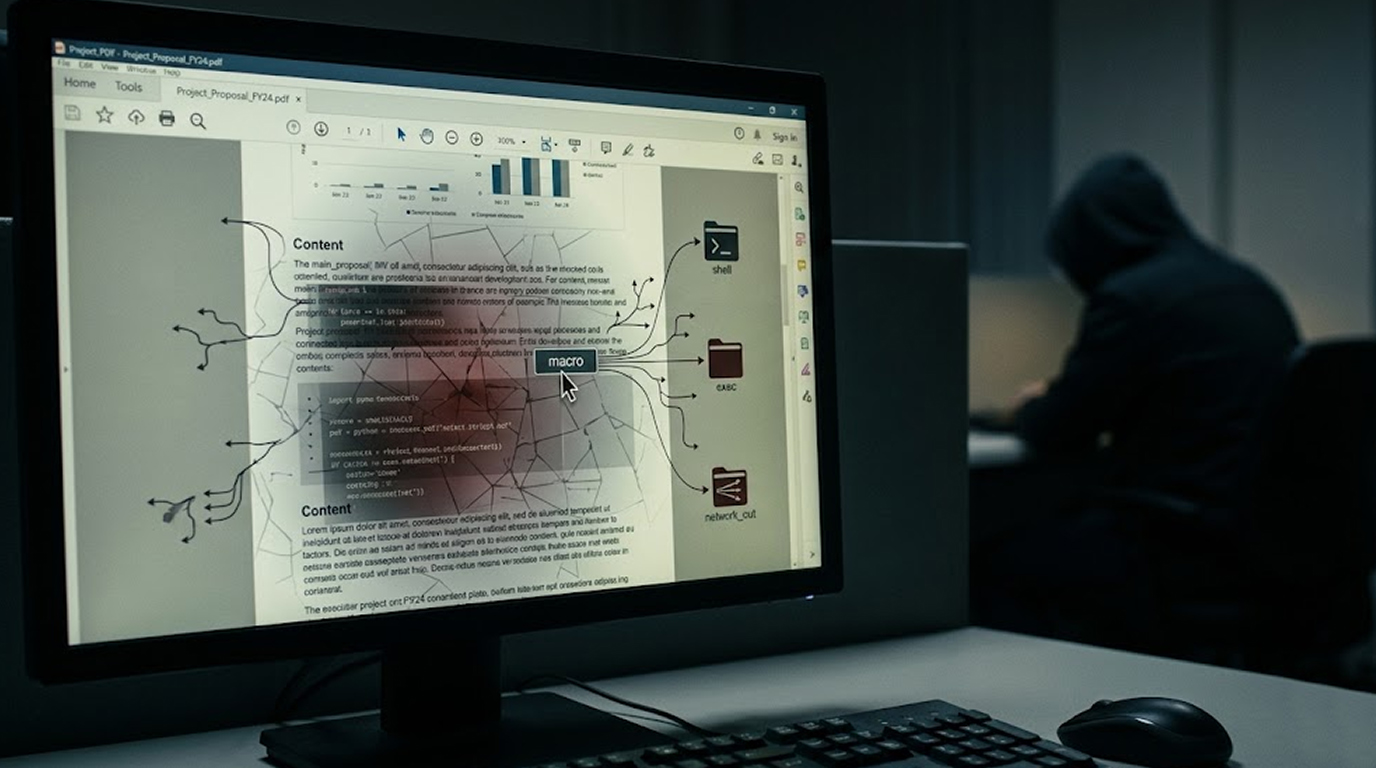
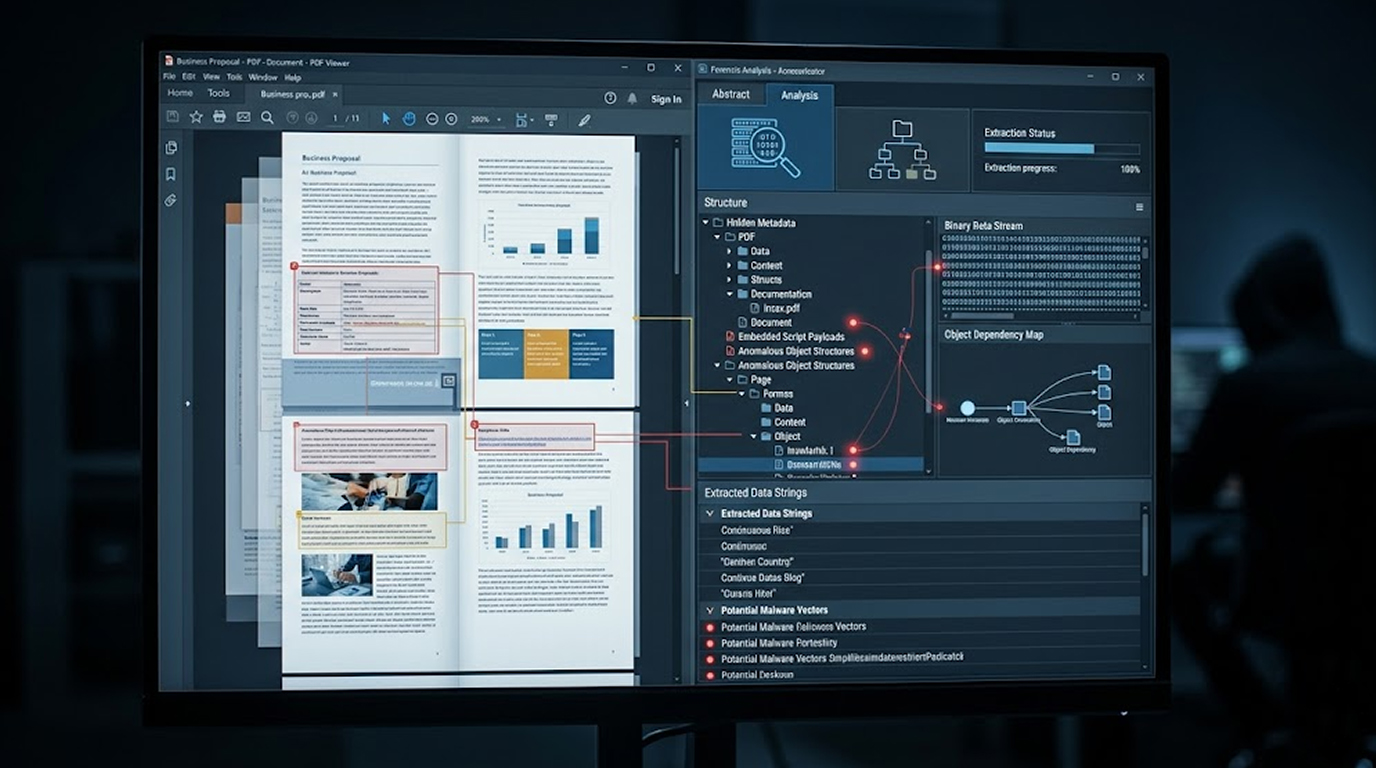
You receive a suspicious PDF. The file name says "Invoice.pdf." The sender is unknown. Your gut says something is wrong.You could delete it. Or you could i...
Found 77 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You receive a suspicious PDF. The file name says "Invoice.pdf." The sender is unknown. Your gut says something is wrong.You could delete it. Or you could i...
You receive an email. It looks important. There is a PDF attachment. The file name suggests an invoice, a contract, or a news update. You double-click it....
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
PHANTOMPULSE RAT is a newly developed and highly advanced Remote Access Trojan (RAT) that is getting a lot of attention within the cybersecurity community...
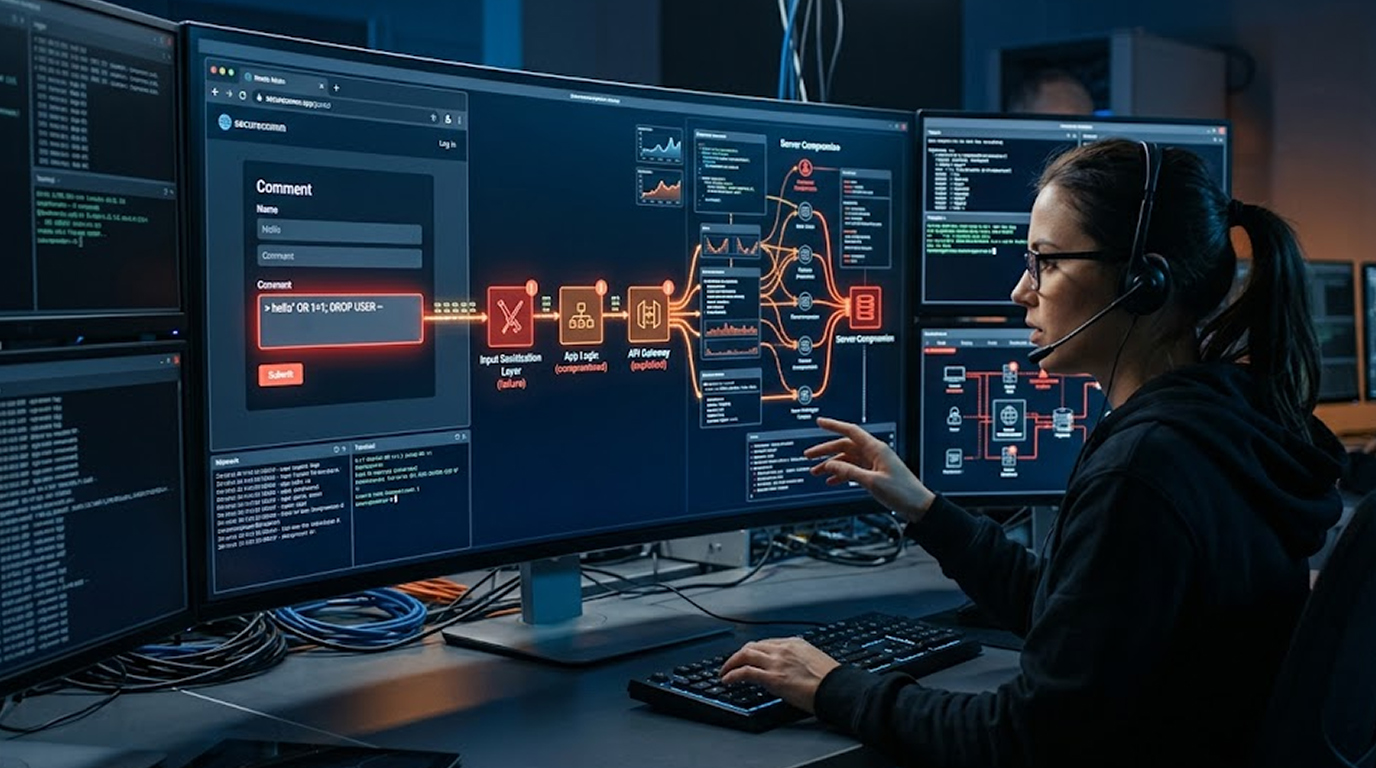
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
As of 2026, webshells still rank among the most consistent methods attackers use to retain persistent access once they achieve RCE for the first time. Alth...
Your website is hacked. Here’s what matters right now. A business owner logs in.Everything looks normal. Traffic? Dropping.Customers? Complaining.G...
The postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in th...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067