API Vulnerabilities in Mobile Apps Explained With Examples
Modern mobile apps are mostly UI.The real logic lives in:1. APIs2. Backend services3. Third party integrationsAttackers rarely attack the app itself.They a...
Found 40 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Modern mobile apps are mostly UI.The real logic lives in:1. APIs2. Backend services3. Third party integrationsAttackers rarely attack the app itself.They a...
In 2026, most work still happens in a browser.Email, cloud apps, admin panels, dashboards, internal tools all run there.Attackers know this.Instead of brea...
Admin panels are not public.That’s exactly why attackers like them.They often contain:1. Trusted data paths2. Fewer validation controls3. Less testin...
Most teams already run scanners.Many still miss XSS.That’s because XSS is rarely a simple input problem.It’s a data-flow and context problem.Re...
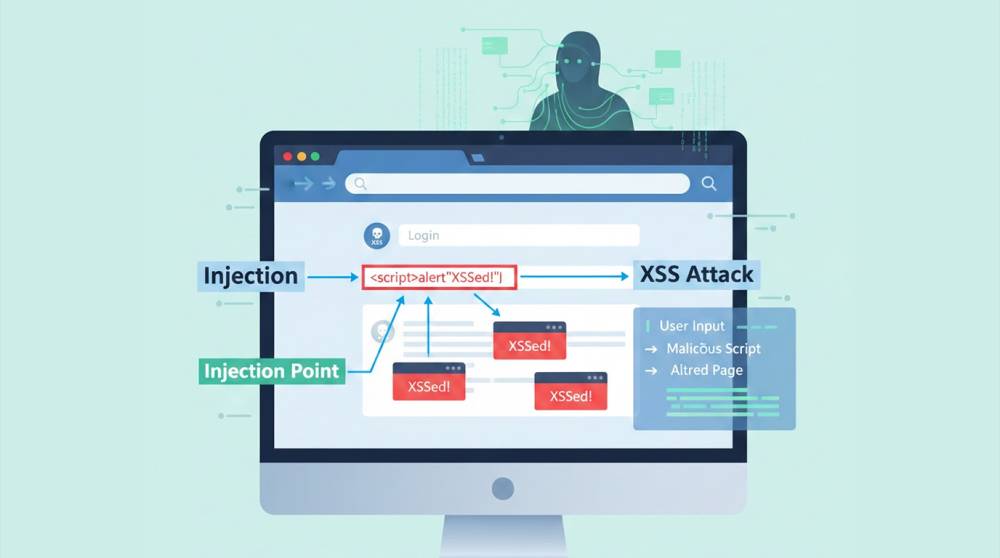
Cross Site Scripting, usually called XSS, happens when a website shows user input without properly checking it first.In simple terms:the website trusts dat...
Companies today rely heavily on web applications for conducting their business. From online banking sites to ecommerce stores, web applications serve three...
Ethical hacking is not abstract theory.It is hands-on work with real applications, real traffic, and real mistakes.The goal is not to show off tools or cod...
Breaking web apps usually doesn’t start with zero-days or Hollywood hacking.It starts with someone opening the same tools developers and testers alre...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067