SSTI Code Injection: Still Works on Major Frameworks in 2026
SSTI (Server Side Template Injection) is an incredibly hazardous as well as often overlooked method of code injection that has been used against modern web...
Found 427 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
SSTI (Server Side Template Injection) is an incredibly hazardous as well as often overlooked method of code injection that has been used against modern web...
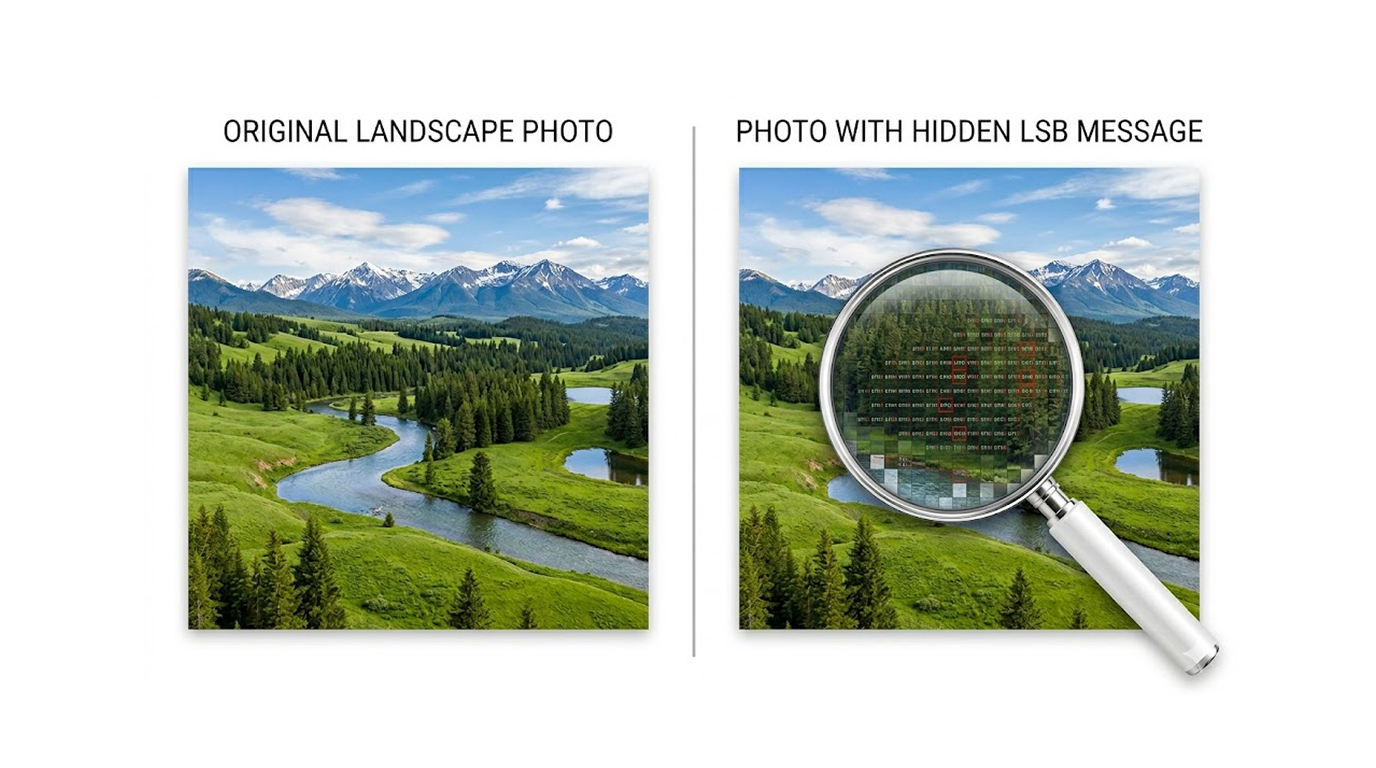
Steganography is a technique that hides an image/data in such a way that it appears innocent to an outside observer. Unlike encryption, where an encrypted...
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
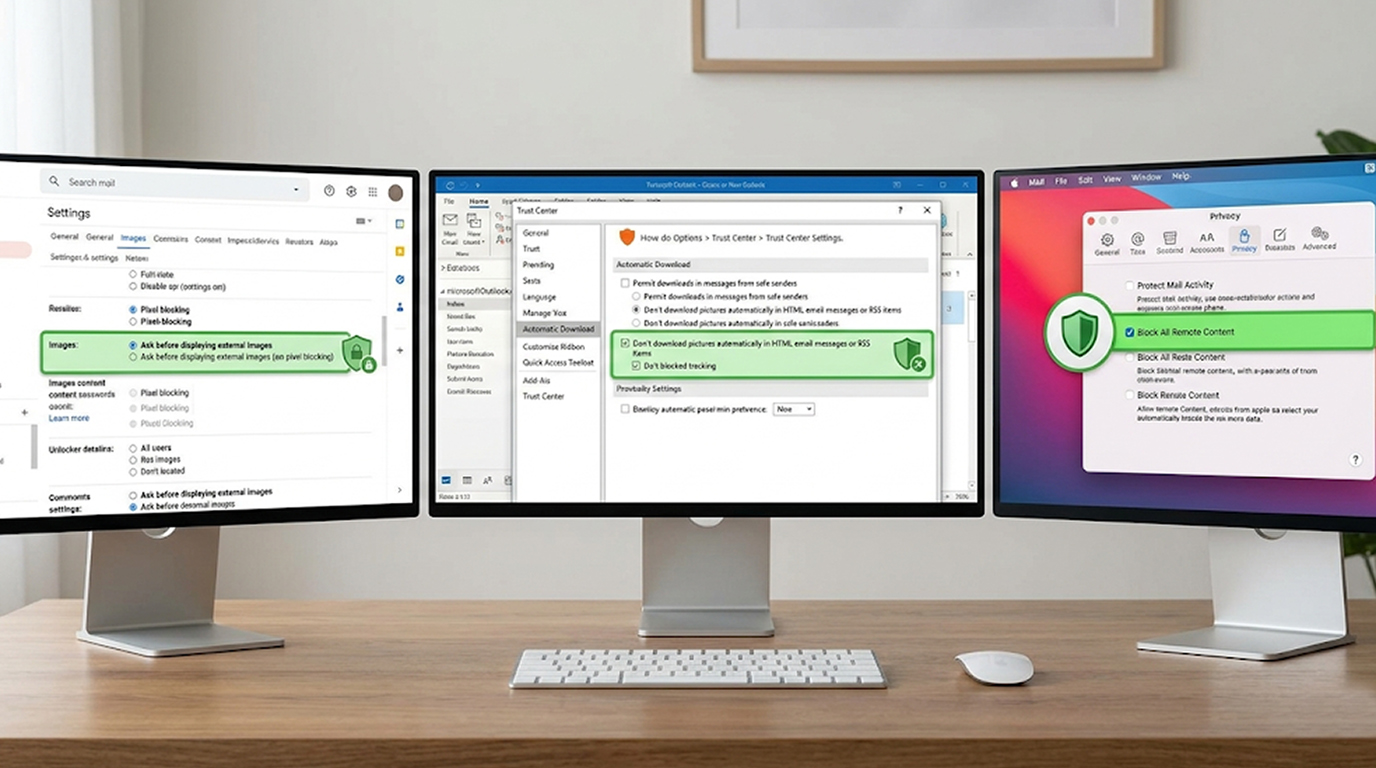
Invisible web bugs (or tracking pixels/beacon images) are helpful for sending notifications to the sender upon opening the email by inserting tiny visuals...
A China-aligned threat actor has resumed targeting European government and diplomatic organizations after a two-year period of relative inactivity in the r...
An operation, codenamed REF1695, that has been financially motivated and active quietly since November 2023. In its use of fake software installers to deli...
If you’ve recently installed a “free offline AI tool,” “local AI code completer,” “smart AI trading assistant,” o...
According to cybersecurity investigations into an active attack on government organisations in Southeast Asia, there was a zero-day vulnerability in TrueCo...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067