PDF Forensics: Extracting Metadata & Hidden Payloads Like a Pro
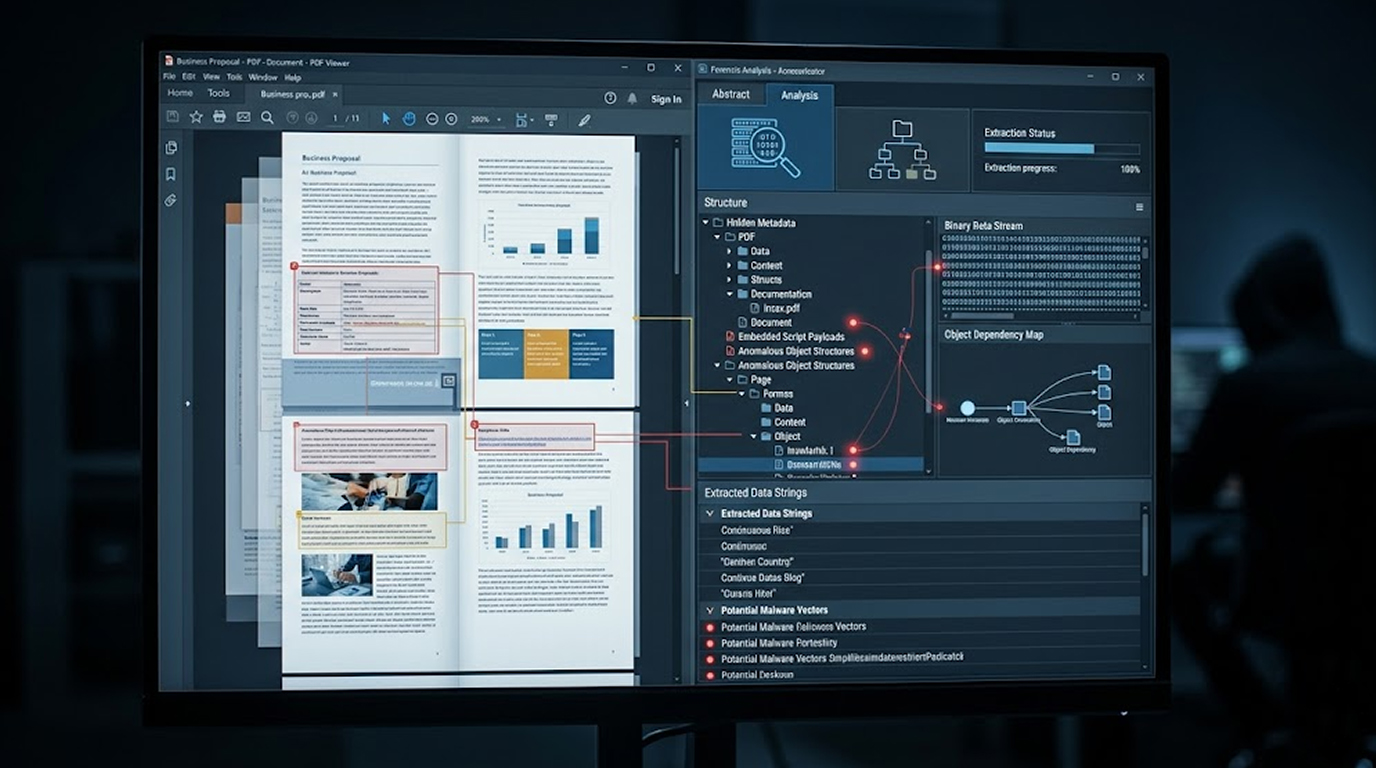
You receive a suspicious PDF. The file name says "Invoice.pdf." The sender is unknown. Your gut says something is wrong.You could delete it. Or you could i...
Found 18 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You receive a suspicious PDF. The file name says "Invoice.pdf." The sender is unknown. Your gut says something is wrong.You could delete it. Or you could i...
The creation of a hidden local admin account is one of the most effective persistence mechanisms utilized by both malware developers and red team practitio...
The number of malware infections on websites is not only increasing but also exploding exponentially. During 2025, the WordPress platform had 11,334 brand...
If you’ve cleaned your site of pharma spam only to see it return within days or weeks you’re not imagining things. The real culprit isn’t bad luck. It’s...
Website hacks are more sophisticated than ever. From infostealer malware campaigns exposing billions of credentials to targeted attacks on WordPress sites...
In 2026 the phrase “deepfake diplomat” is no longer a thought experiment or conference panel topic. It has appeared in real diplomatic cables,...
Malware sometimes deliberately triggers a Blue Screen of Death (BSOD) on Windows systems. It’s not a bug , it’s a tactic. The crash either hide...
Since January 2022, cybersecurity researchers have discovered an ongoing web skimming operation targeting businesses associated with some of the largest gl...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067