Laravel Lang PHP Supply Chain Attack Steals Credentials
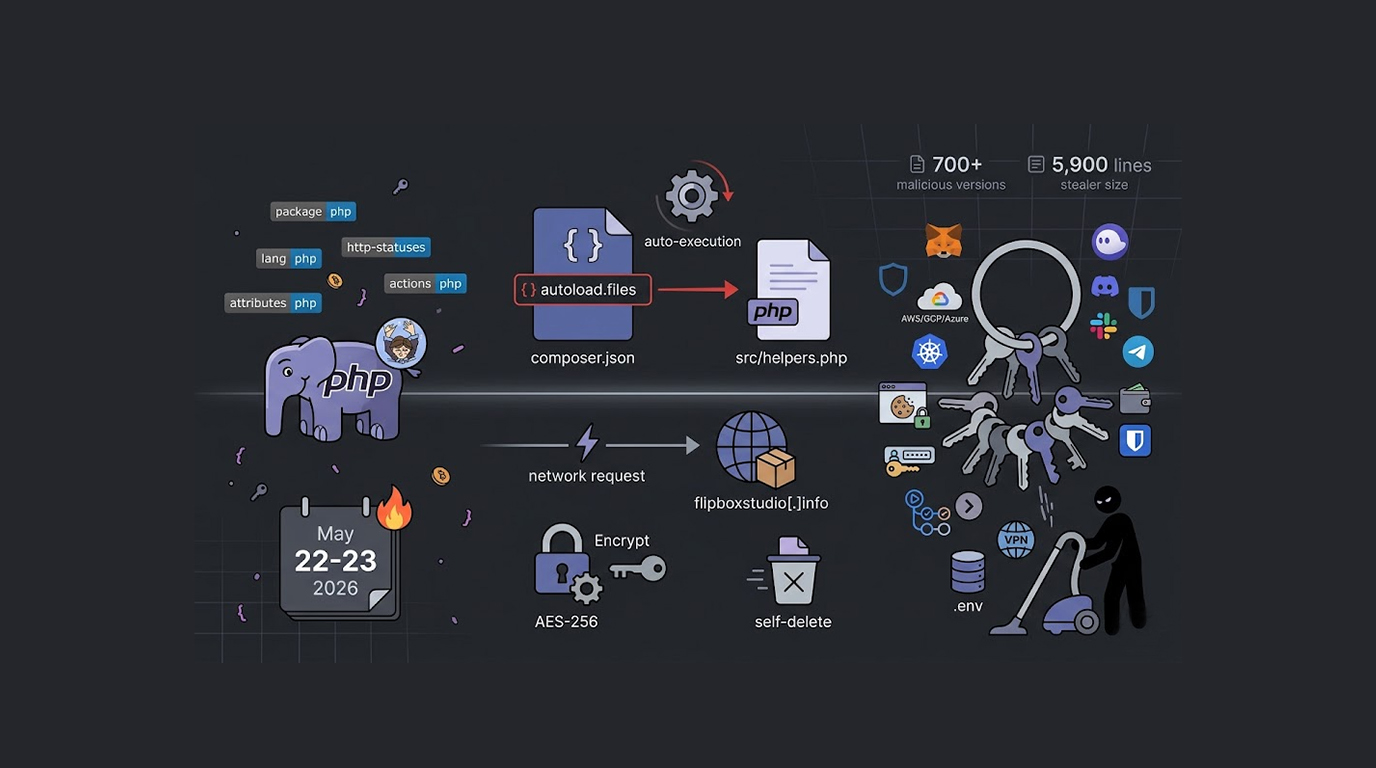
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
Found 23 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
Your network is set up like this, employees plug into the switch, servers plug into the same switch, everything can talk to everything, it is simple, it is...
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
Automated vulnerability scanners (OpenVAS, Nessus, Qualys, Nuclei, Nikto, sqlmap, etc.) are incredibly powerful, they scan fast, find thousands of potentia...
Running a vulnerability scanner often gives you a long list of findings. Many are low-priority noise, but a few high/critical issues appear again and again...
phpMyAdmin is convenient.That convenience is exactly why it ends up exposed to the internet.In many real incidents, phpMyAdmin was never meant to be public...
A new wave of GoBruteforcer (GoBrut) attacks has been discovered by Cybersecurity researchers targeting databases of Cryptocurrency and Blockchain Projects...
In critical infrastructure, IoT devices don’t just collect data.They open valves, regulate pressure, manage traffic, and balance power loads.These de...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067