YAMCS No Rate Limiting Allows Brute Force Attacks
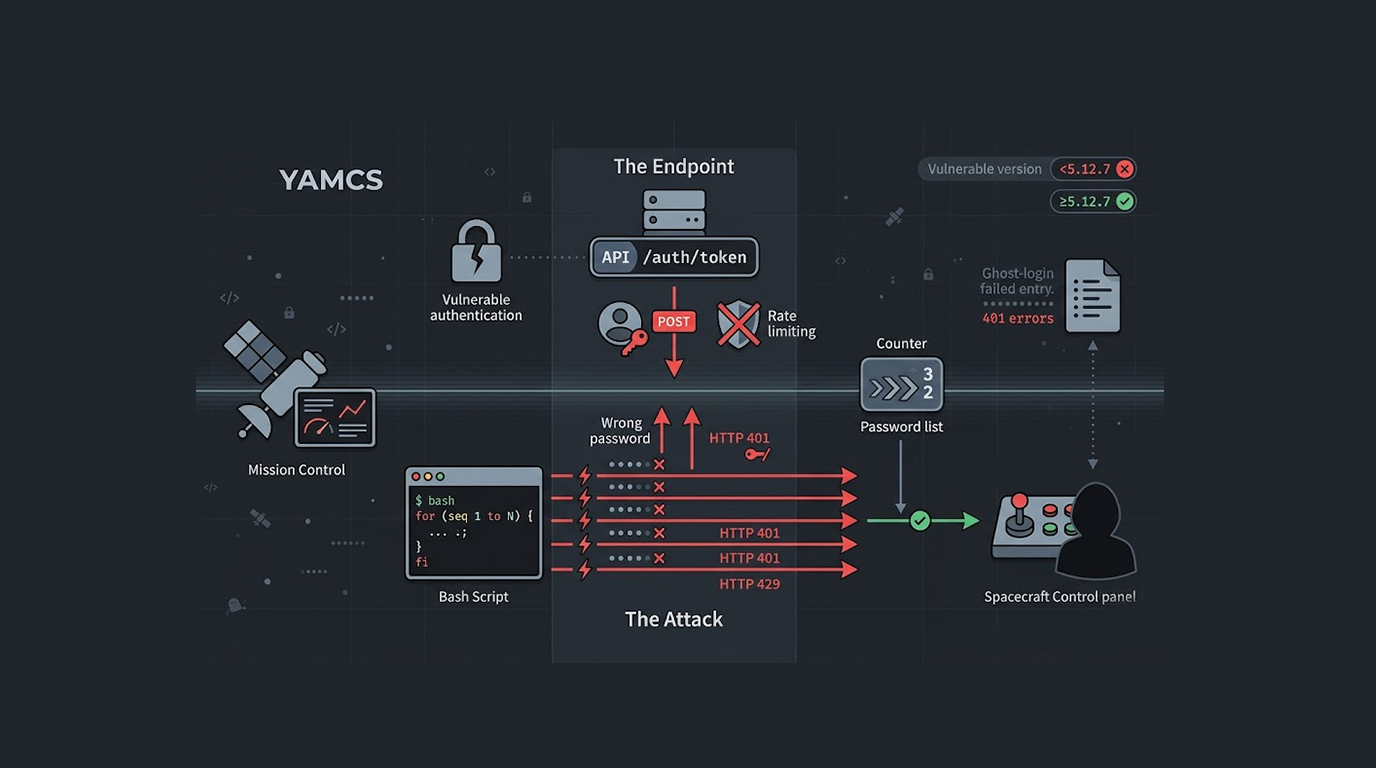
YAMCS contains an exploitable security vulnerability that allows endless brute-force attempts to log into the user accounts, meaning there is no limit on t...
Found 25 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
YAMCS contains an exploitable security vulnerability that allows endless brute-force attempts to log into the user accounts, meaning there is no limit on t...
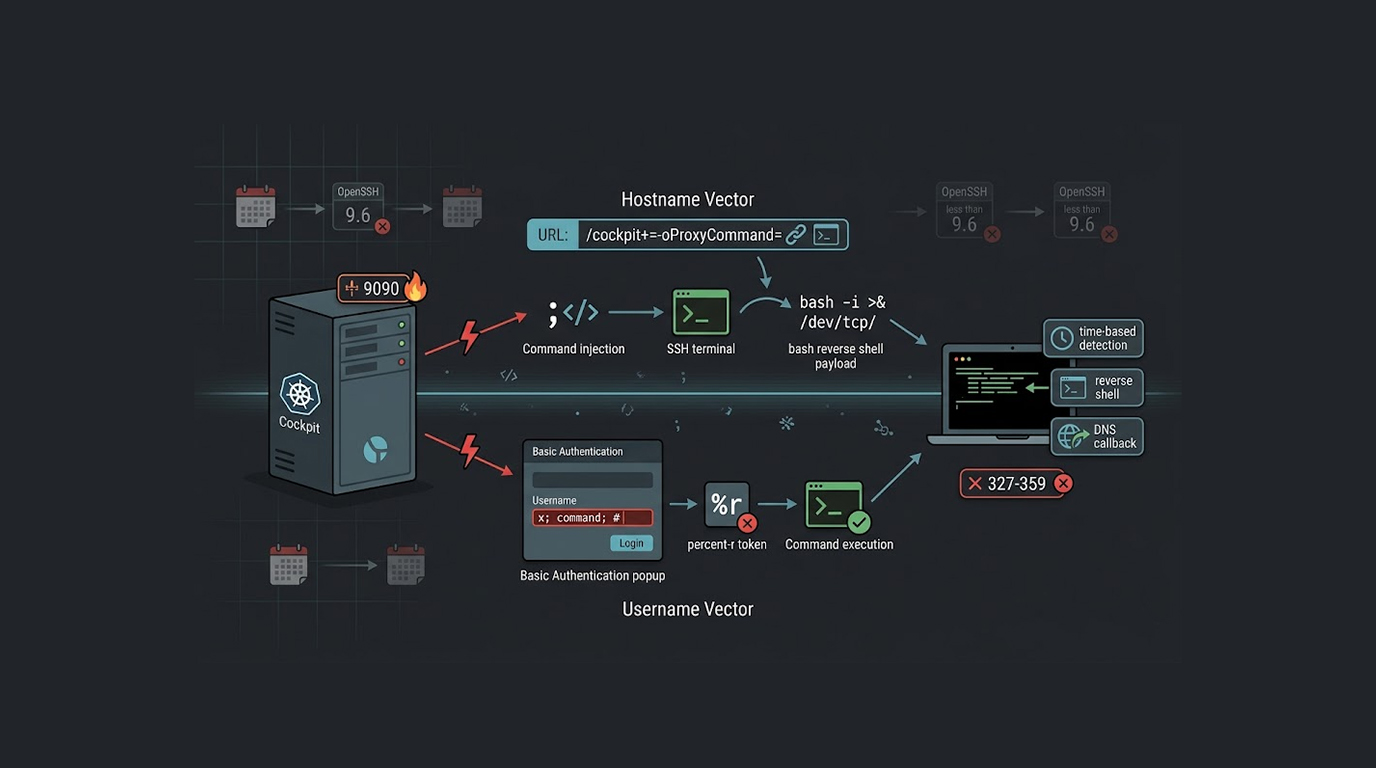
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
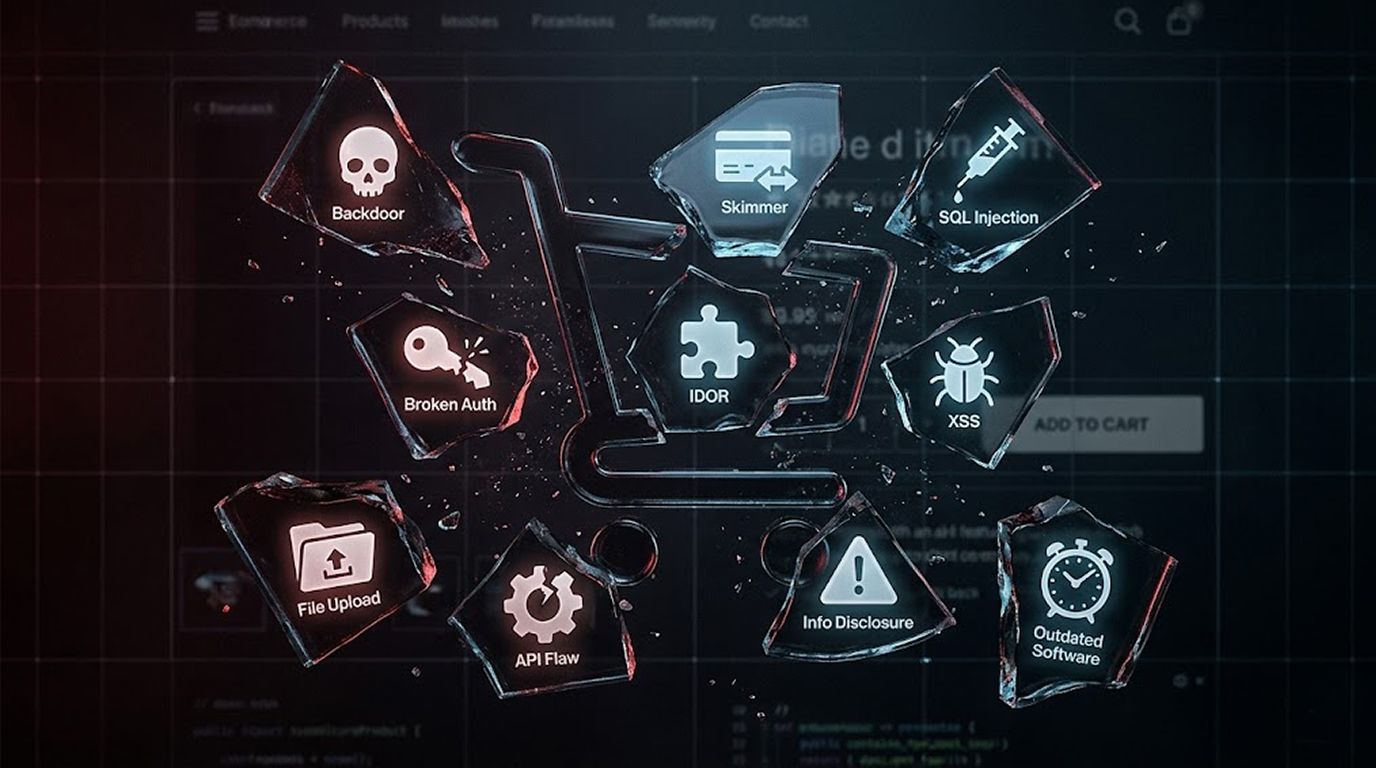
You spend thousands on marketing, you optimize your product pages, you run Facebook ads, you finally see sales rolling in.Then one morning you wake up to a...
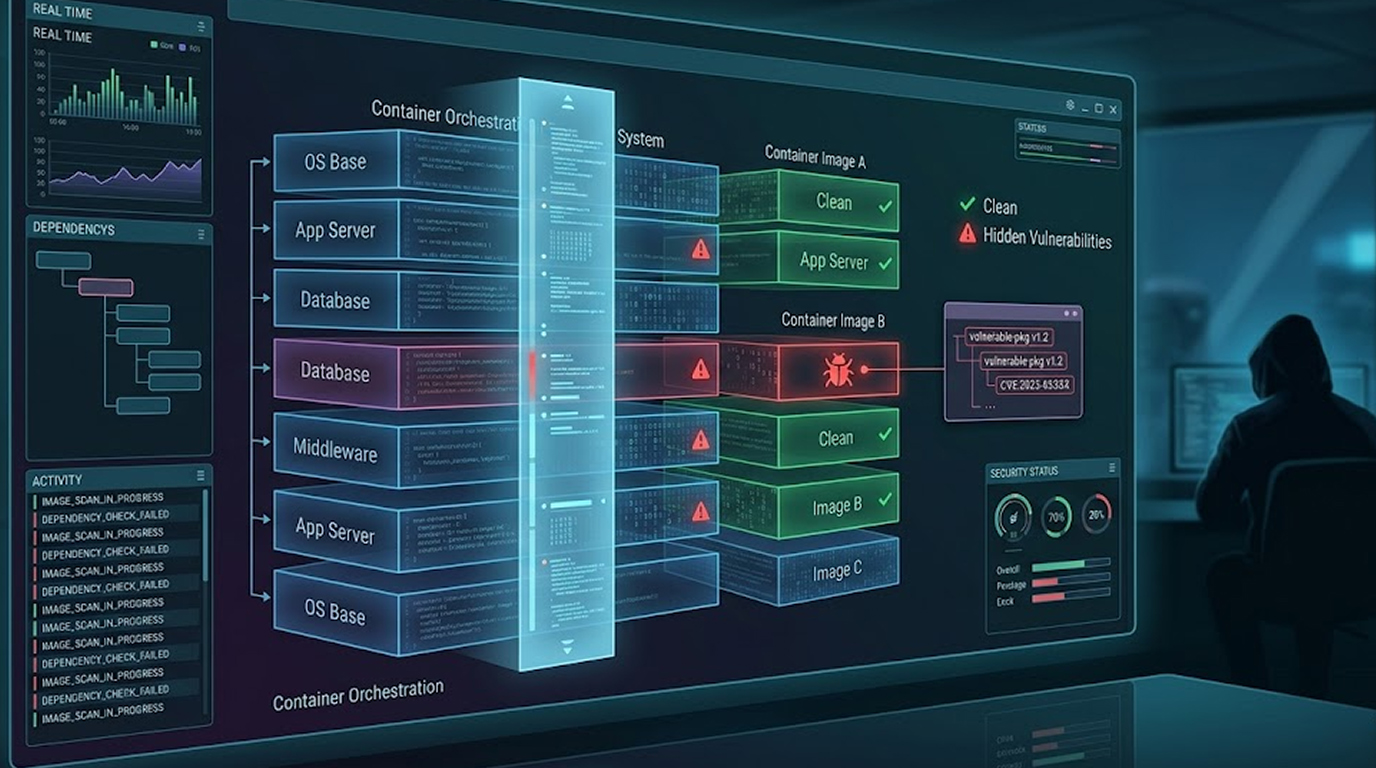
You built a Docker image, it runs perfectly, no errors, no warnings, you push it to your registryBut inside that image, there are vulnerabilities, old vers...
There is an increase in supply chain attacks against open-source packages in 2026. Hackers or other malicious actors will either publish or compromise pack...
Cybersecurity researchers have warned that cybercriminals are currently leveraging a serious remote code execution vulnerability in Flowise – a widel...
Ivanti disclosed and patched two high-severity (CVSS 9.8) code injection vulnerabilities (CVE-2026-1281 and CVE-2026-1340) affecting Ivanti Endpoint Manage...
OpenVAS (Open Vulnerability Assessment System) is one of the most widely used free and open-source vulnerability scanners available today. It is the commu...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067