The Process of Ransomware Attacks Explained
Ransomware is often treated as a sudden technical failure.In practice, encryption is usually the final move in a longer campaign.By the time systems are lo...
Found 185 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Ransomware is often treated as a sudden technical failure.In practice, encryption is usually the final move in a longer campaign.By the time systems are lo...
Threat actors do not rely on guesswork.They use simple, accessible tools to build an accurate picture over time. Open-source intelligence (OSINT) toolsThe...
New research by CloudSEK has found that a Cybercrime Group linked to the Chinese Government, Silver Fox, has started Phishing Campaigns against target user...
When credentials are stolen, the breach hasn’t happened yet.That moment is just access.What follows is quiet, and methodical, until it isn’t.At...
It Usually Starts SmallNo one wakes up and shuts down a city.It usually starts with something.A forgotten VPN account.An exposed remote desktop service.A c...
Most breaches don’t begin with malware detonating everywhere.They begin quietly.Someone logs in.They look around.They test limits.If you replay the l...
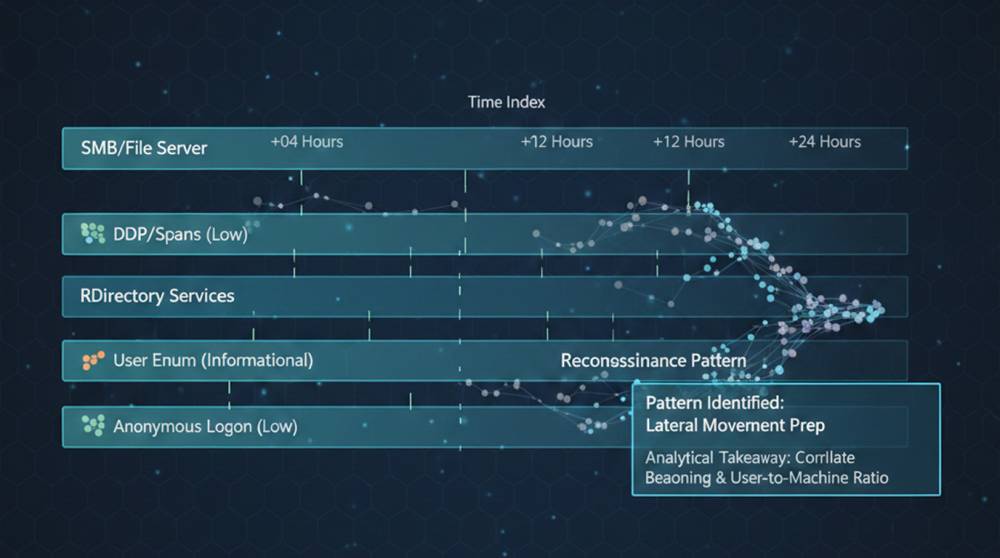
Network reconnaissance isn’t loud, it doesn’t trip alarms or crash systems, it’s someone looking around carefully, touching many things a...
Corporate networks usually look tidy on architecture slides.Clear zones, Strong boundaries and Logical flows. What “Hidden Paths” Really AreHi...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067