CISA Flags Active Exploitation of Gogs Path Traversal Flaw
The Cybersecurity and Infrastructure Security Agency (CISA) of the United States has now added the 'CVE-2025-8110' Path Traversal vulnerability in Gogs (a...
Found 185 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The Cybersecurity and Infrastructure Security Agency (CISA) of the United States has now added the 'CVE-2025-8110' Path Traversal vulnerability in Gogs (a...
phpMyAdmin is convenient.That convenience is exactly why it ends up exposed to the internet.In many real incidents, phpMyAdmin was never meant to be public...
Cybersecurity researchers have uncovered two key service-provider categories that supply online criminal networks with the tools, infrastructure, and autom...
Advanced attacks rarely fail because an exploit did not work.They fail because something felt wrong.APT groups succeed by blending into normal operations.G...
A group of hackers has recently launched new credential-harvesting attacks against people connected with a Turkish nuclear research agency, an EU-based thi...
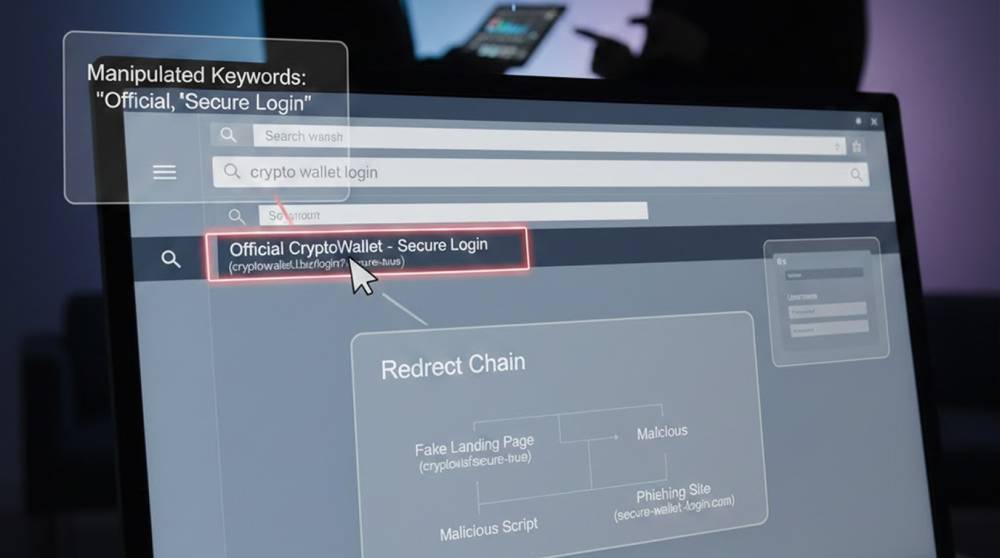
Some phishing campaigns never send a message.Instead of pushing links into inboxes, attackers wait for users to search.The trust comes from Google, not the...
What “Malware Free” Actually MeansNot all compromises involve payloads, binaries, or dropped files.Some of the most persistent incidents never...
Most serious incidents do not begin with malware or exploits.They begin with a valid login.Once attackers authenticate, their objective changes.The questio...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067