PDF Forensics: Extracting Metadata & Hidden Payloads Like a Pro
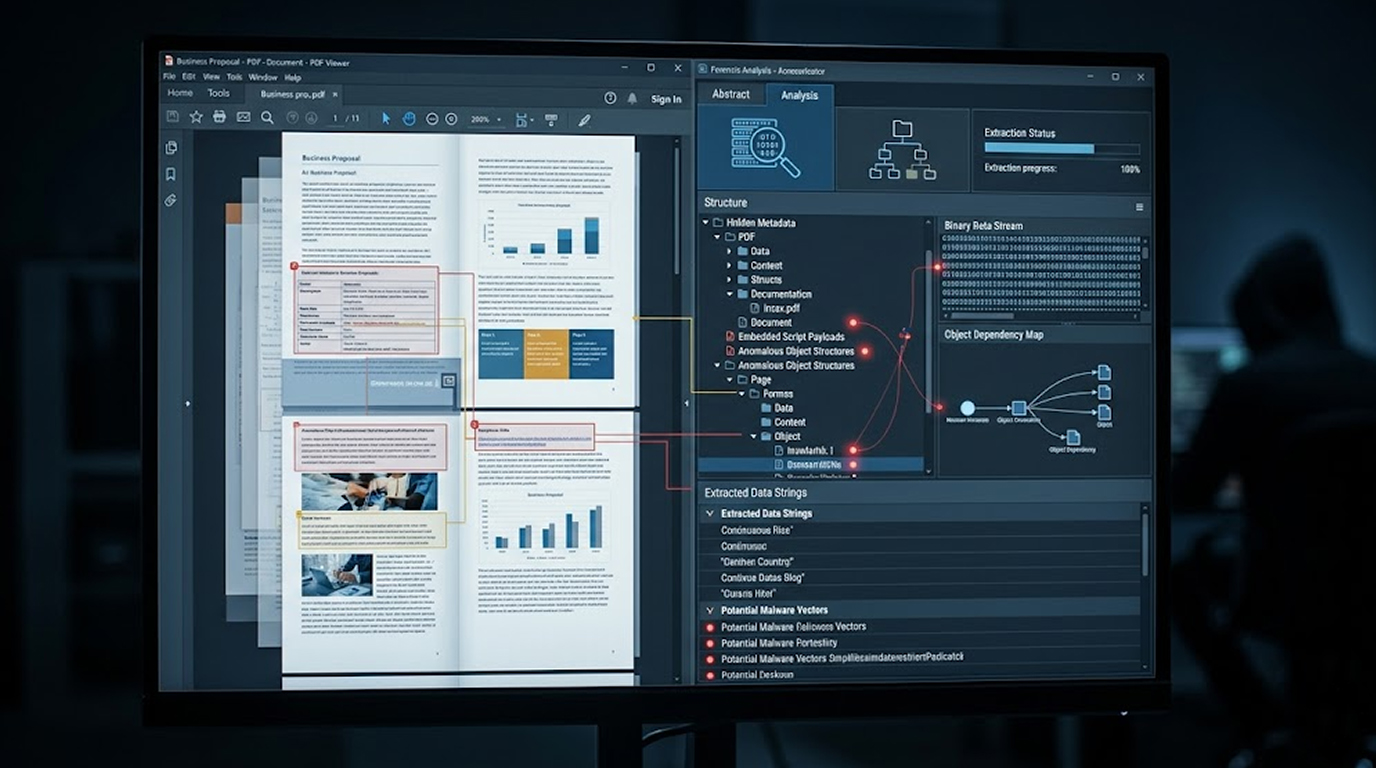
You receive a suspicious PDF. The file name says "Invoice.pdf." The sender is unknown. Your gut says something is wrong.You could delete it. Or you could i...
Found 200 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You receive a suspicious PDF. The file name says "Invoice.pdf." The sender is unknown. Your gut says something is wrong.You could delete it. Or you could i...
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
In 2026, malware developers are becoming interested in Zig due to its use as a modern day replacement for C as a systems programming language. Whereas legi...
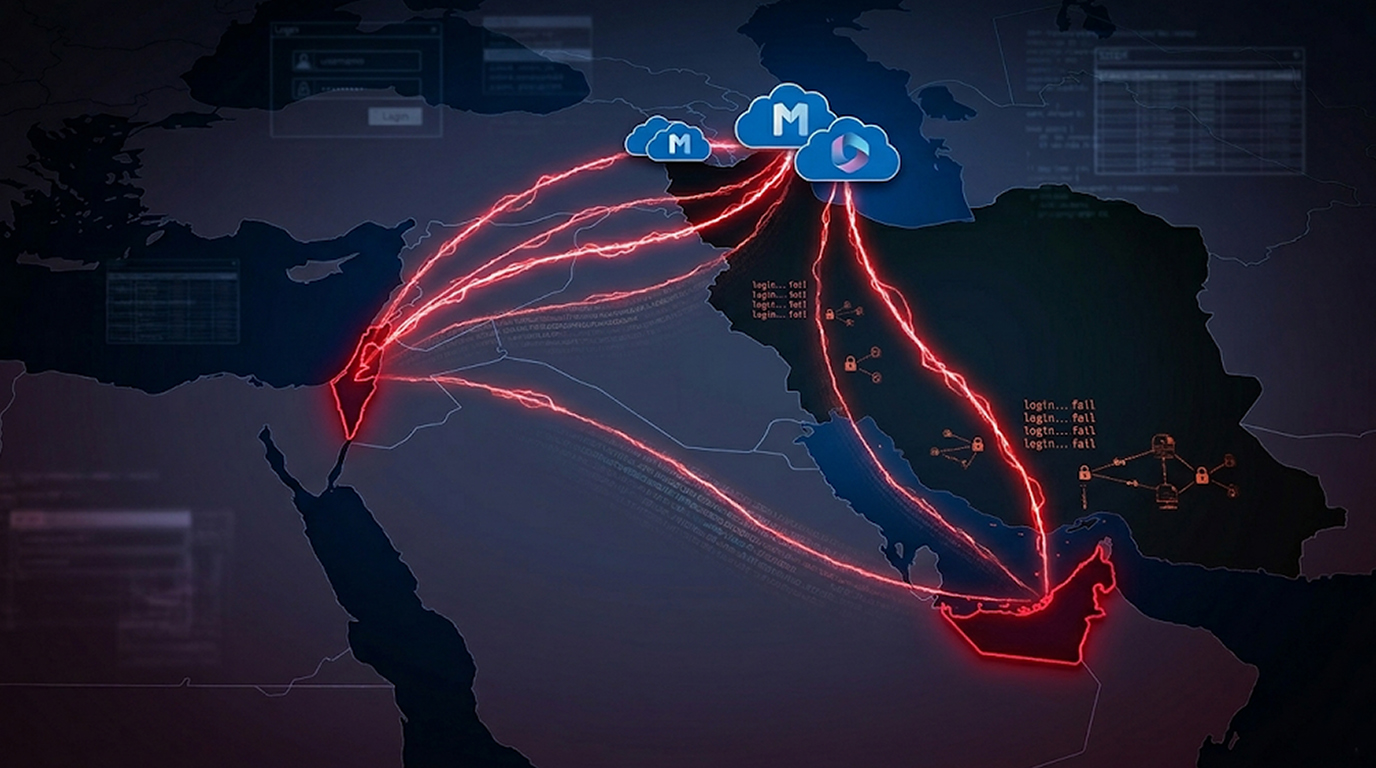
In March 2026, a threat actor aligned with Iran has conducted password-spraying attacks on Microsoft 365 accounts located in both Israel and the United Ara...
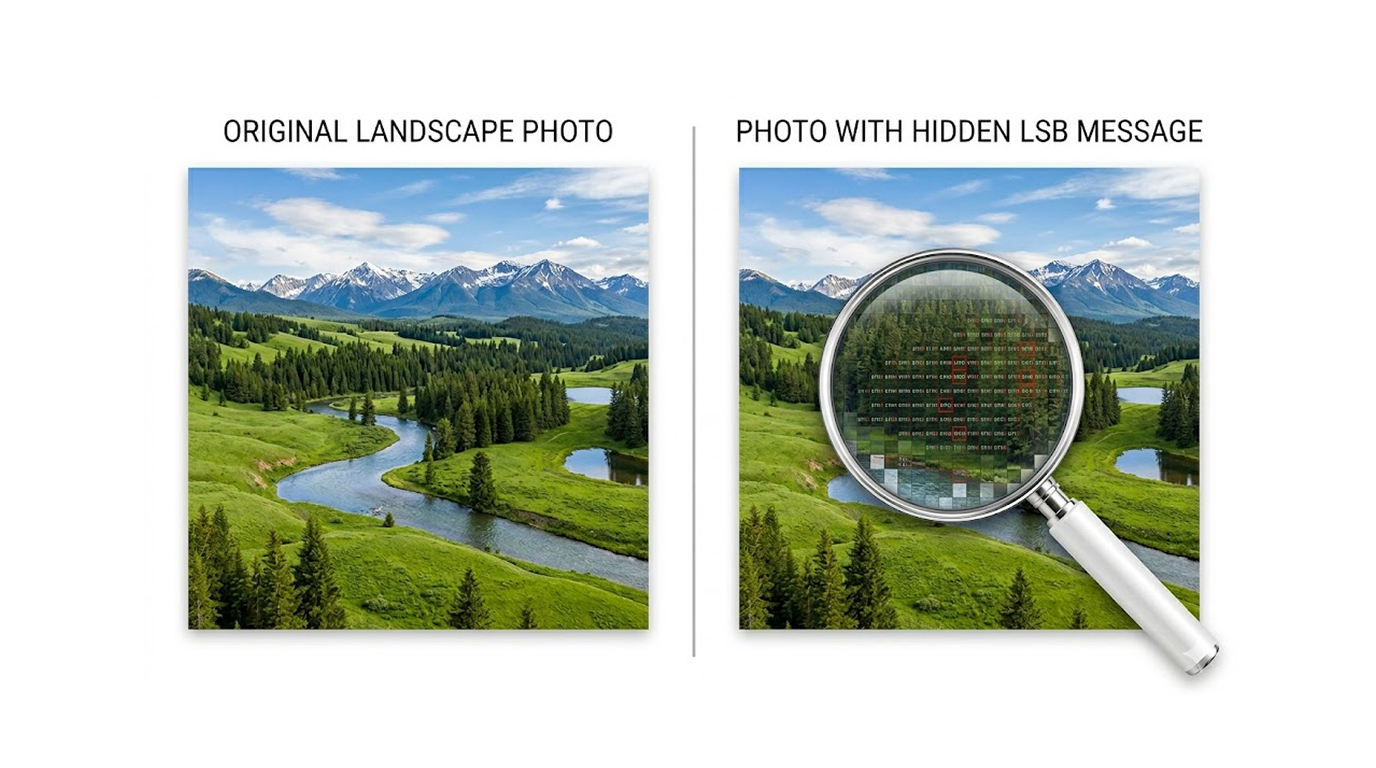
Steganography is a technique that hides an image/data in such a way that it appears innocent to an outside observer. Unlike encryption, where an encrypted...
On Friday, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced that they have added a significant vulnerability of the F5 BIG-IP Acc...
Ethical hacking and penetration testing aren't just careers, they're mindsets. Whether you're reconning targets, chaining exploits, writing reports, or def...
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067