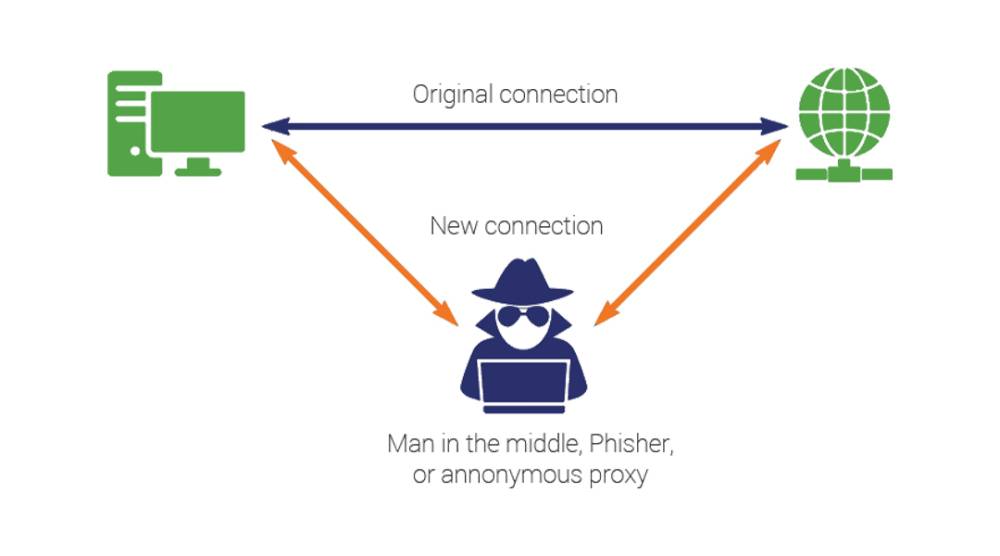
Man-in-the-Middle Attacks: How Cybercriminals Intercept Your Data
Man-in-the-Middle (MitM) attacks are a dangerous type of cyberattack where an attacker secretly intercepts and possibly alters the communication between tw...
Found 115 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Man-in-the-Middle (MitM) attacks are a dangerous type of cyberattack where an attacker secretly intercepts and possibly alters the communication between tw...
Cross-Site Scripting (XSS) attacks are among the most common and dangerous types of security vulnerabilities found in web applications. XSS attacks occur w...
In today’s interconnected world, software is a critical tool for productivity, communication, and entertainment. However, not all software is safe. C...
As cloud computing becomes the backbone of modern digital infrastructure, the risk of cyberattacks targeting cloud environments has surged. Cloud attacks,...
As cars become more connected through modern technology, they also become more susceptible to a new kind of threat—car hacking. Cybercriminals are no...
In the vast realm of cybersecurity, hackers play diverse roles, each with distinct motivations, methods, and impacts. Understanding the different types of...
An advanced persistent threat (APT) group, likely affiliated with Iran’s Ministry of Intelligence and Security (MOIS), has emerged as a key player in...
In an era where technology governs everything from personal devices to critical infrastructure, the threat of remote hacking extends far beyond data theft....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067