GitHub comments abused to push malware via Microsoft repo URLs
A GitHub flaw, or possibly a design decision, is being abused by threat actors to distribute malware using URLs associated with Microsoft repositories, mak...
Found 952 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A GitHub flaw, or possibly a design decision, is being abused by threat actors to distribute malware using URLs associated with Microsoft repositories, mak...
Key considerations for conducting ethical hacking experiments One of the fundamental considerations for conducting ethical hacking experiments is understa...
What if we told you… that the Bad “USB” attack could be performed… without the “USB” element of it, purely...
In this comprehensive video tutorial, we explore the realms of cybersecurity and ethical hacking, centering our focus on Whonix an influential anonymity-ce...
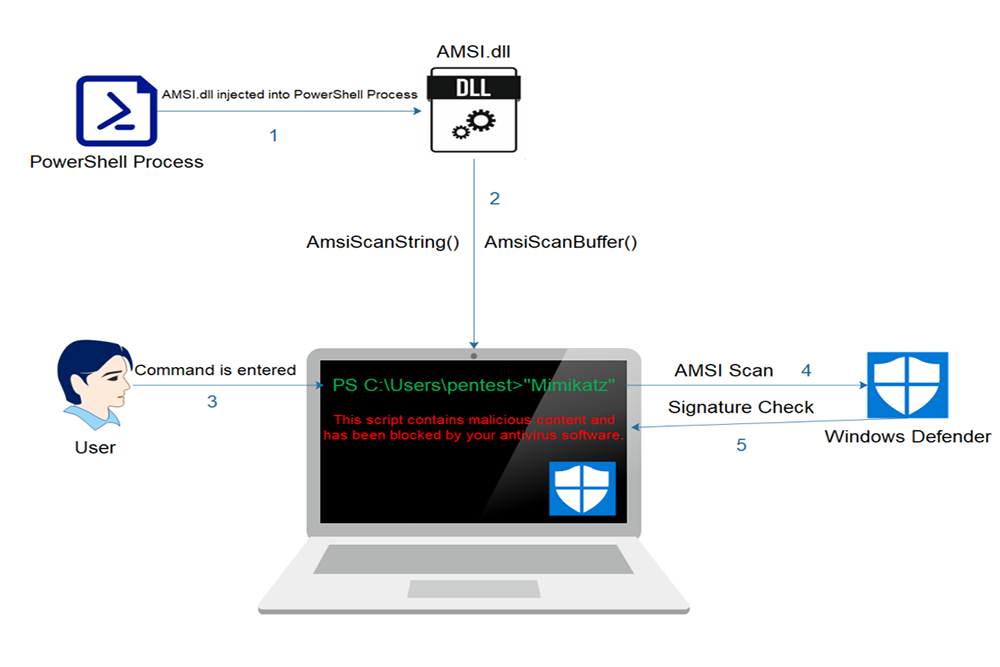
Introduction Windows developed the Antimalware Scan Interface (AMSI) standard that allows a developer to integrate malware defense in his application. AMS...
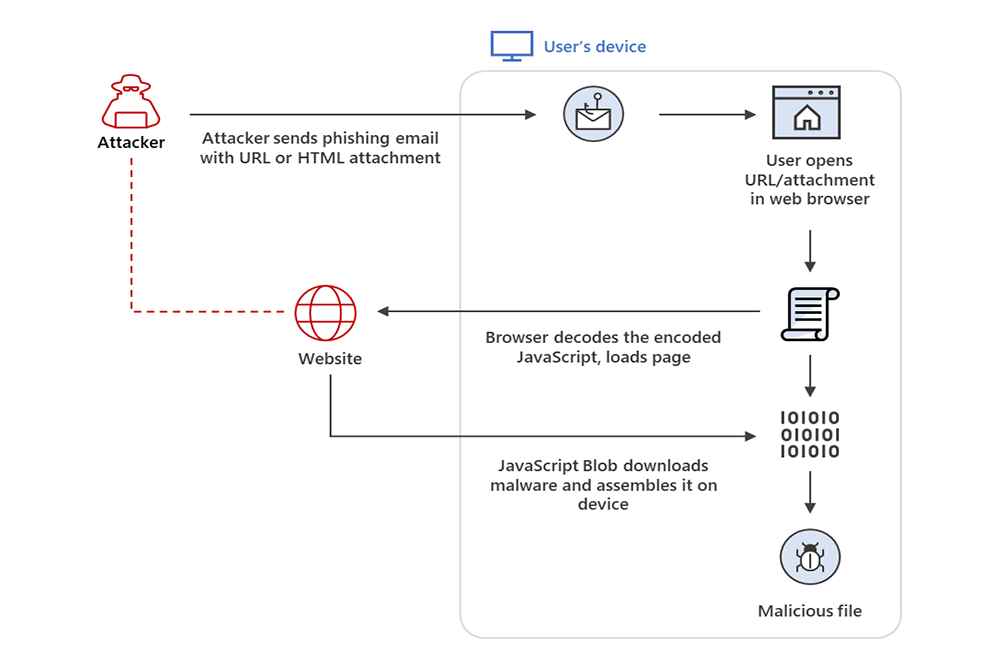
Introduction HTML Smuggling is an evasive payload delivery method that helps an attacker smuggle payload past content filters and firewalls by hiding mali...
Cybersecurity researchers have discovered a case of "forced authentication" that could be exploited to leak a Windows user's NT LAN Manager (NTLM) tokens b...
SSH is a widely used protocol for system administration and file transfer. In addition, it has a feature called SSH tunnelling (or SSH port forwardin...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067