Trivy vs Clair vs Anchore: Container Scanning Compared
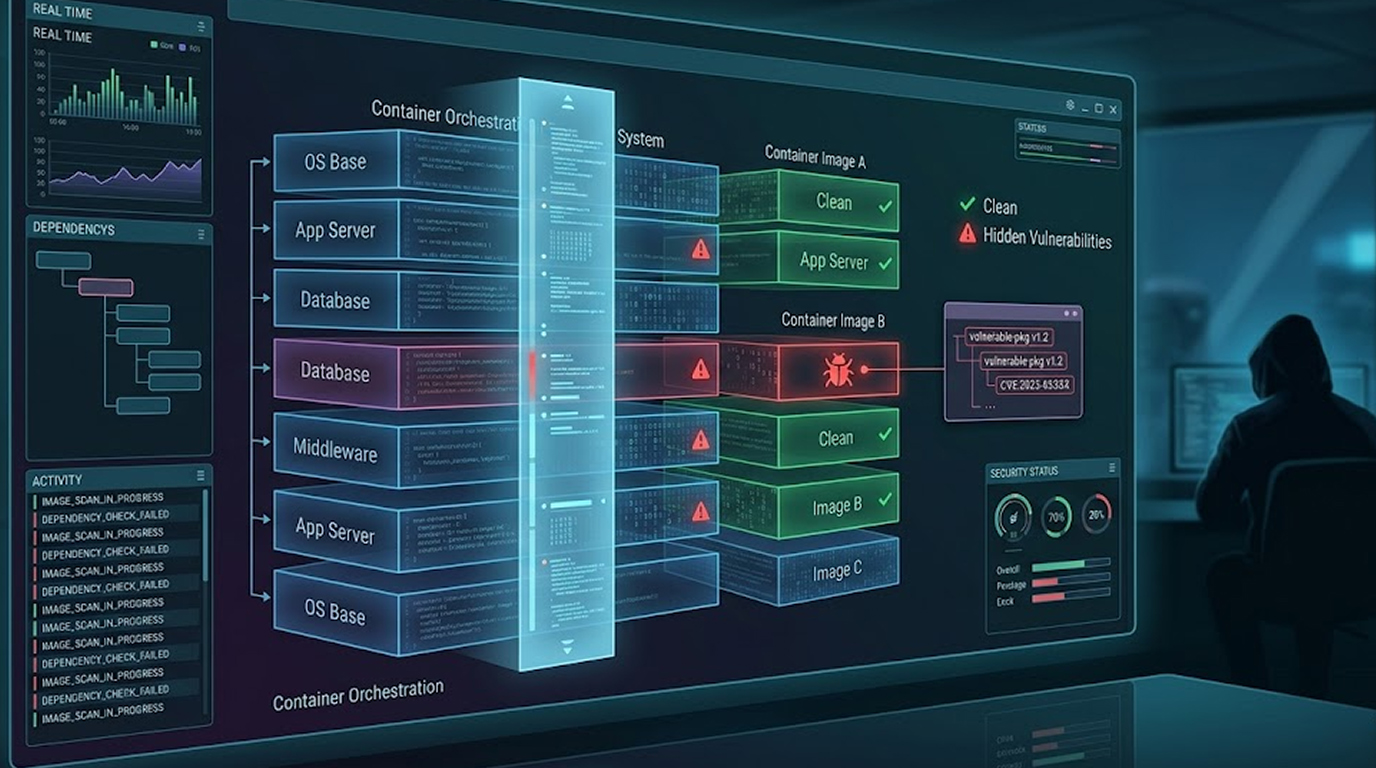
You build an image, you push it to a registry, you deploy it to production, and somewhere inside that image is a vulnerable package nobody noticed, sitting...
Found 9 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You build an image, you push it to a registry, you deploy it to production, and somewhere inside that image is a vulnerable package nobody noticed, sitting...
You built a Docker image, it runs perfectly, no errors, no warnings, you push it to your registryBut inside that image, there are vulnerabilities, old vers...
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
Ransomware is familiar. It locks files, demands payment, and disrupts operations.Most organizations now have at least a basic plan to deal with it. Wiper...
Cyber warfare isn’t just about networks anymore, it’s in the cloud.Critical infrastructure, enterprises, and governments rely on cloud services...
Most organizations have the misconception that after they migrate their workloads to a cloud service provider, their workloads will be secure. Unfortunatel...
Containers make life easier for developers, you can build an app, package it, and deploy it anywhere. But convenience comes with risk, Images can be tamper...
Cybersecurity researchers from Trend Micro have uncovered a malicious campaign in which attackers are targeting Docker remote API servers to deploy the SRB...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067