Oracle EBS Flaw: CVE-2026-101767 Under Attack
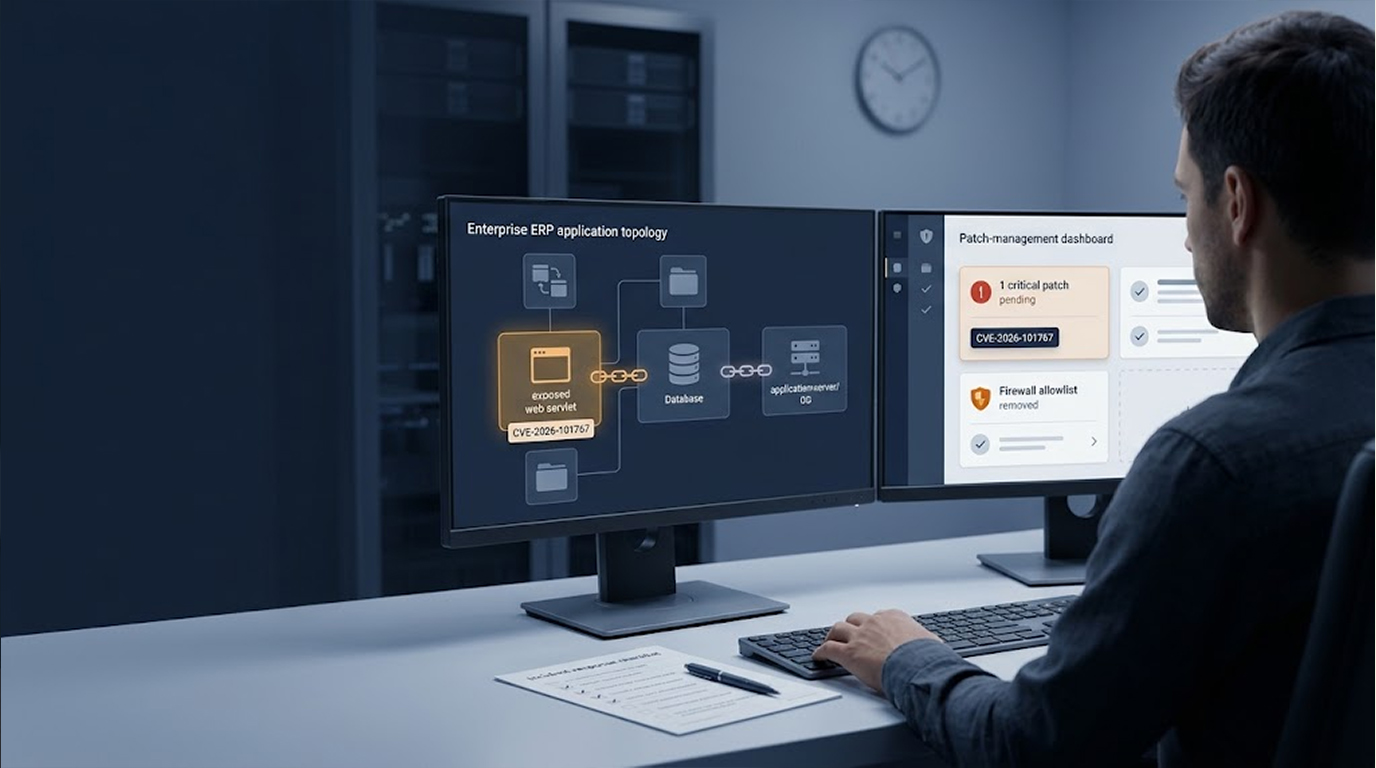
Threat actors are already probing for a newly patched critical vulnerability in Oracle E-Business Suite, because threat intelligence firm Defused Cyber jus...
Found 13 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Threat actors are already probing for a newly patched critical vulnerability in Oracle E-Business Suite, because threat intelligence firm Defused Cyber jus...
Your Dell storage infrastructure might be wide open to attackers right now, because Dell just dropped a bombshell security advisory, revealing six critical...
CISA added two security flaws to its Known Exploited Vulnerabilities catalog on Friday, citing evidence of active exploitation, and the two bugs are very d...
Imagine the AI code agent that is working in the sandbox. It is expected to remain there. It can read files, run commands, and help you code, but it should...
You spend millions on identity protection. Multi-factor authentication. Zero-trust architecture. Password policies. You feel secure. Then an attacker comp...
A critical severity vulnerability in the Progress Kemp LoadMaster load balancer has been added to CISA’s Known Exploited Vulnerabilities list. The ad...
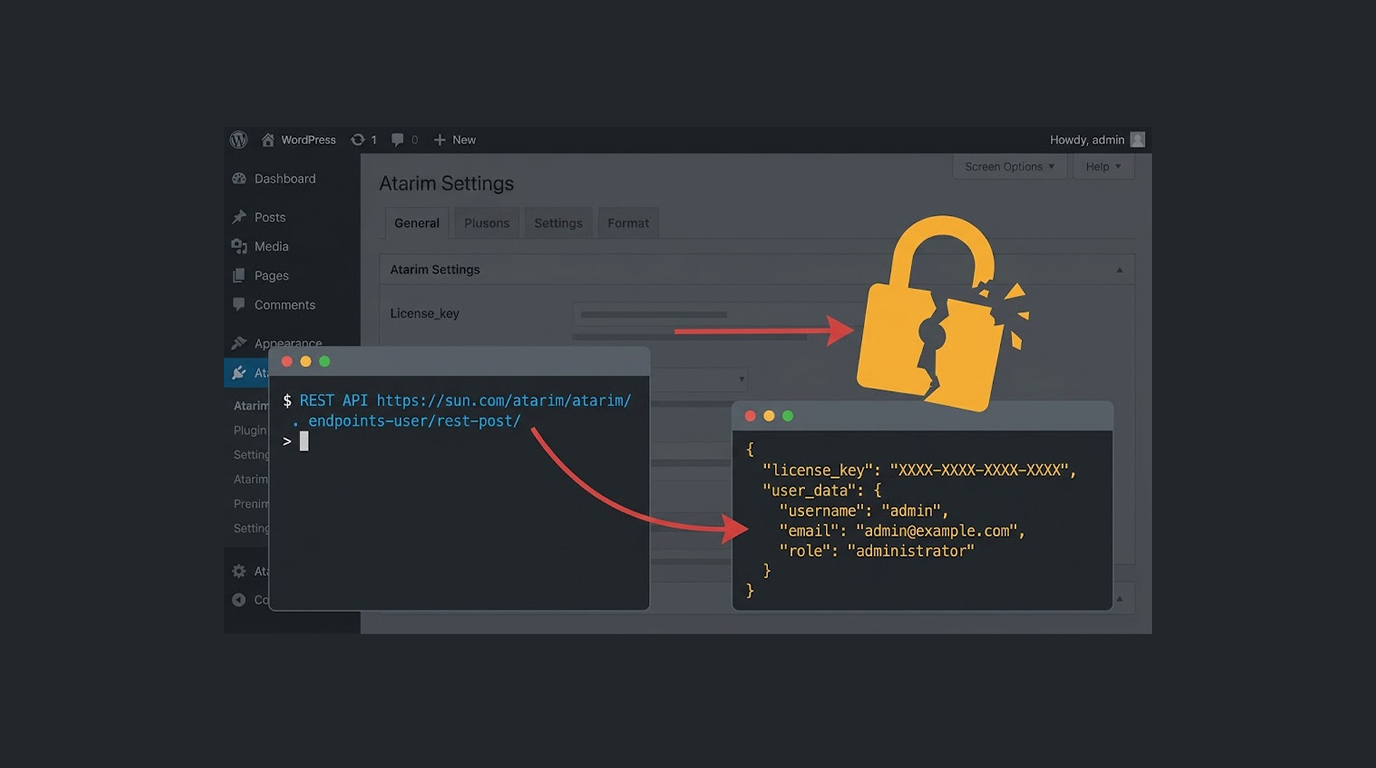
There exists a security vulnerability in the Atarim plug-in which exposes attackers to steal sensitive data without going through any kind of authenticatio...
Immediate action is necessary if you use the Gravity SMTP plugin for sending emails through WordPress, as there is currently a vulnerability being exploite...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067